Continuous Threat Exposure Management (CTEM) | SAFE
MEET SAFE X

Continuous Threat ExposureManagement (CTEM)

Your CTEM AI Co-Worker: From Findings to Fixes at Machine Speed.

Trusted By 10% of Fortune 500

  • T-Mobile
  • Fannie Mae
  • Verizon
  • Delta
  • Honeywell
  • S&P Global
  • HP
  • AAA
  • ADP
  • Chipotle
  • Snap Inc.
The Paradox

More data than ever before.
5x more disclosures than before.

The old way can no longer turn fragmented findings into prioritized action.

The Solution

Say Hello to the SAFE
CTEM AI Co‑Worker

SAFE CTEM AI Co-Worker is a command center for 100+ AI Agents. With built-in workflows, agents work in parallel across your Continuous Threat Exposure Management projects, completing weeks of work in days

Unified Risk Visibility

Create a de-duplicated exposure inventory of assets and exposures from tools that exist in your environment. Get zero drop architecture with zero data loss guarantee

Dynamic Risk-Driven Prioritization

Move away from CVSS. Prioritize exposures based on the industry’s most comprehensive prioritization engine with 25+ parameters

Scaled Exposure Management

Continuously reduce exposure across complex environments with 100+ AI Agents and built-in agentic workflows that keep teams aligned

The Architecture

How the SAFE CTEM
AI Co‑Worker Operates

Five stages. On loop.
A continuous, autonomous system that runs your Continuous Threat Exposure Management program with zero manual intervention.

Phase 1

Scoping

Industry's First Cyber Risk Quantification based Scoping Engine

The SAFE CTEM AI Co-Worker deploys a Scoping task force to define and continuously maintain scope around what matters most to the business.

The Asset Criticality Agent evaluates business context, data sensitivity, internet exposure, and other criticality signals for Continuous Threat Exposure Management

The Business Service Mapping Agent connects technical assets to revenue, critical applications, operational processes, and more

The Asset Tagging Agent enriches incomplete asset records across business unit, geography, ownership, application, and policy

The Scope Drift Agent continuously detects new workloads, exposure changes, and assets moving outside approved scope
Phase 2

Discovery

Industry's First Zero Drop Architecture with Zero Data Loss Guarantee

Discover, normalize, and deduplicate assets and findings across 150+ security tools and flexible connectors with zero data loss.

The Integration Sync Health Agent monitors connector health, sync status, and data freshness to prevent ingestion gaps in your CTEM program

The Shadow Asset Agent uncovers unknown and unmanaged assets missing from approved inventories creating complete exposure visibility

The Asset Deduplication Agent reconciles duplicate asset records across tools into a single, authoritative asset profile for a single, trusted exposure view

The Coverage Gap Agent identifies assets missing expected scanner, endpoint, cloud, or security-tool coverage in real time

Phase 3

Prioritization

Industry's Most Comprehensive Prioritization Engine with 25+ Parameters. Fully Dynamic

Prioritize exposures with finding scores that combine access, threat activity, exploitability, business impact, and compensating controls.

The Access Prioritization Agent evaluates reachability, internet exposure, network position, privilege, and attack paths for risk-driven exposure prioritization

The Threat Intelligence Agent reasons across active exploitation, available exploits, CISA KEV, malware, ransomware, and 100+ intelligence sources

The Business Impact Agent connects affected applications, services, data, and processes to cyber risk quantification for financial impact mapping

The Compensating Controls Agent determines whether existing defenses meaningfully reduce real-world risk with clear guidance

Phase 4

Validation

Industry's First AI-Driven Exploit Mutation and Validation Engine with 2000+ Active Exploits

Natively validate whether an exposure is reachable, exploitable, and inadequately mitigated, before it triggers patch deployment and remediation.

The Internet Exposure Validator confirms whether the vulnerable service is genuinely reachable from the internet in your enterprise environment

The Exploitability Validation Agent determines whether a credible exploit path exists for the asset, configuration, privileges, and environment

The Controls Efficacy Agent evaluates whether EDR, WAF, firewalls, segmentation, hardening, and identity controls would stop the attack

The False Positive Triage Agent continuously removes findings that do not apply to the actual environment streamlining your CTEM program

Phase 5

Mobilization

1000+ Agentic Workflow Templates. 100+ Agents to Ingest, Reason and Act

Mobilize the right resources to turn prioritized, validated exposures into owned, governed, measurable action, and drive meaningful risk reduction.

The Executive Reporting Agent communicates remediation progress, exceptions, and verified risk reduction to leadership

The Remediation Ticketing Agent creates context-rich tickets and continuously synchronizes progress across ServiceNow and Jira

The Patch Intelligence Agent connects prioritized findings to vendor guidance and available patch jobs, significantly reducing analyst effort

The Exception Agent governs risk acceptance through documented justification, controls, approvals, review dates, and expiry

Guided Demo

Want to take SAFE CTEM
AI Co‑Worker for a ride?

Take a self-guided demo

Choose Demo

Select a demo to view

More Demos Available

Unlock the full demo

In Action

Too much to read?

Watch our Continuous Threat Exposure Management (CTEM) solution in action.

Metrics

Get Measurable Impact
with SAFE CTEM AI Co‑Worker

99%

Reduction in
Critical Exposures, Daily

40%

Reduction in
Mean Time to Remediate (MTTR)

200%

Productivity improvement
for triage, ticketing & validation

The Proof

Machine‑Speed Defense.
Measurable Results.

Drives cyber resilience up while bringing down insurance costs

Automotive Retail USA

Read the Full Story

The Challenge

Carvana relied on multiple scanners, making it difficult to consolidate asset and vulnerability data. This created operational overhead, blind spots, and challenges in prioritizing vulnerabilities and communicating risk.

The Results

40%
lower
enterprise breach likelihood
25%
savings
in insurance premiums
200%
ROI
in < 9 months of operationalization

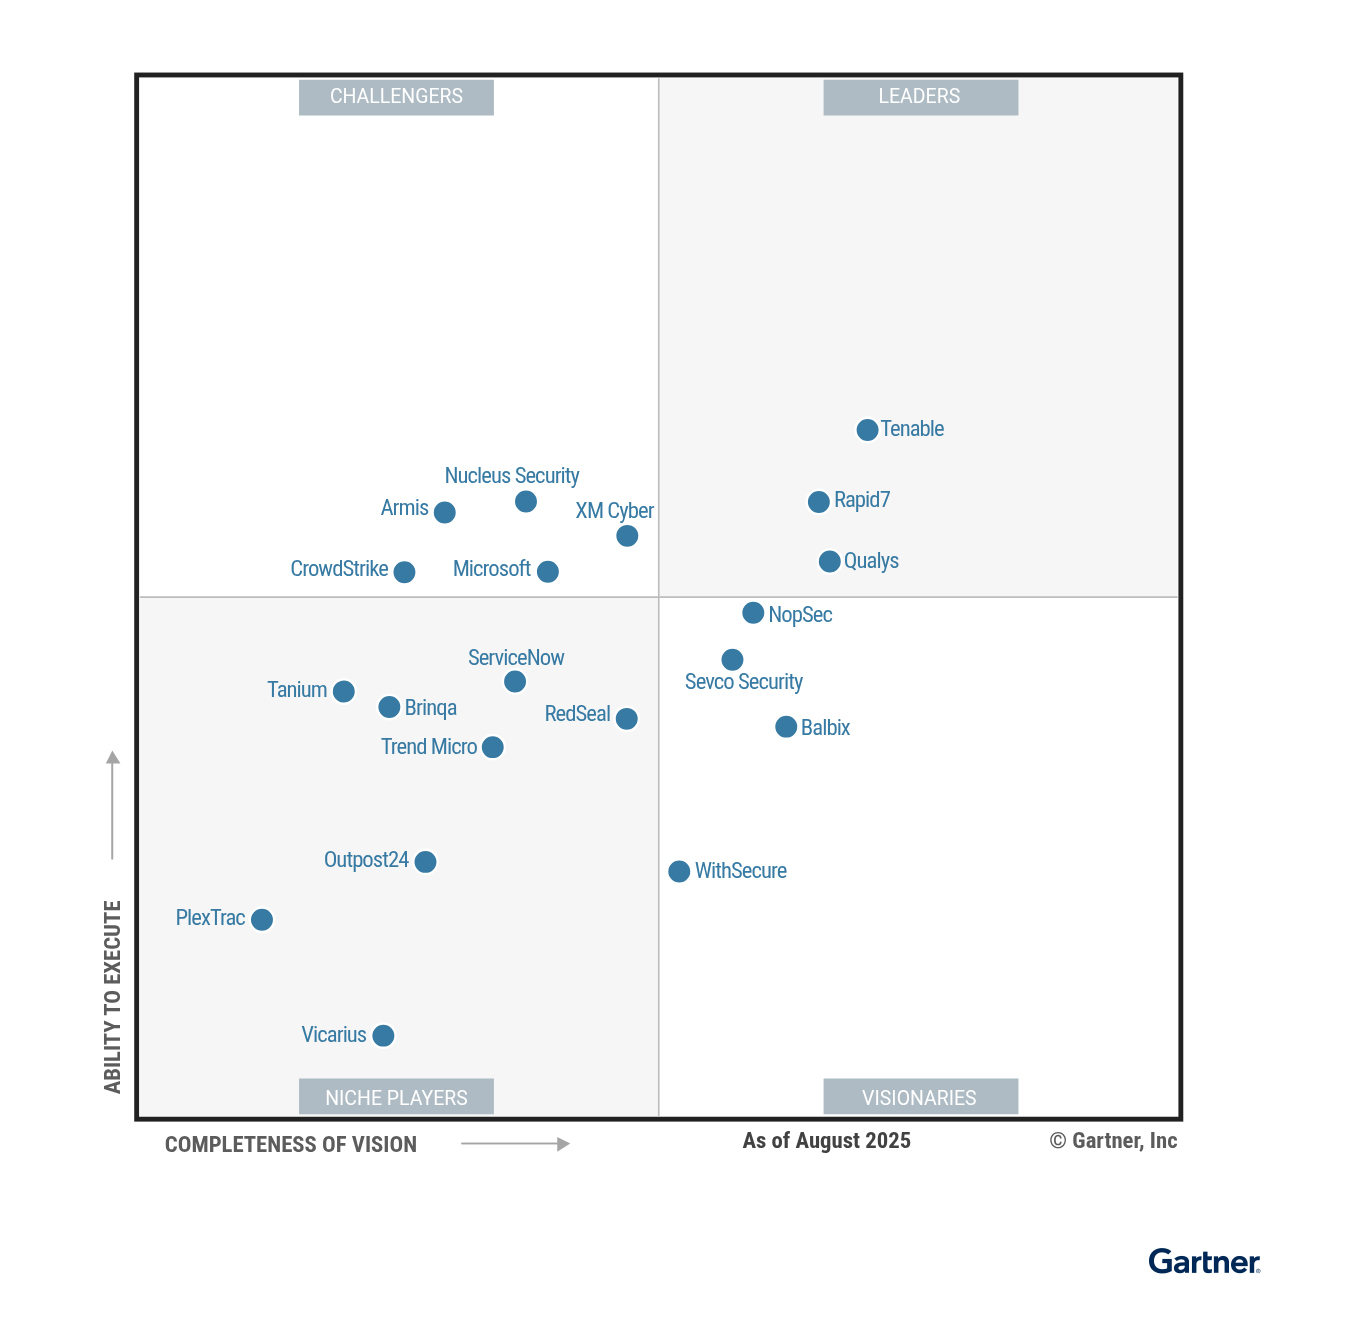
Endorsed by Leading Analysts

Book a demo

Ready to meet your
AI Co‑Workers?

Get a Demo