Continuous Threat Exposure Management (CTEM) | SAFE
MEET SAFE X

Continuous Threat ExposureManagement (CTEM)

Meet the SAFE CTEM AI Co-Worker: Scope, discover, prioritize, validate and mobilize in one continuous loop

Trusted By 10% of Fortune 500

  • T-Mobile
  • Fannie Mae
  • Verizon
  • Delta
  • Honeywell
  • S&P Global
  • HP
  • AAA
  • ADP
  • Chipotle
  • Snap Inc.
The Paradox

More data than ever before.
5x more disclosures than before.

The old way can no longer turn fragmented findings into prioritized action.

The Solution

Say Hello to the SAFE
CTEM AI Co‑Worker

SAFE CTEM AI Co-Worker is your AI colleague that leverages Agentic workflows and commands AI Agents to de-duplicate asset and finding data, prioritize them by exploitability and business impact, validate reachability and control effectiveness, and track remediation to verified closure.

It autonomously runs your CTEM program in one continuous loop, so you can manage exposures at machine speed.

Unified Risk Visibility

Create a de-duplicated exposure inventory of assets and exposures from tools that exist in your environment. Get zero drop architecture with zero data loss guarantee

Dynamic Risk-Driven Prioritization

Move away from CVSS. Prioritize exposures based on the industry’s most comprehensive prioritization engine with 25+ parameters

Scaled Exposure Management

Continuously reduce exposure across complex environments with 100+ AI Agents and built-in agentic workflows that keep teams aligned

The Architecture

How the SAFE CTEM
AI Co‑Worker Operates

Five stages. On loop.
A continuous, autonomous system that runs your Continuous Threat Exposure Management program with zero manual intervention.

Phase 1

Scoping

Industry's First Cyber Risk Quantification based Scoping Engine

The SAFE CTEM AI Co-Worker deploys a Scoping task force to define and continuously maintain scope around what matters most to the business.

Assess Asset Criticality
Evaluate business context, data sensitivity, and internet exposure to identify the assets that matter most to your CTEM scope.

Connect Assets to Business Services
Autonomously trace technical assets to revenue, critical applications, and operational processes to reveal what an exposure could disrupt.

Enrich Asset Records
SAFE CTEM AI Co-Worker fills gaps in business unit, geography, ownership, application, and policy data to give every in-scope asset the context it needs.

Detect Scope Drift
Continuously catch new workloads, changing exposures, and assets moving beyond approved scope, so your CTEM program keeps pace with the environment.
Phase 2

Discovery

Industry's First Zero Drop Architecture with Zero Data Loss Guarantee

Discover, normalize, and deduplicate assets and findings across 150+ security tools and flexible connectors with zero data loss.

Keep Data Pipelines Healthy
Continuously check connector health, sync status, and data freshness, catching ingestion gaps before they create blind spots.

Uncover Shadow Assets
The Co-Worker autonomously discovers unknown and unmanaged assets missing from approved inventories as the attack surface changes.

Reconcile Duplicate Assets
Run Agentic workflows that match records across security tools into a single, authoritative profile for each asset and its exposures.

Expose Coverage Gaps
Detect assets missing expected scanner, endpoint, cloud, or other security tool coverage in real time, so teams can address what their tools may be missing.

Phase 3

Prioritization

Industry's Most Comprehensive Prioritization Engine with 25+ Parameters. Fully Dynamic

The SAFE CTEM AI Co-Worker autonomously recalculates exposure priorities across 25+ parameters as access, threats, business impact, and defenses change.

Prioritize by Access and Attack Path
Evaluate reachability, internet exposure, network position, privilege, and attack paths to identify which exposures an attacker could realistically use.

Correlate Threat Intelligence
Reason across active exploitation, available exploits, CISA KEV, malware, ransomware, and 100+ intelligence sources to keep priorities aligned with current threats.

Quantify Business Impact
Connect affected applications, services, data, and processes to cyber risk quantification, translating technical exposures into potential financial impact.

Account for Compensating Controls
Assess whether existing defenses meaningfully reduce real-world risk, with clear guidance on which exposures still need action.

Phase 4

Validation

Industry's First AI-Driven Exploit Mutation and Validation Engine with 2000+ Active Exploits

Natively validate whether an exposure is reachable, exploitable, and inadequately mitigated, before it triggers patch deployment and remediation.

Confirm Internet Reachability
Verify whether a vulnerable service can actually be reached from the internet in your enterprise environment.

Validate Exploitability
Assess the asset, configuration, privileges, and surrounding environment to determine whether a credible exploit path exists.

Evaluate Control Effectiveness
Check whether EDR, WAF, firewalls, segmentation, hardening, and identity controls would stop the attack.

Remove False Positives
Continuously filter out findings that do not apply to the actual environment, keeping remediation focused on validated exposures.

Phase 5

Mobilization

1000+ Agentic Workflow Templates. 100+ Agents to Ingest, Reason and Act

Mobilize the right resources to turn prioritized, validated exposures into owned, governed, measurable action, and drive meaningful risk reduction.

Show Verified Risk Reduction
Keep leadership informed of remediation progress, approved exceptions, and risk reduction confirmed after action is taken.

Synchronize Remediation Work
Create tickets with the exposure context teams need to act, then continuously sync progress across ServiceNow and Jira.

Connect Findings to Fixes
Match prioritized findings to vendor guidance and available patch jobs, reducing the research needed to move remediation forward.

Govern Risk Acceptance
Document the justification, controls, approvals, review dates, and expiry for every exception, so accepted risk remains visible and accountable.

Guided Demo

Want to take SAFE CTEM
AI Co‑Worker for a ride?

Take a self-guided demo

Choose Demo

Select a demo to view

More Demos Available

Unlock the full demo

In Action

Too much to read?

Watch our Continuous Threat Exposure Management (CTEM) solution in action.

Metrics

Get Measurable Impact
with SAFE CTEM AI Co‑Worker

99%

Reduction in
Critical Exposures, Daily

40%

Reduction in
Mean Time to Remediate (MTTR)

200%

Productivity improvement
for triage, ticketing & validation

The Proof

Machine‑Speed Defense.
Measurable Results.

Drives cyber resilience up while bringing down insurance costs

Automotive Retail USA

Read the Full Story

The Challenge

Carvana relied on multiple scanners, making it difficult to consolidate asset and vulnerability data. This created operational overhead, blind spots, and challenges in prioritizing vulnerabilities and communicating risk.

The Results

40%
lower
enterprise breach likelihood
25%
savings
in insurance premiums
200%
ROI
in < 9 months of operationalization

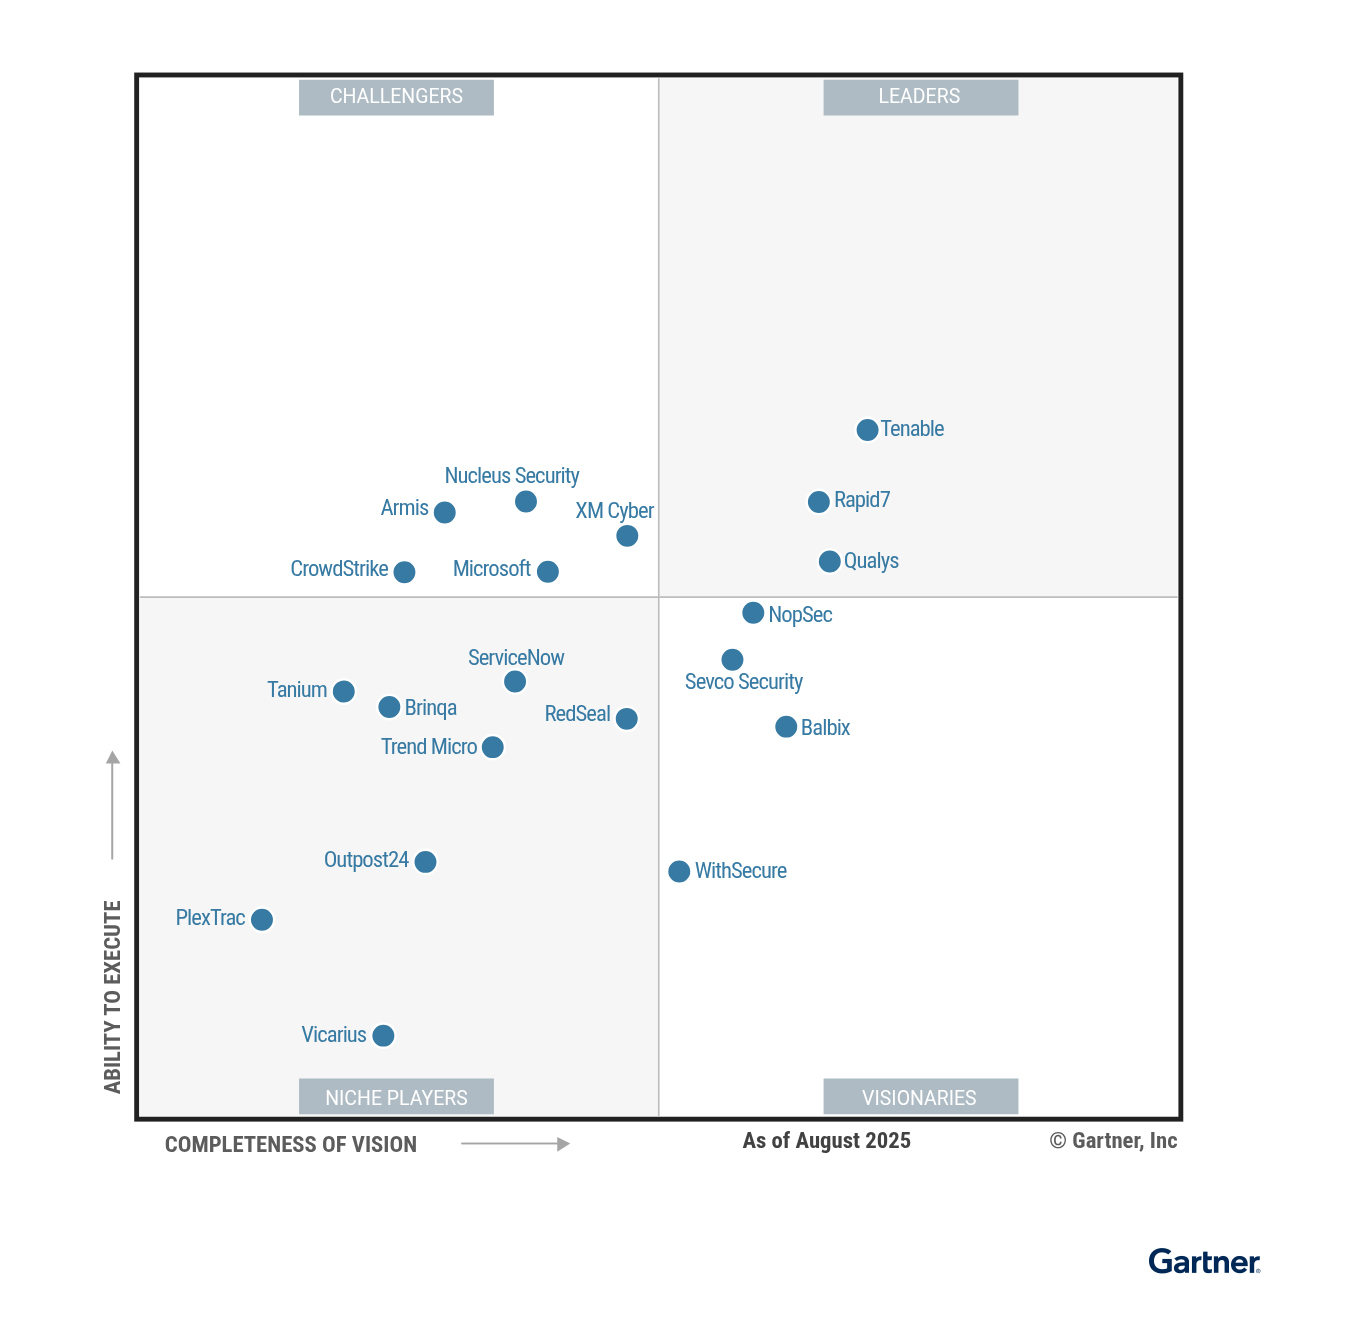
Endorsed by Leading Analysts

Book a demo

Ready to meet your
AI Co‑Workers?

Get a Demo