Healthcare Providers: Cyber Risk Management Solution - Safe Security

SAFE One for Healthcare Providers

Managing cyber risk in healthcare to serve patients better

The Paradox

Business Challenges

  1. Cyber incidents can quickly escalate into patient-safety events when clinical systems or service providers go offline

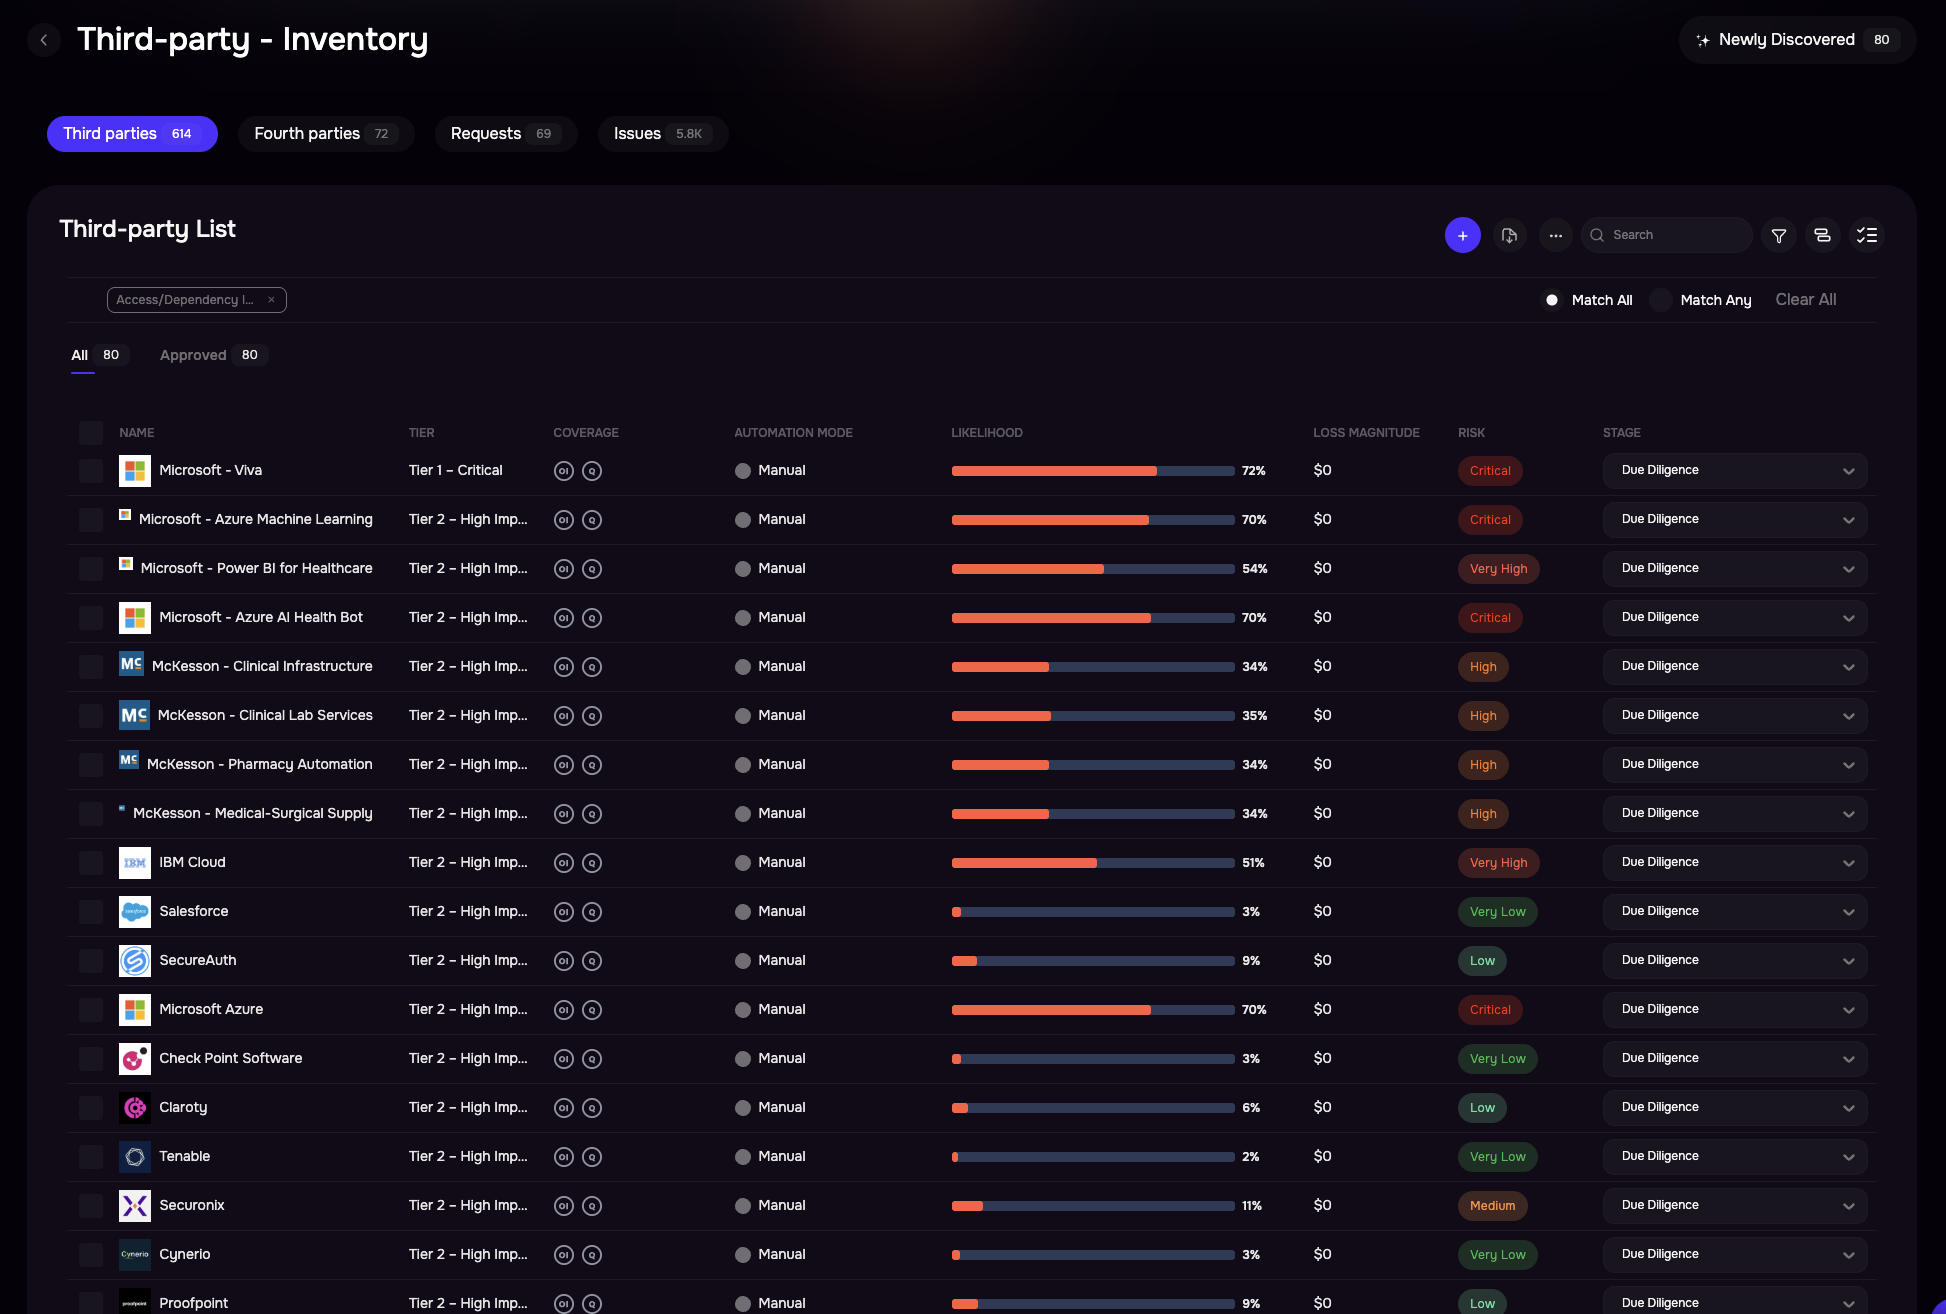
  2. Thousands of third parties and medical device suppliers create blind spots in PHI exposure and operational risk

  3. Third-party breaches trigger some of the largest care disruptions, financial losses, and regulatory investigations

  4. Security teams are small and overwhelmed compared to the size of their third-party ecosystem

  5. Complex regulations (HIPAA, ONC, CMS, FDA) demand fast and defensible evidence, but most lack auditable documentation

The Solution

Solution Highlights

Protect Patient Care. Strengthen Your Cyber Risk Management

Know, understand, and communicate cyber risk in real-time

Continuous visibility of risk across IoT clinical system, vendors, cloud partners, and more

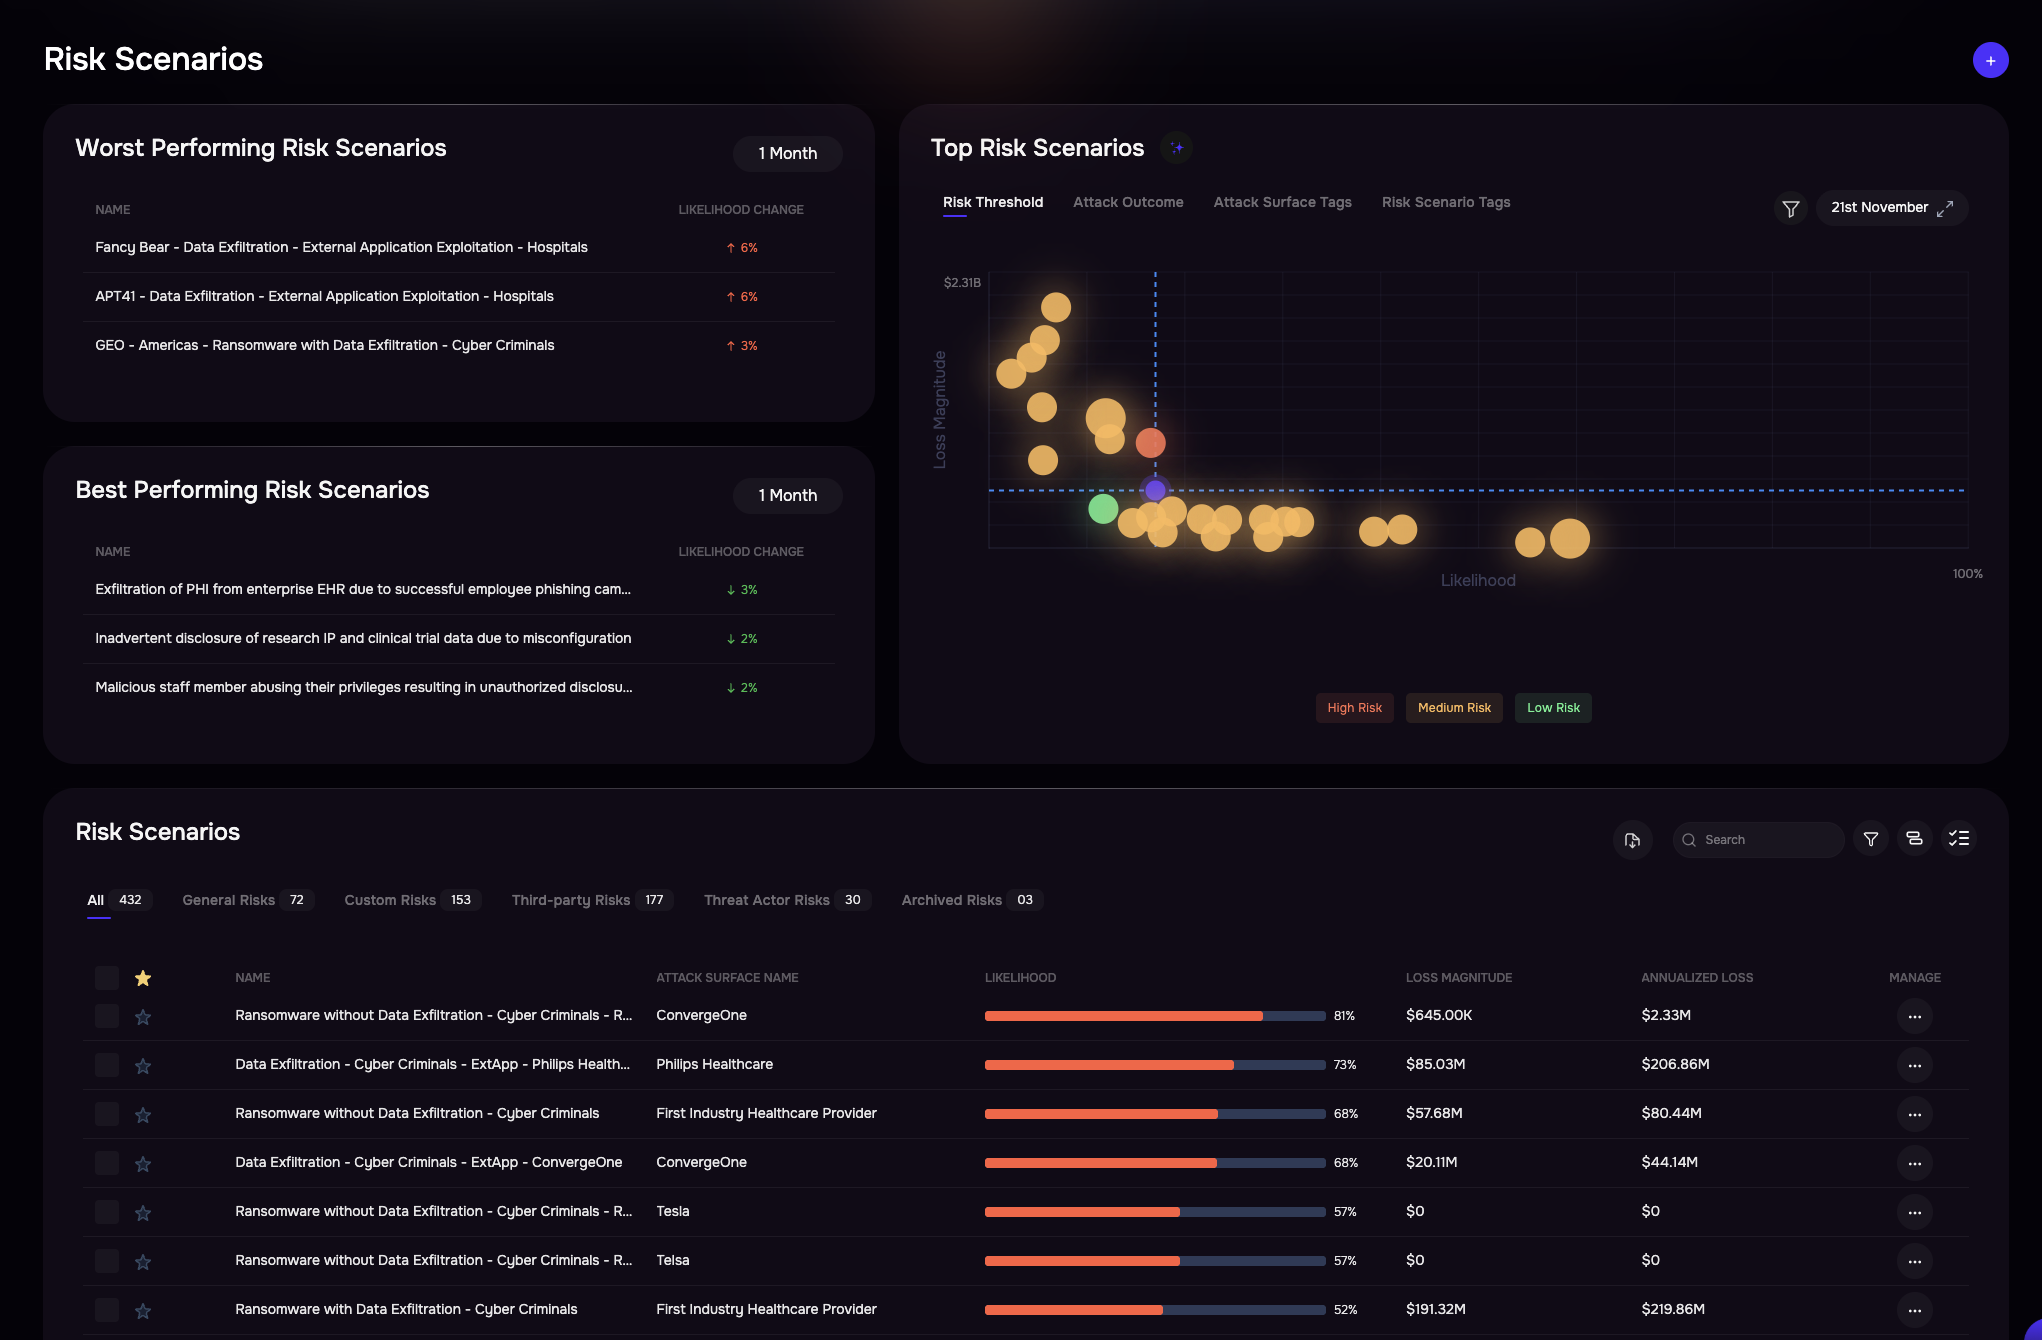
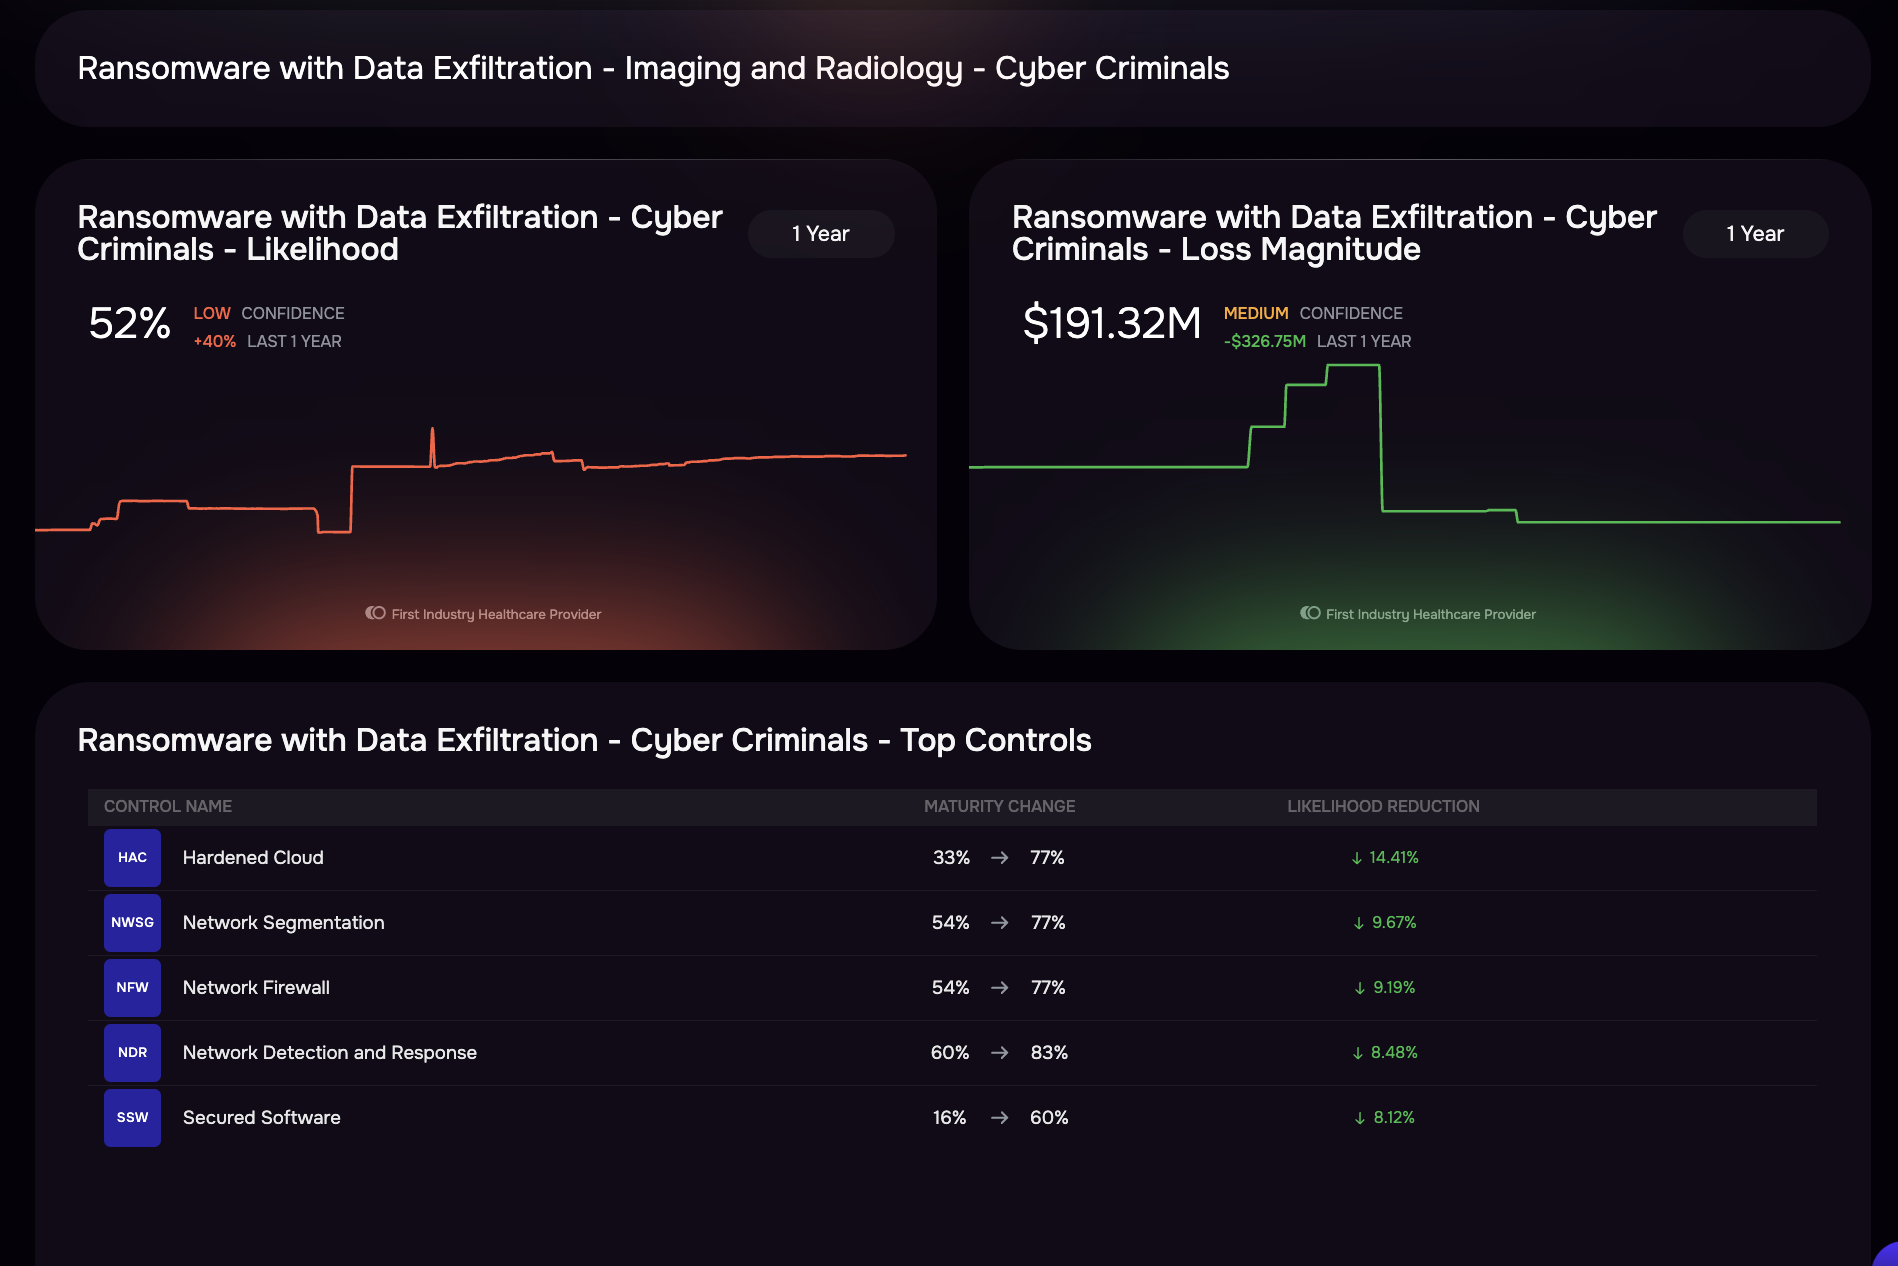
Map risk to disruptions from ransomware, system outages, data exfiltration of PHI

Effectively communicate the impact of cyber risk as financial loss to all stakeholders

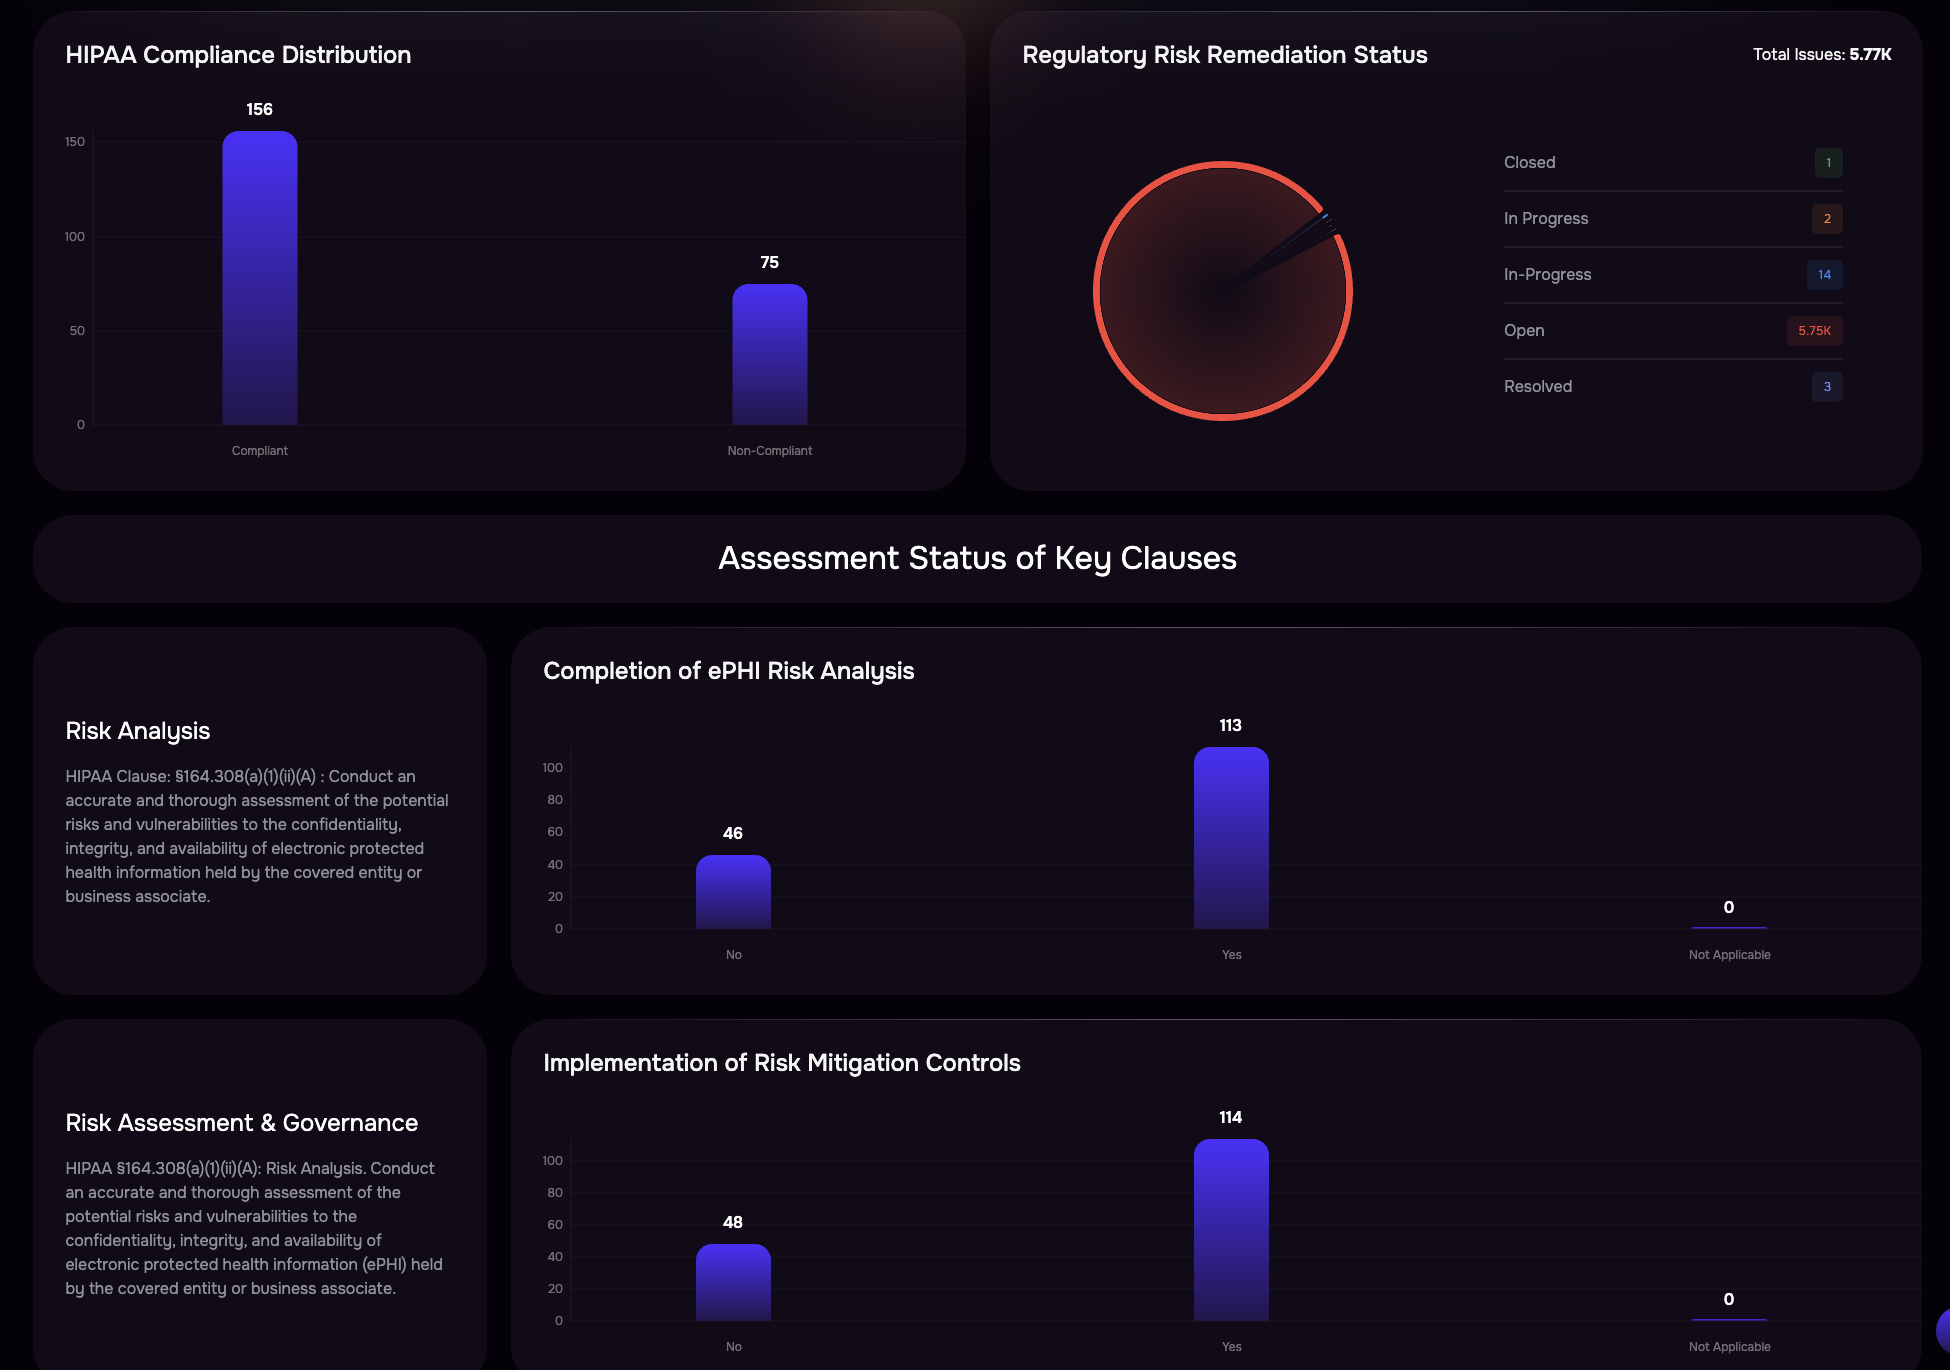
HIPAA Compliance SAFE

Meet and report compliance and regulatory requirements

Built-in, customizable compliance dashboards including HIPAA, Texas HB300, DORA, etc

Leverage AI-powered, prompt-based reporting to generate customized reports on the fly

Get audit and compliance-ready documentation to meet regulatory timelines & reduce penalty exposure

Accelerate & easily scale vendor onboarding & assessment

Accelerate innovation and patient care by getting clinical vendors live in hours instead of weeks

Automatically risk-tier BAs, subcontractors, and PHI-handling entities, eliminating costly contract gaps

Get autonomous reviews and remediation, so teams focus on risks that impact patient care

Continuous monitoring of third-party security risk postures

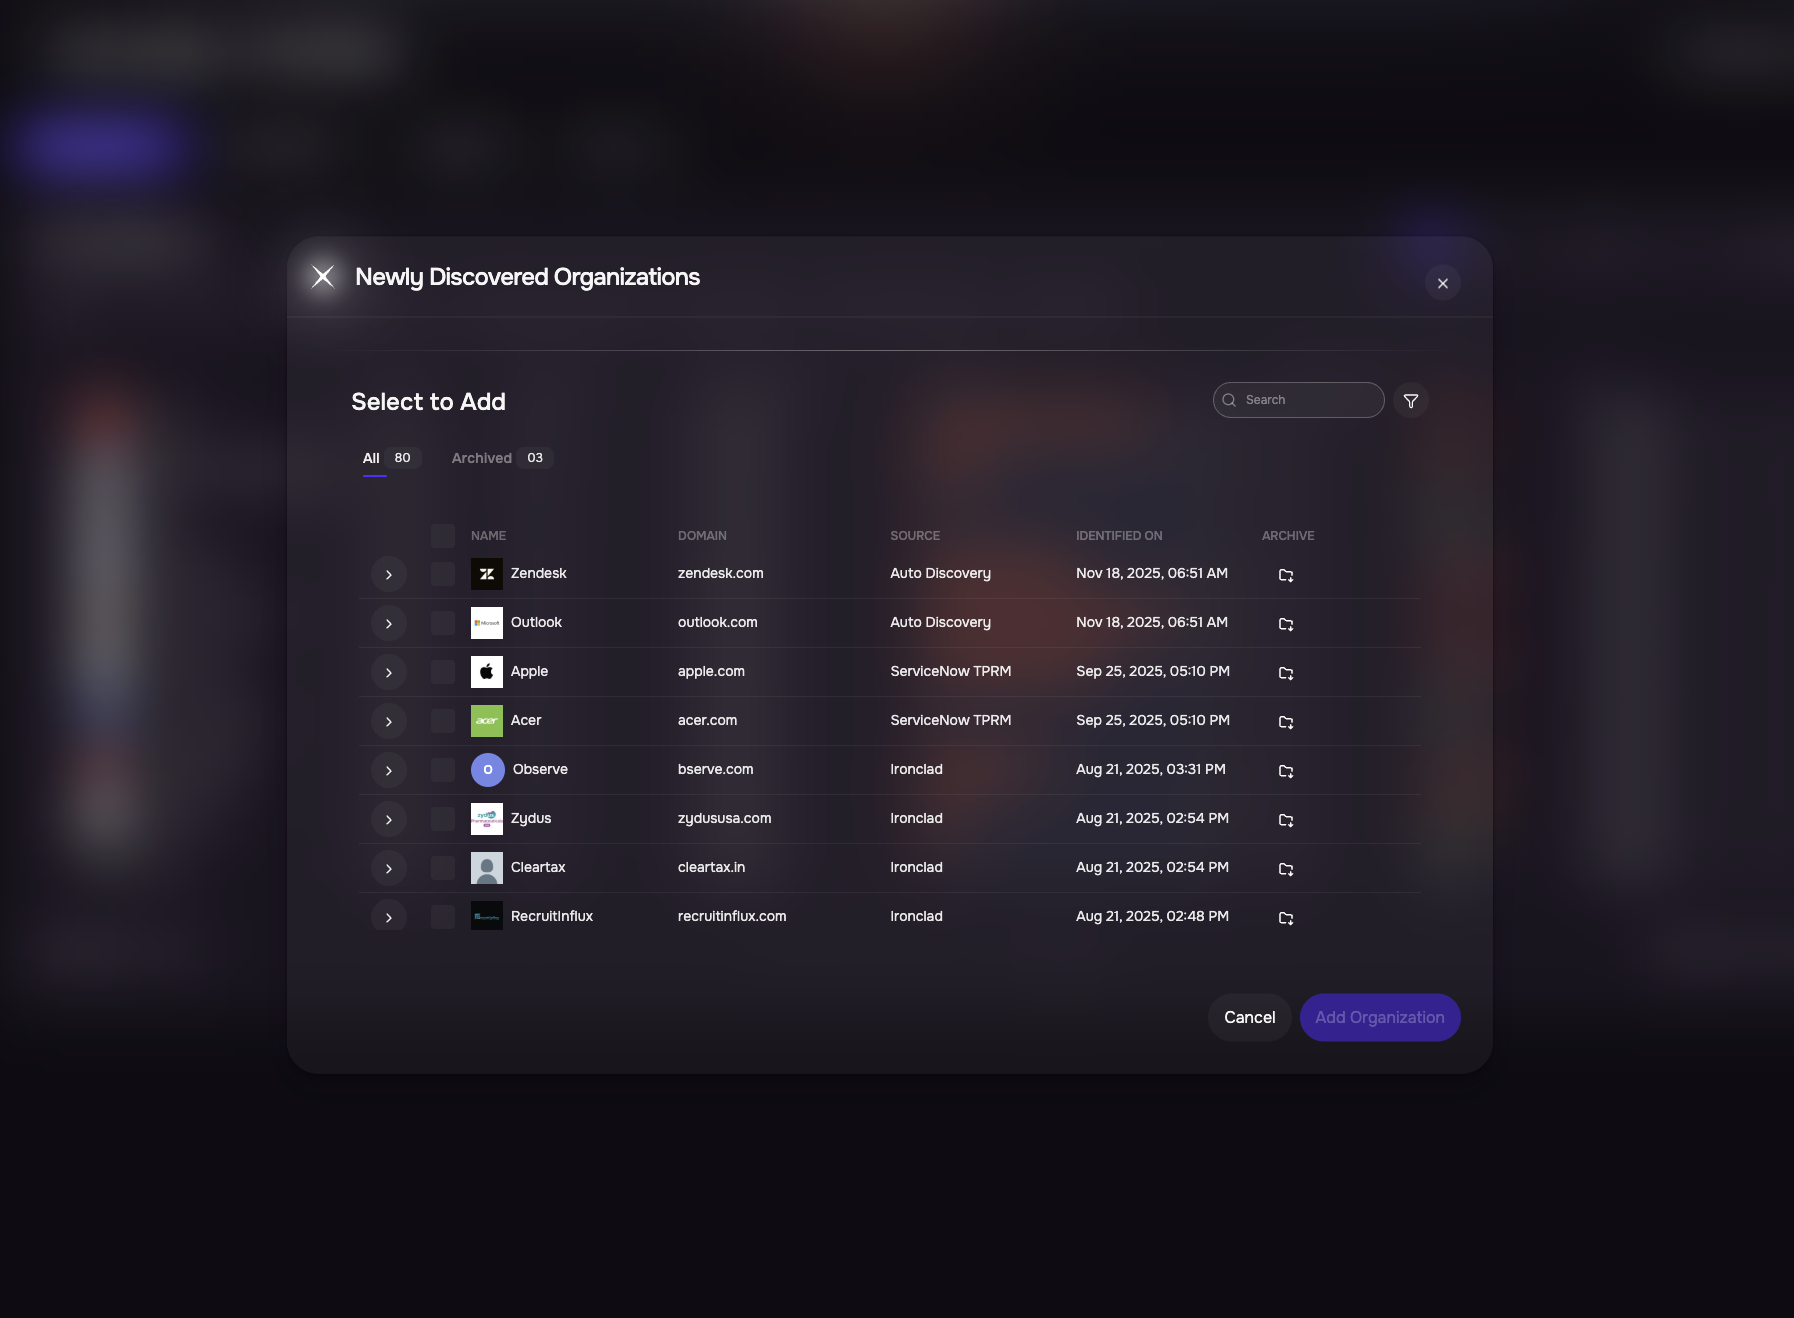
Accelerate detection of third-party breaches to minimize patient-critical service disruptions

Get full visibility into third- & fourth-party ecosystems - suppliers, cloud apps, subcontractors

Reduce downtime from third-party outages due to concentration risks and single vendor dependencies

Strategically prioritize your cybersecurity investments

Run what-if analyses to see how changes to controls and third-party risk reduce patient-care disruption

Demonstrate the ROI of security investments that drive the greatest risk reduction

Strengthen insurance negotiations and premium positions with defensible evidence of risk reduction

The Proof

Machine-Speed Defense.
Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart’s TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount

Trusted By 10% of Fortune 500

  • T-Mobile
  • Fannie Mae
  • Verizon
  • Delta
  • Honeywell
  • S&P Global
  • HP
  • AAA
  • ADP
  • Chipotle
  • Snap Inc.
Book a demo

Ready to Meet your
AI Co-Workers?

Get a Demo