Resource Library
 CTEM
From Exposure Backlogs to Verified Remediation
Series: Understanding CTEM and Why It Matters | Part 3 of 3: Validation and Mobilization By: Ramesh Ramachandran Until now we explored why 25 years of vulnerability management hasn’t…
 CTEM
How CTEM Turns Vulnerability Data Into Risk Reduction
Series: Understanding CTEM and Why It Matters | Part 2 of 3: Scoping, Discovery, and Prioritization By: Ramesh Ramachandran In the first blog of this series, we talked about…
 CTEM
The Defender’s Window Is Open. Here Is What Enterprise Security Has to Change.
Part 1 of a four-part series on what the defender’s window requires at enterprise scale. This week, OpenAI and more than 100 organizations, including Google, Microsoft, CrowdStrike, and…
 Threat Research
New Exploitation Signals Put Oracle, GitLab, and Zimbra in Focus
By SAFE Threat Research Team This week’s exploitation activity spans enterprise middleware, development platforms, collaboration software, remote-access infrastructure, and AI tooling. Oracle HTTP Server and WebLogic Proxy CVE-2026-21962…
 Trends
The Suspect Is New. The Doors Are Not.
Explaining the Hugging Face break-in the way I would explain it to a jury By Josh Fazio, VP of Global Pre-Sales, Safe Security The hardest part of working…
 CTEM
AI Took 17,600 Autonomous Actions to Break In. How Many Is Your Defense Taking Today?
By: Saket Modi, Co-Founder and CEO of SAFE “AI models are becoming extraordinary zero-day discovery engines.” – JFrog’s CTO Last month, Hugging Face disclosed a security incident…
 Threat Research
Lazarus Windows Zero-Day, vCenter RCE, and Cisco VPN Exploitation Lead This Week’s CVE Priorities
By SAFE Threat Research Team This week’s exploitation activity spans zero-day privilege escalation, persistent access, service disruption, and enterprise application compromise. Lazarus exploited Windows CVE-2026-68820 to elevate privileges…
 Events
Life After Mythos: 3 Hard Truths BlackHat Missed
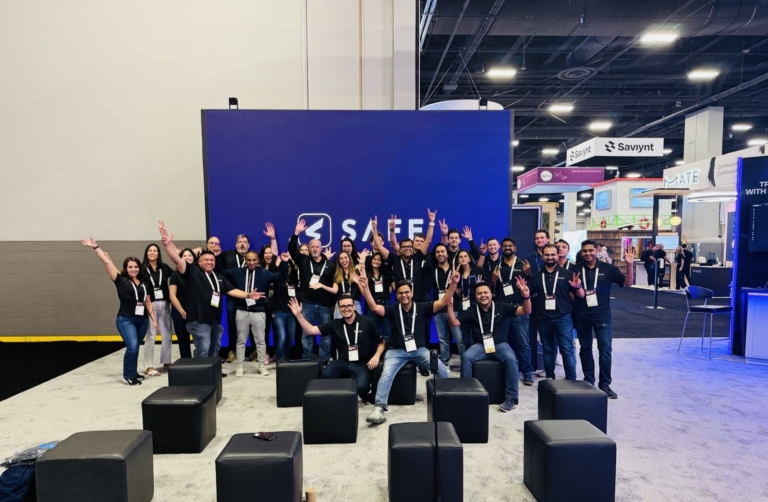
By Dr Meghan E Maneval, Director of Community and Education Walking the floor at BlackHat USA 2026, one thing was undeniable: the security industry has officially crossed into…
 Whitepapers
Beyond the Backlog
AI has collapsed the time between vulnerability discovery, proof, and exploitation. See the exposure management operating model built for what comes next.
 Datasheets
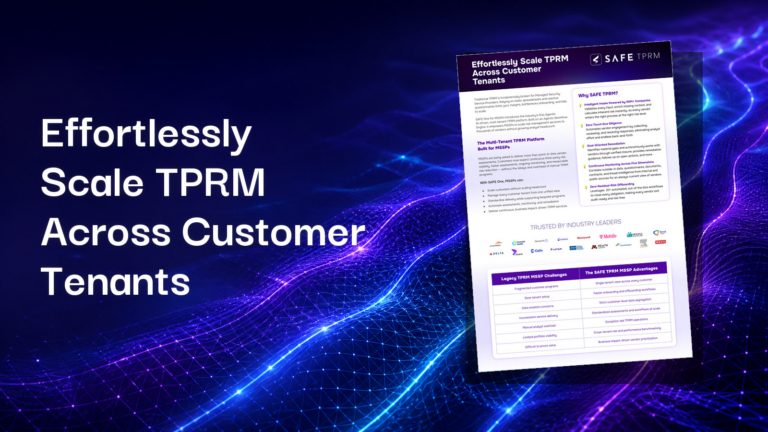
Effortlessly Scale TPRM Across Customer Tenants
SAFE TPRM is the industry’s first Agentic AI-driven, multi-tenant Third-Party Risk Management platform, purpose-built for MSSPs. Orchestrating 100+ specialized AI Agents, it automates vendor intake, due diligence, remediation,…
 Threat Research
N-able RMM Compromise, SonicWall Ransomware Intrusions, and OWAReaper Persistence Lead This Week’s CVE Priorities
By SAFE Threat Research Team This week’s exploitation activity is concentrated on technologies that already hold administrative trust across enterprise environments. Attackers exploited N-able N-central to obtain remote…