Vendor Risk Assessment Automation for Analysts | SAFE
For TPRM and vendor risk analysts

Stop reading SOC 2s.
Start reading risk.

SAFE reads the SOC 2, drafts the questionnaire from the vendor's own evidence, flags where answers and evidence disagree, and sends the follow-ups. You review what matters and make the call.

The Problem

You were hired to judge vendor risk.
Most of the week goes on paperwork.

  1. Evidence review eats the calendar

    Reviewing a single SOC 2 report by hand took Instacart's team one to three days. Multiply that by every vendor in the queue.

  2. Chasing vendors is the real job

    Outreach, reminders, clarifications and missing documents run through email, so assessments stall waiting on replies.

  3. Self-reported answers go unchecked

    When the questionnaire says one thing and the evidence says another, the conflict surfaces late, or not at all.

  4. Outside-in alerts arrive without context

    Analysts can't always tell whether a flagged IP or domain even belongs to the vendor, so real issues hide among false ones.

  5. Supplier breaches start a manual scramble

    News of a vendor incident arrives first. Working out which relationships, data and services are affected is left to the analyst.

  6. Every reassessment starts from zero

    Prior work isn't reused, and remediation lives in spreadsheets and inboxes until nobody knows what was fixed.

The Solution

Solution highlights

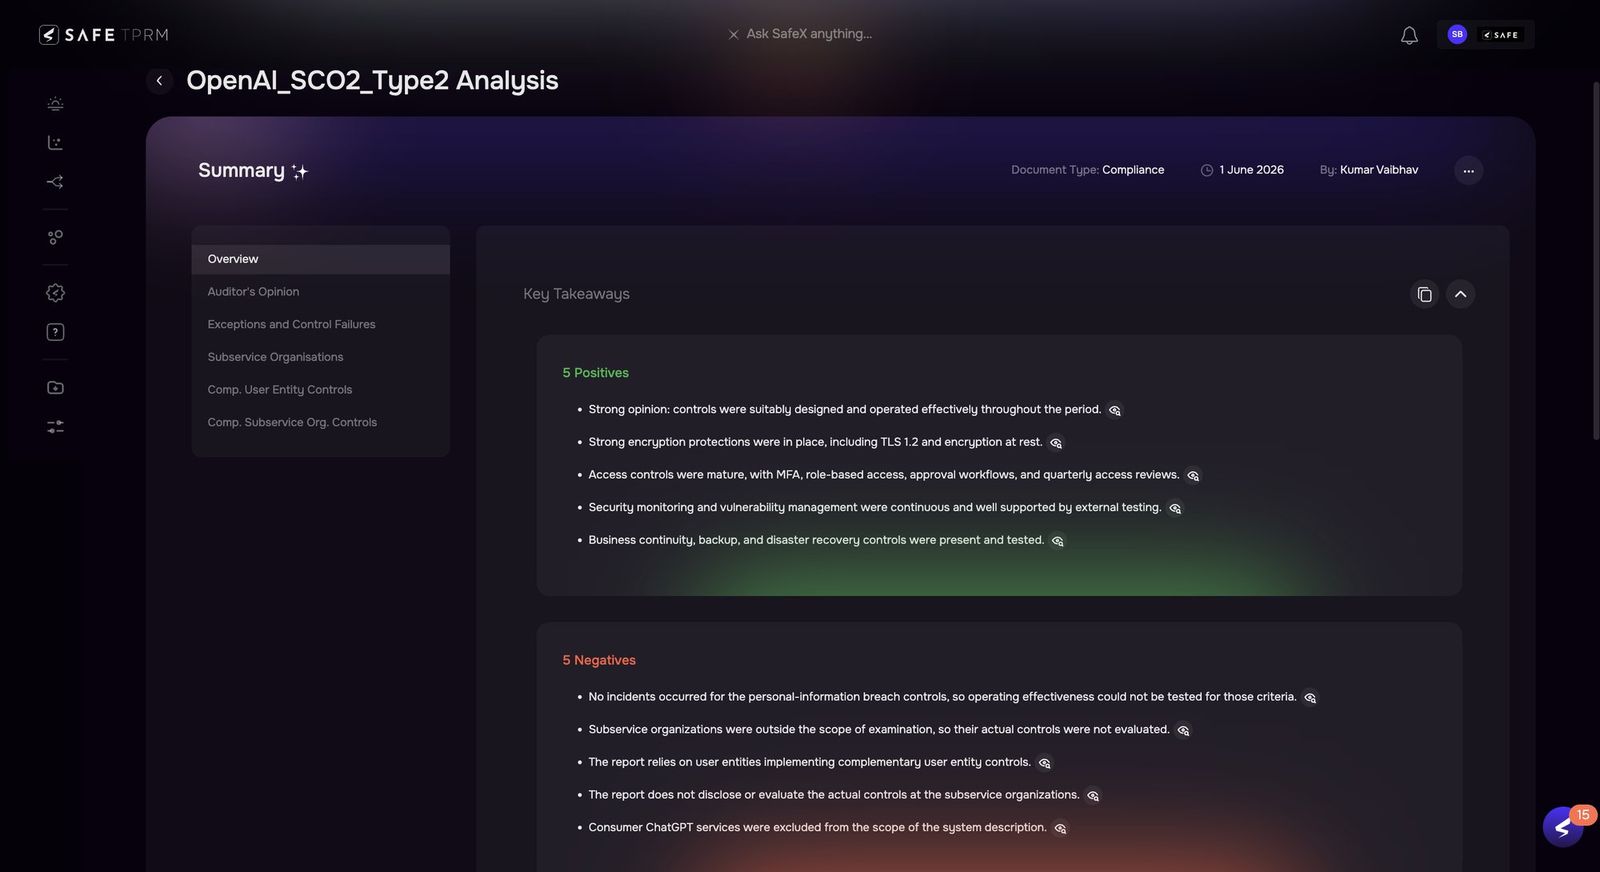
AI summary of a vendor SOC 2 Type 2 report with key positives and negatives

Get through vendor evidence in minutes, not days

More vendors are cleared each week, and your time goes on judgment instead of reading.

  • SAFE reads each SOC 2, ISO certificate and policy, checks it is current and genuine, and summarizes the exceptions.
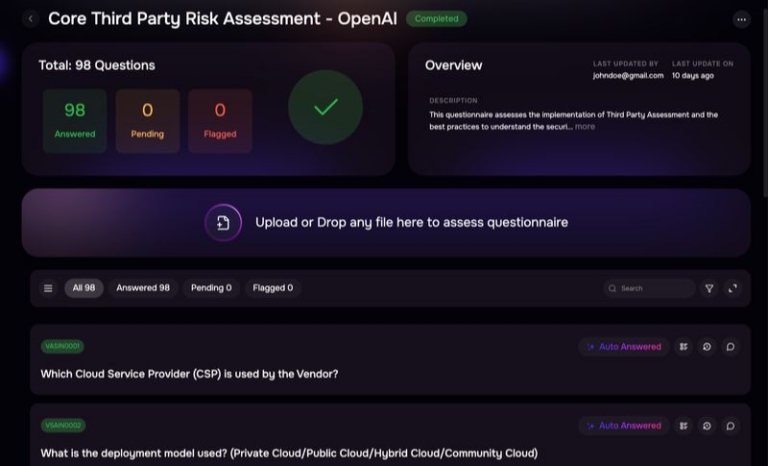
  • Questionnaire answers are drafted from the vendor's own evidence, so you review instead of re-keying.
  • Contracts are checked for security, privacy and AI risk, so you don't need a separate legal pass to spot the gaps.
  • What it's worth: at Instacart, one SOC 2 review went from one to three days to minutes.
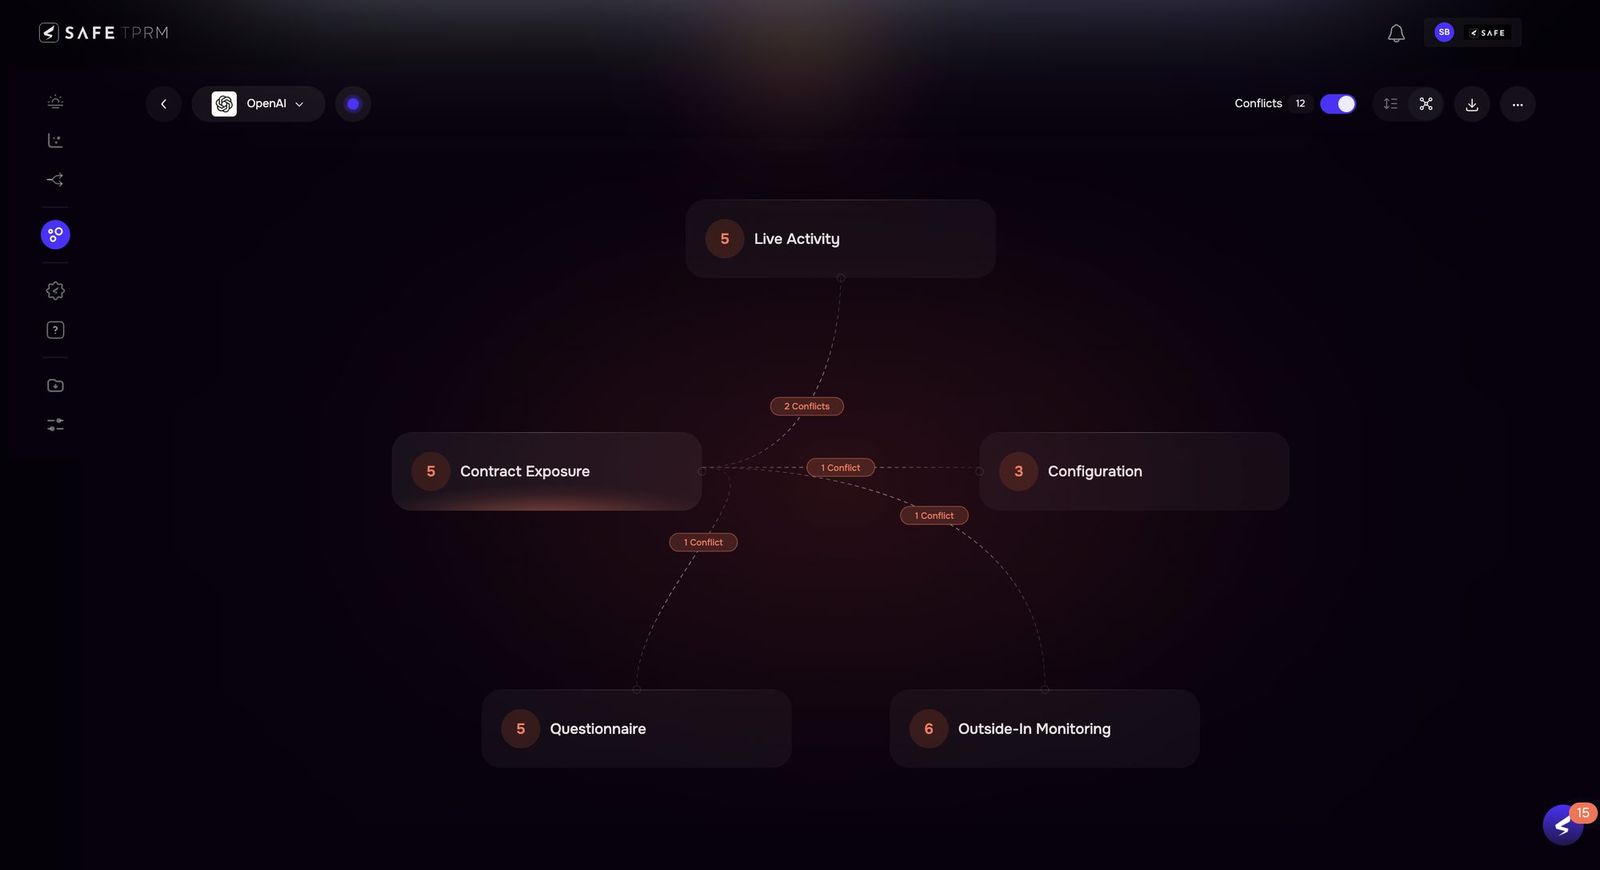
Conflicts flagged between questionnaire, contract, configuration and monitoring evidence

Sign off with confidence

Fewer missed risks, and decisions you can explain when a business owner pushes back.

  • Conflicts between what a vendor says and what the evidence shows are flagged while the vendor is still answering.
  • Questionnaires, documents, outside-in findings, contracts and public records sit in one view, so nothing is judged in isolation.
  • AI review is advisory, so the final call, and the credit for it, stays with you.
  • What it's worth: conclusions that trace to evidence, which is what auditors and business owners ask for.
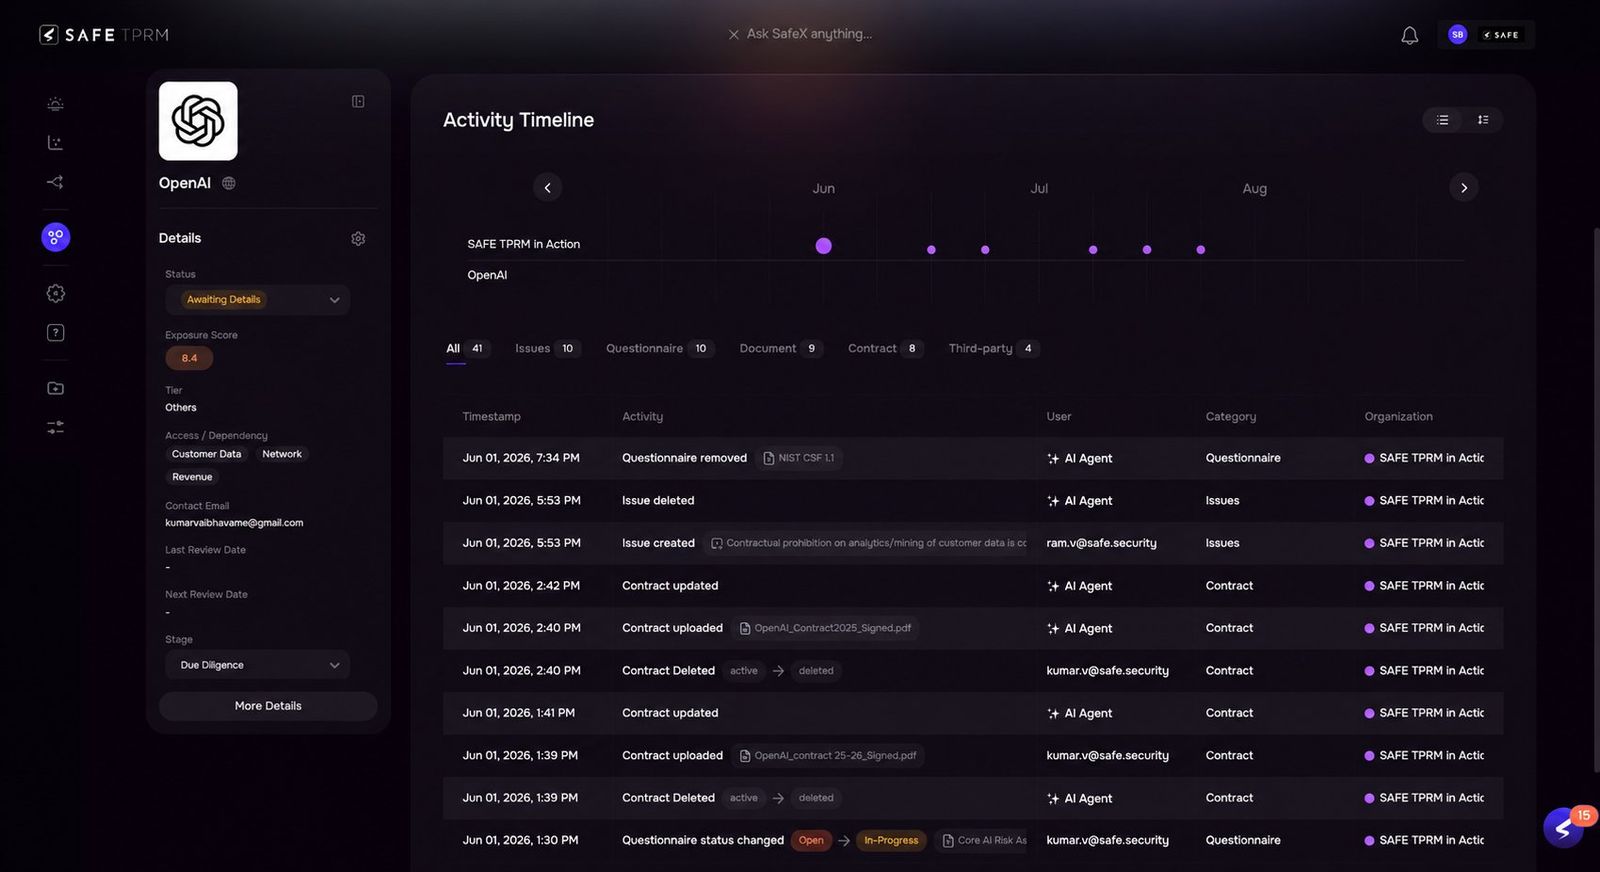
Vendor activity timeline showing actions completed by the AI agent

Stop chasing vendors

The follow-ups run themselves, so your inbox stops being the workflow.

  • Agentic workflows send requests, reminders and clarifications, and pause for your approval at the steps that matter.
  • Vendors respond through a simple portal with no account to set up, so replies come back faster.
  • Reassessments reuse what you collected last time, so you only review what changed.
  • What it's worth: Instacart eliminated 30+ hours of analyst work per assessment.
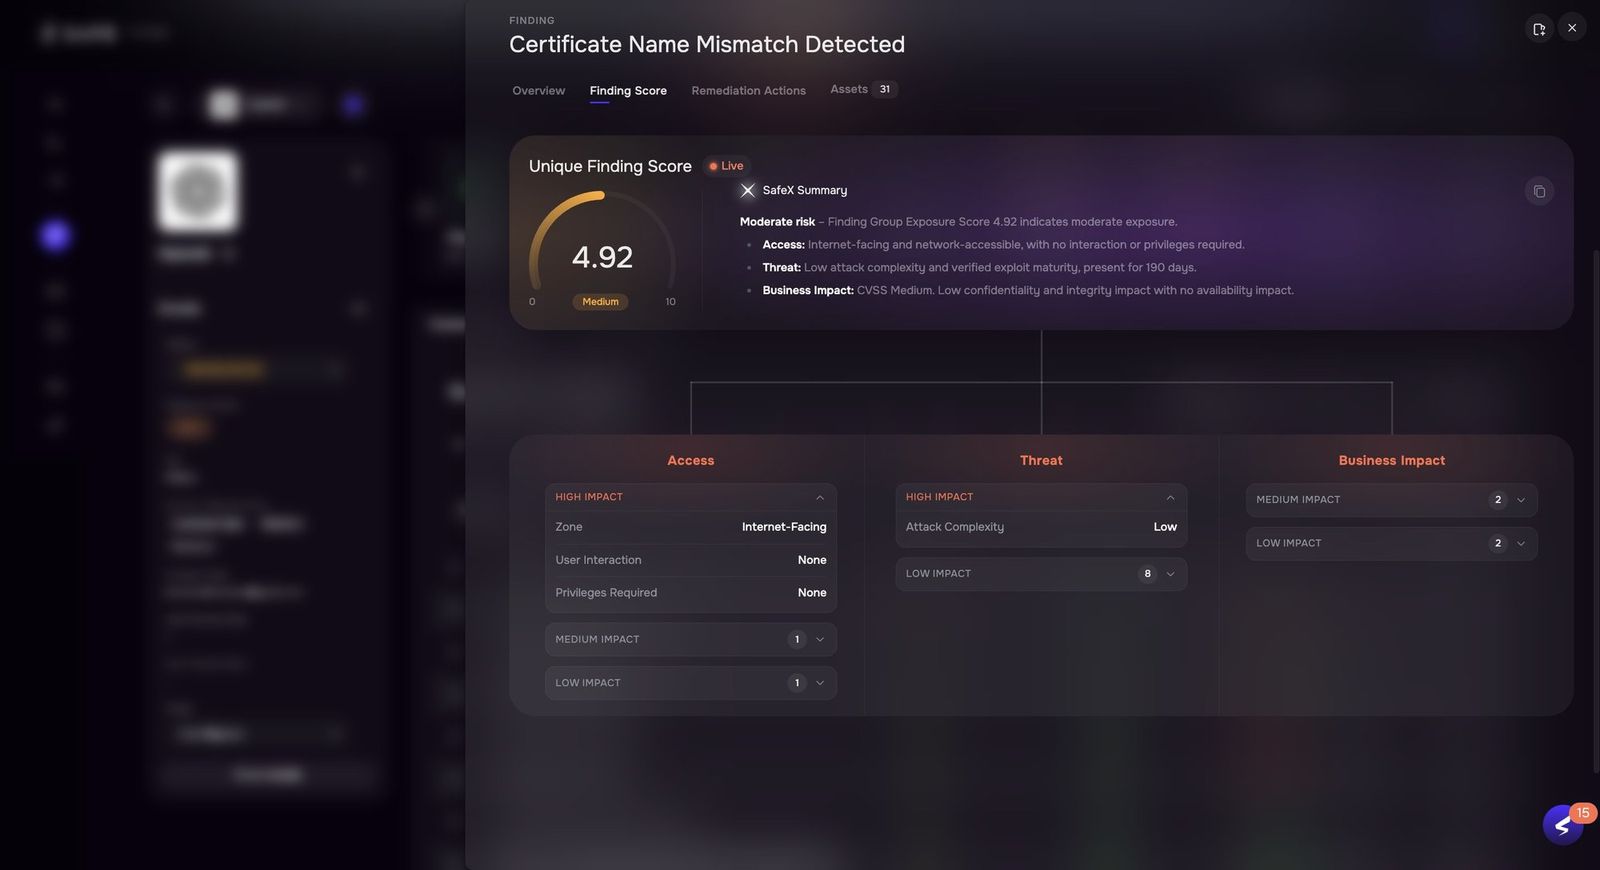
Finding score with SafeX summary of access, threat and business impact

Spend alert time on real risk

Fewer pings, each with the context to act.

  • Alerts follow rules you set, like a score drop on a Tier 1 vendor, and arrive as digests.
  • Every flagged domain or IP shows why it was tied to the vendor, so you stop investigating assets that were never theirs.
  • Breaches, leaked credentials and news for each vendor sit in one place, so an incident check takes one look.
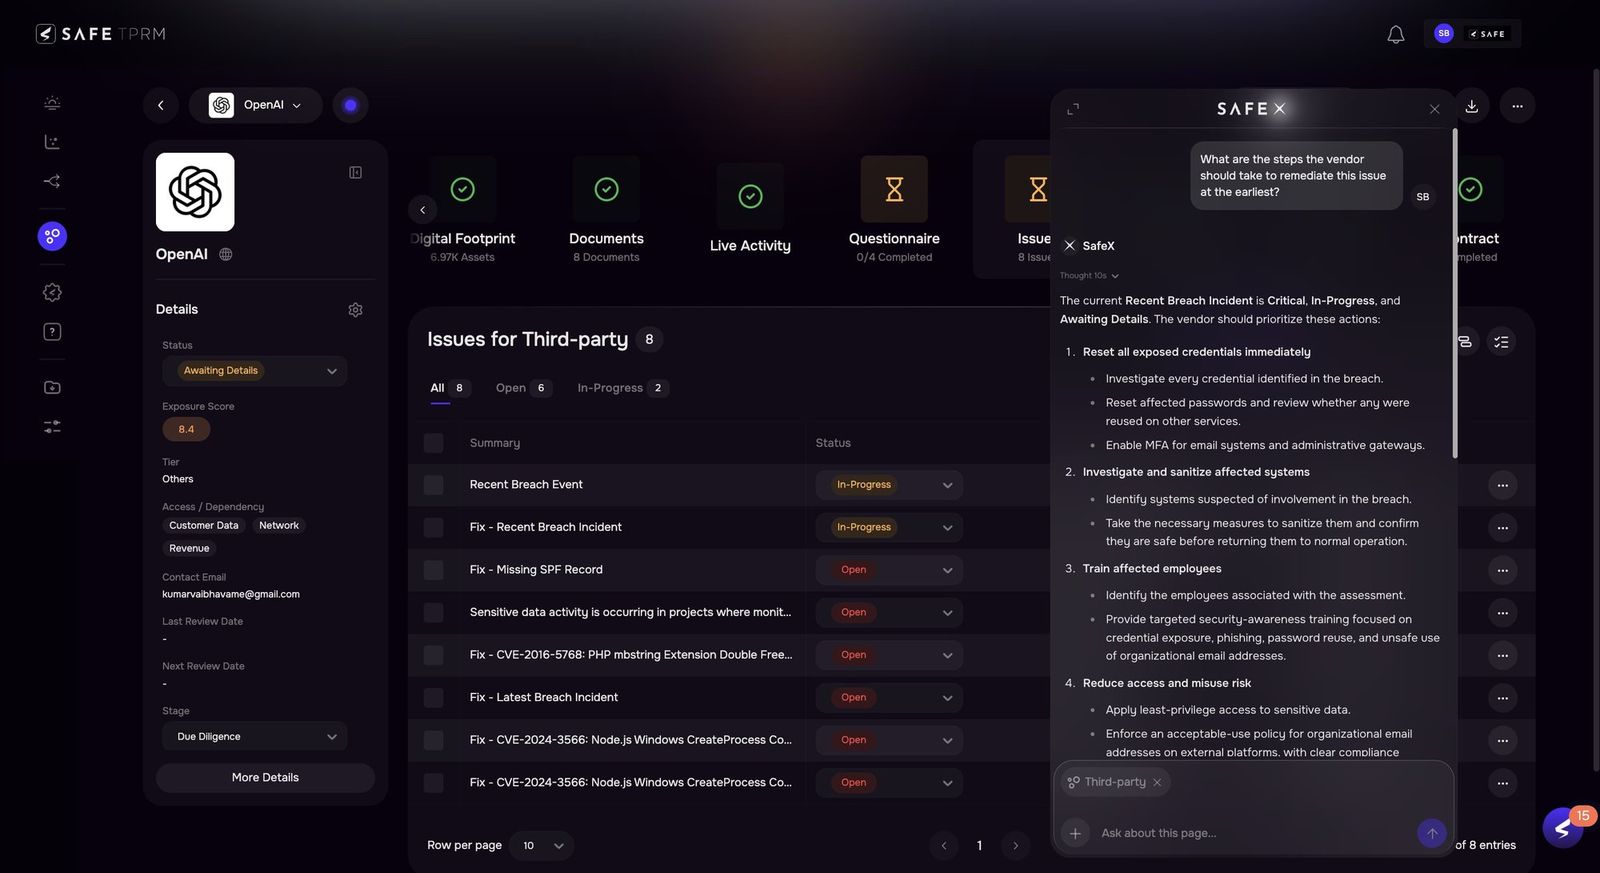
Vendor issues list with SafeX recommending remediation steps

Close findings, not just log them

Every issue has an owner, a date and an end, and the trail is there when audit asks.

  • Findings become tracked action plans.
  • Related findings group into one request to the vendor.
  • Ask SafeX about any vendor, finding or contract in plain language, instead of building a report.
AI You Control

The AI drafts. You decide.

Advisory by design

AI review suggests; only an analyst changes severity or status.

No silent issues

AI-recommended issues stay suggestions until you accept them.

Off when you need it off

Admins can disable SafeX, AI summaries and AI-powered uploads in one setting.

Your permissions, everywhere

Agents act with the same role-based access as the person using them.

The Proof

Machine-Speed Defense. Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart's TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount
Book a demo

Spend Friday on risk, not reminders.

Get a Demo