Manual Vendor Assessments Drain Analyst Time | SAFE
Scale TPRM Without Adding Headcount

Your analysts read reports all day.
Risk decisions wait.

Every assessment means reviewing questionnaires and documents by hand, chasing vendors for evidence and redoing last year's work at renewal. SAFE TPRM AI Co-Worker takes on the routine review and follow-up, so your team covers more vendors with the people it has.

The Problem

What manual assessment looks like today

  1. Every document is read by hand

    Analysts review questionnaires, SOC 2 reports, policies and supporting evidence line by line for every vendor.

  2. Conflicts are found one at a time

    Analysts compare answers against evidence themselves to spot contradictions, gaps and the findings that matter.

  3. Chasing vendors fills the week

    Outreach, evidence requests, clarifications and reminders are sent and tracked manually, vendor by vendor.

  4. Reassessments start from zero

    Renewal reviews repeat work already done, with little reuse of prior responses, evidence and analysis.

Manual vendor review compared with analyst-approved automation in SAFE TPRM

From manual review to analyst-approved automation

When assessments run by hand

  • Skilled analysts spend most of their time on repetitive review and coordination.
  • Assessments and reassessments pile up and miss their deadlines.
  • More vendors means more analysts, contractors or outsourced reviews.
  • Experienced people have less time for judgment, governance and material risk decisions.

When AI agents handle the routine

  • The same team manages more third parties and more assessments.
  • Growing assessment volume is absorbed without building a new backlog.
  • Each added assessment takes less human effort than the one before.
  • Analysts concentrate on exceptions, governance and the decisions that matter.
How SAFE Helps

AI agents do the evidence work. Analysts make the calls.

Eight capabilities in SAFE TPRM take repetitive review and coordination off your team, while every material decision stays with a person.

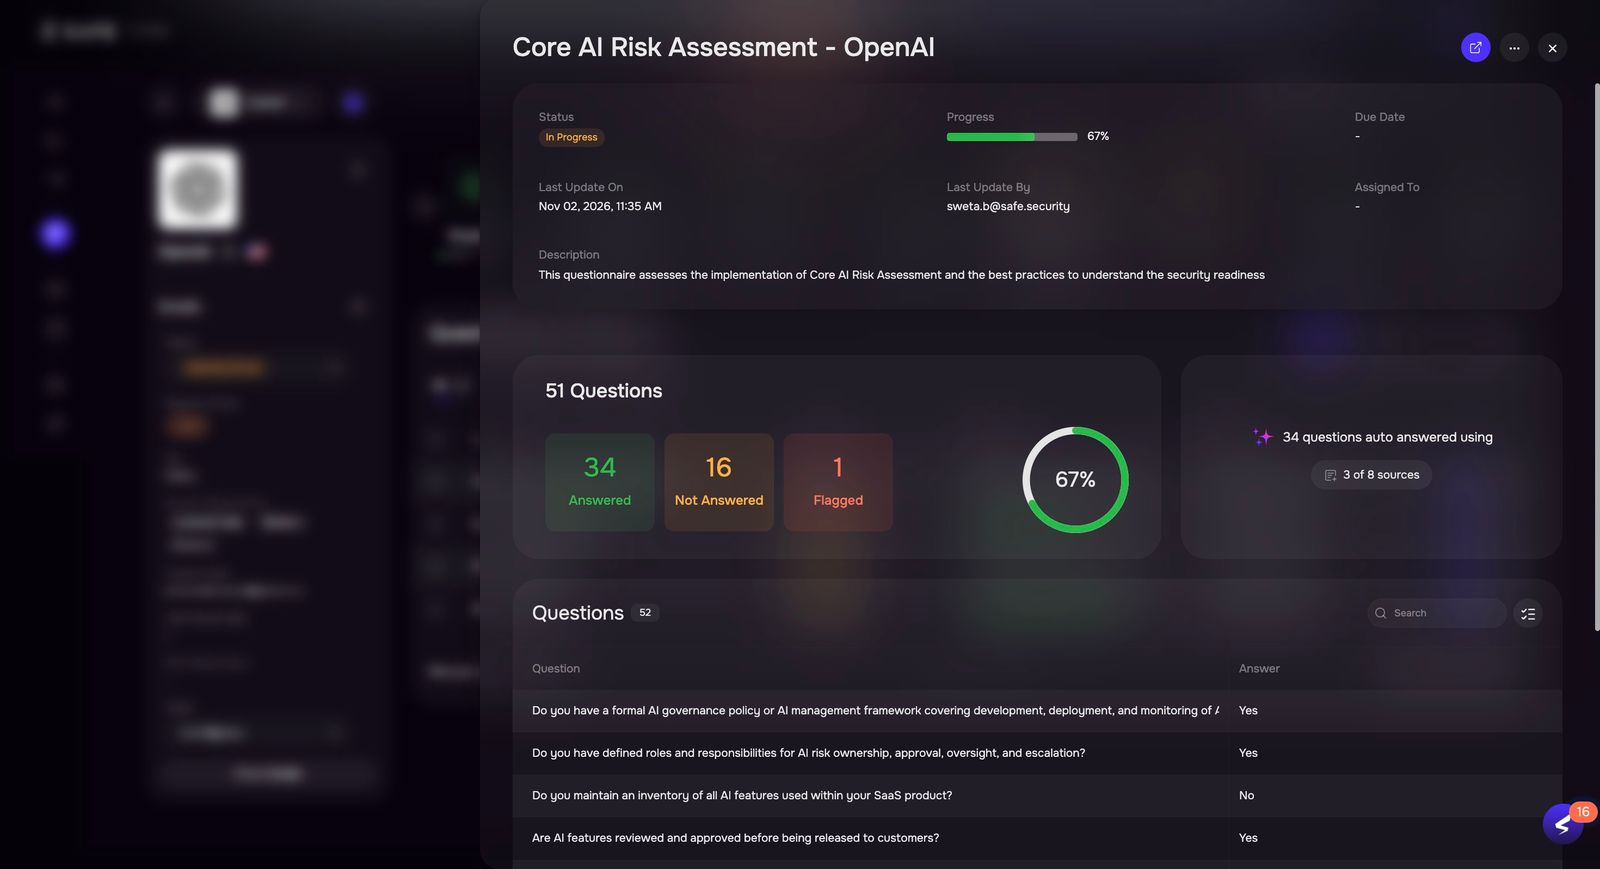
AI review results with Passed Review, Needs Attention and Not Reviewed counts and one flagged answer open.

Review every questionnaire and document with AI

AI reviews every questionnaire and document, so analysts start from drafted answers with sources.

  • Ingests SOC 2 reports, ISO certificates, policies, pen tests and questionnaire responses and maps them to controls.
  • Drafts questionnaire answers with a source citation and confidence indicator on each one.
  • Flags inconsistencies, weak evidence and answers that need an analyst as vendors submit.
  • Turns gaps into control-level findings and issues.
  • Leaves severity, findings and every material risk decision with your analysts.
No-code workflow builder showing event, schedule and manual trigger options

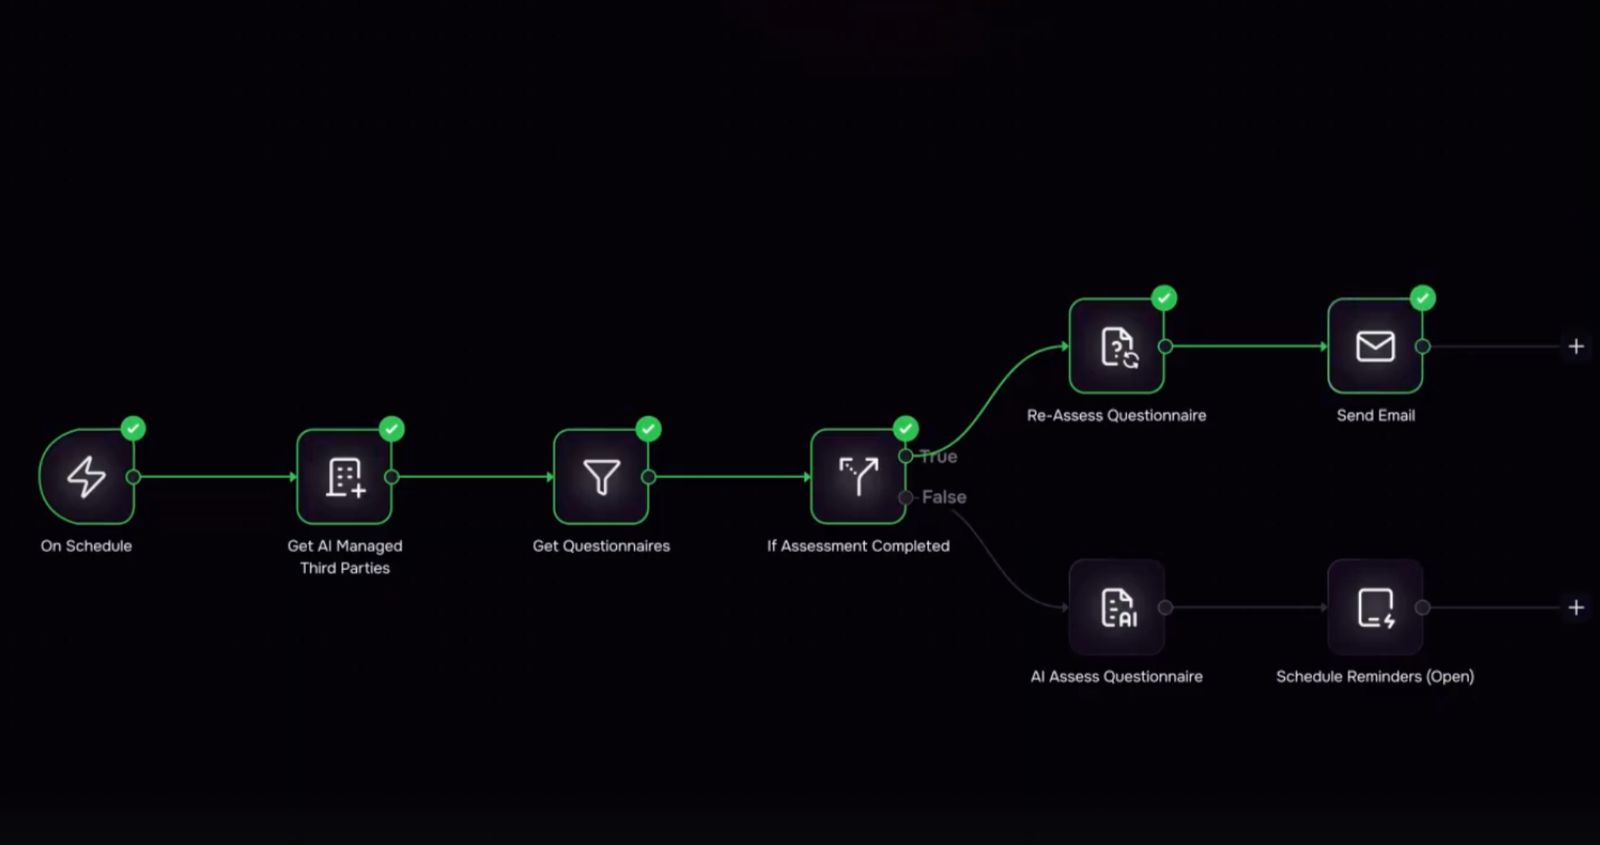
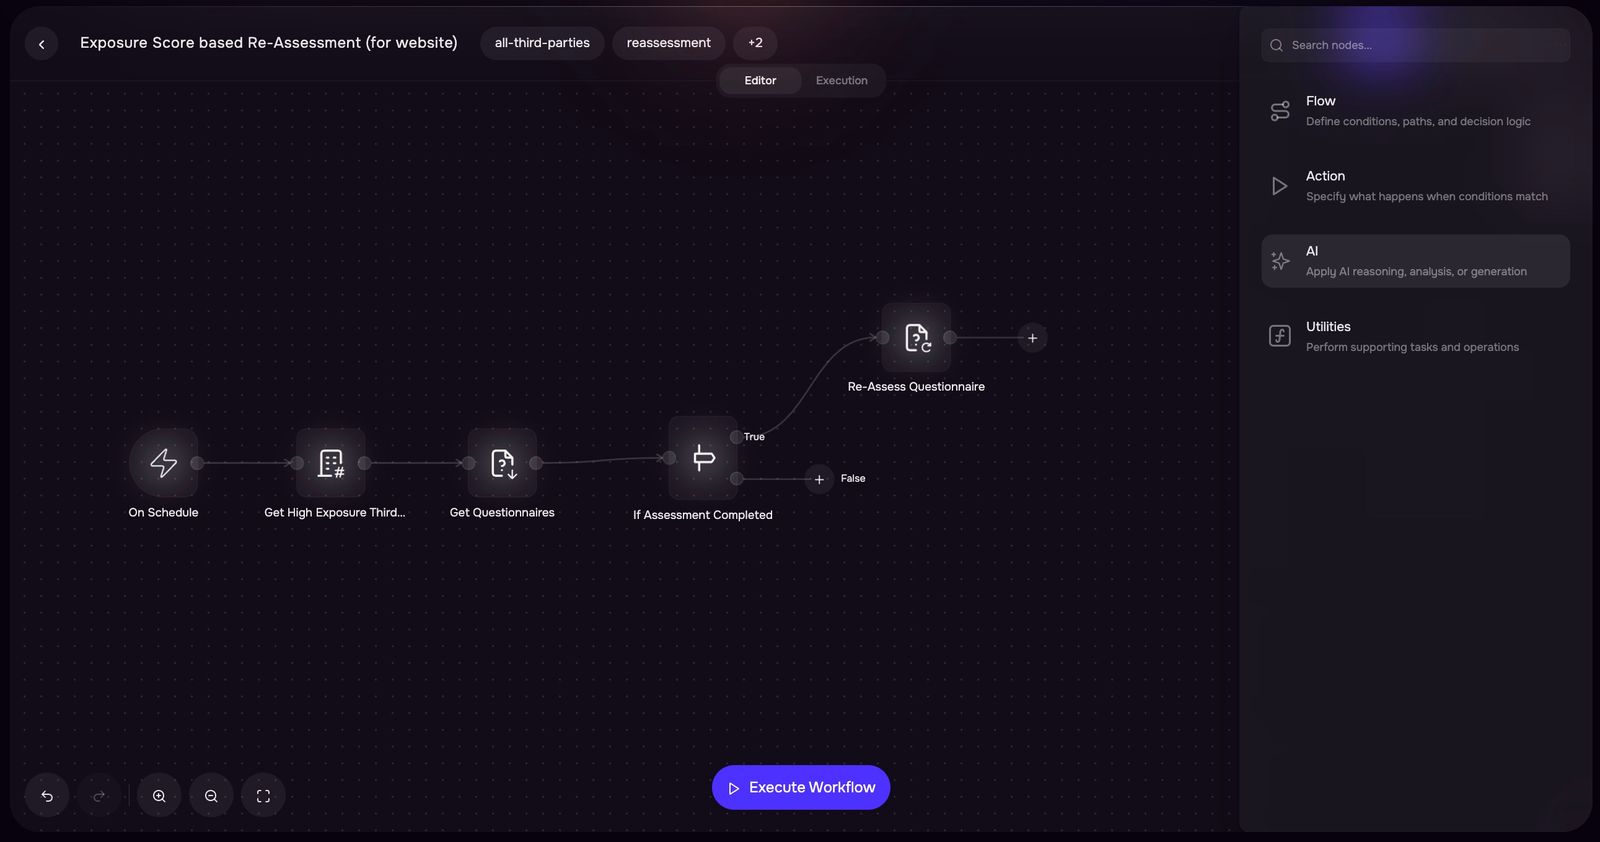
Let agentic workflows run the routine steps

A no-code workflow builder runs the routine steps of each assessment on its own.

  • Start from pre-built templates for onboarding, reassessment and issue management.
  • Add human approvals wherever your process needs them.
  • Send assessments, create issues, send reminders and update third-party records automatically.
  • See every run, with reporting on the work completed and the analyst hours saved.
Explore agentic workflows
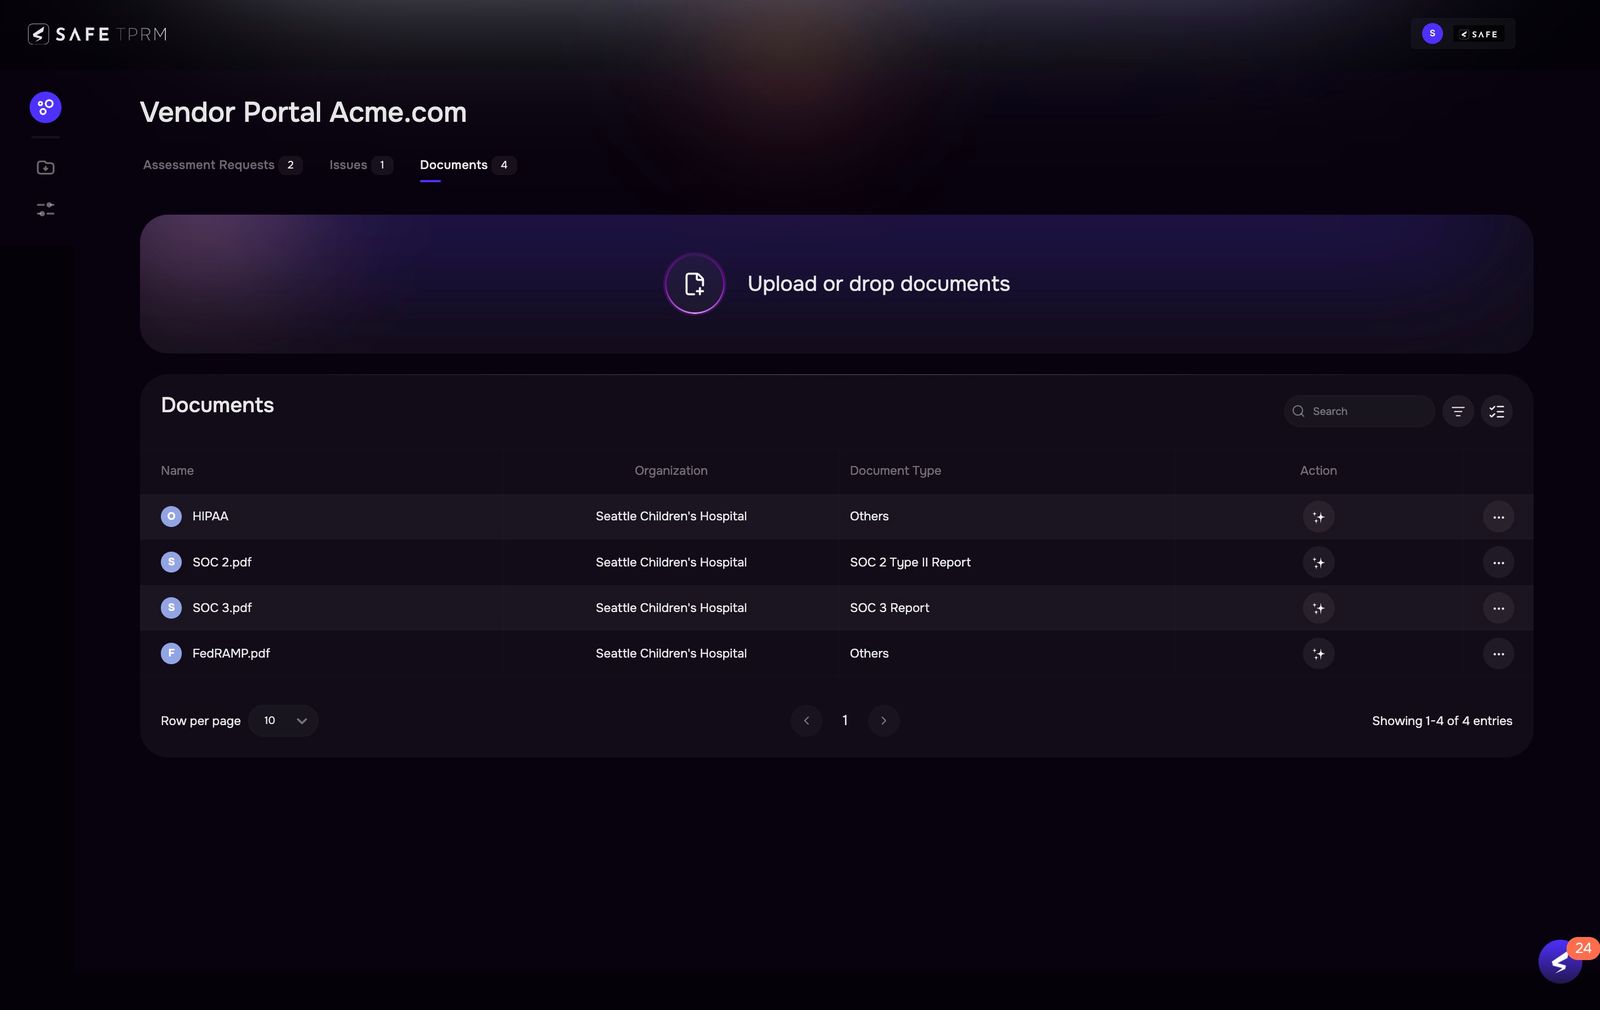
Vendor portal documents tab with multi-file upload

Give vendors one place to respond

Vendors respond to assessments, evidence requests and issues in one portal, with no account to create.

  • Passcode-protected links open each request securely.
  • Several vendor contacts can collaborate, delegate questions and save progress.
  • Agents chase missing responses and escalate only the vendors that stay unresponsive.
  • At reassessment, valid responses carry forward and vendors refresh only what expired or changed.
Third-party AI summary with top risk drivers and suggested issues

See what drives each vendor's risk and what to do next

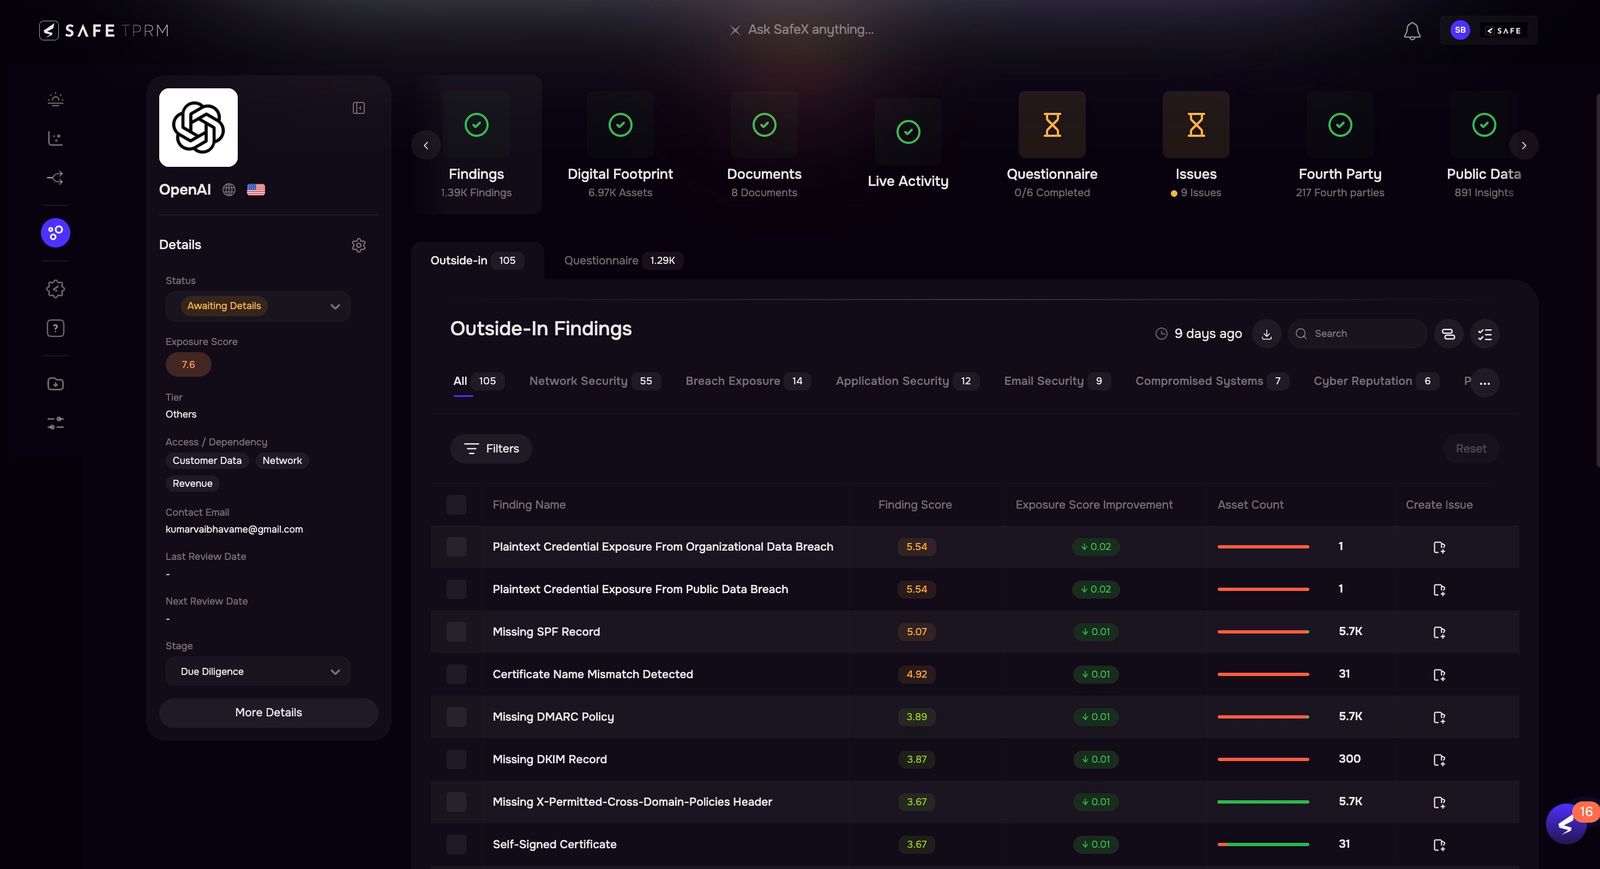
AI brings assessments, findings, control gaps, external exposure and documents into one view of each third party.

  • Surfaces the factors that contribute most to each vendor's risk.
  • Recommends remediation actions, priority controls and next steps.
  • Shows the evidence and reasoning behind every recommendation.
  • Keeps each recommendation a suggestion until an analyst accepts it.
Explore AI risk decisioning
Issue list with owners, due dates and automated reminders

Turn findings into tracked remediation automatically

Findings from questionnaires, external exposure and AI review become tracked issues through to closure.

  • Create issues individually, in bulk or automatically.
  • Review every finding in one place.
  • Assign each issue an owner in your organization or at the vendor, with automated reminders.
  • Consolidate related findings into a single remediation action.
  • Close each issue as resolved, accepted or escalated, with rationale and evidence on record.
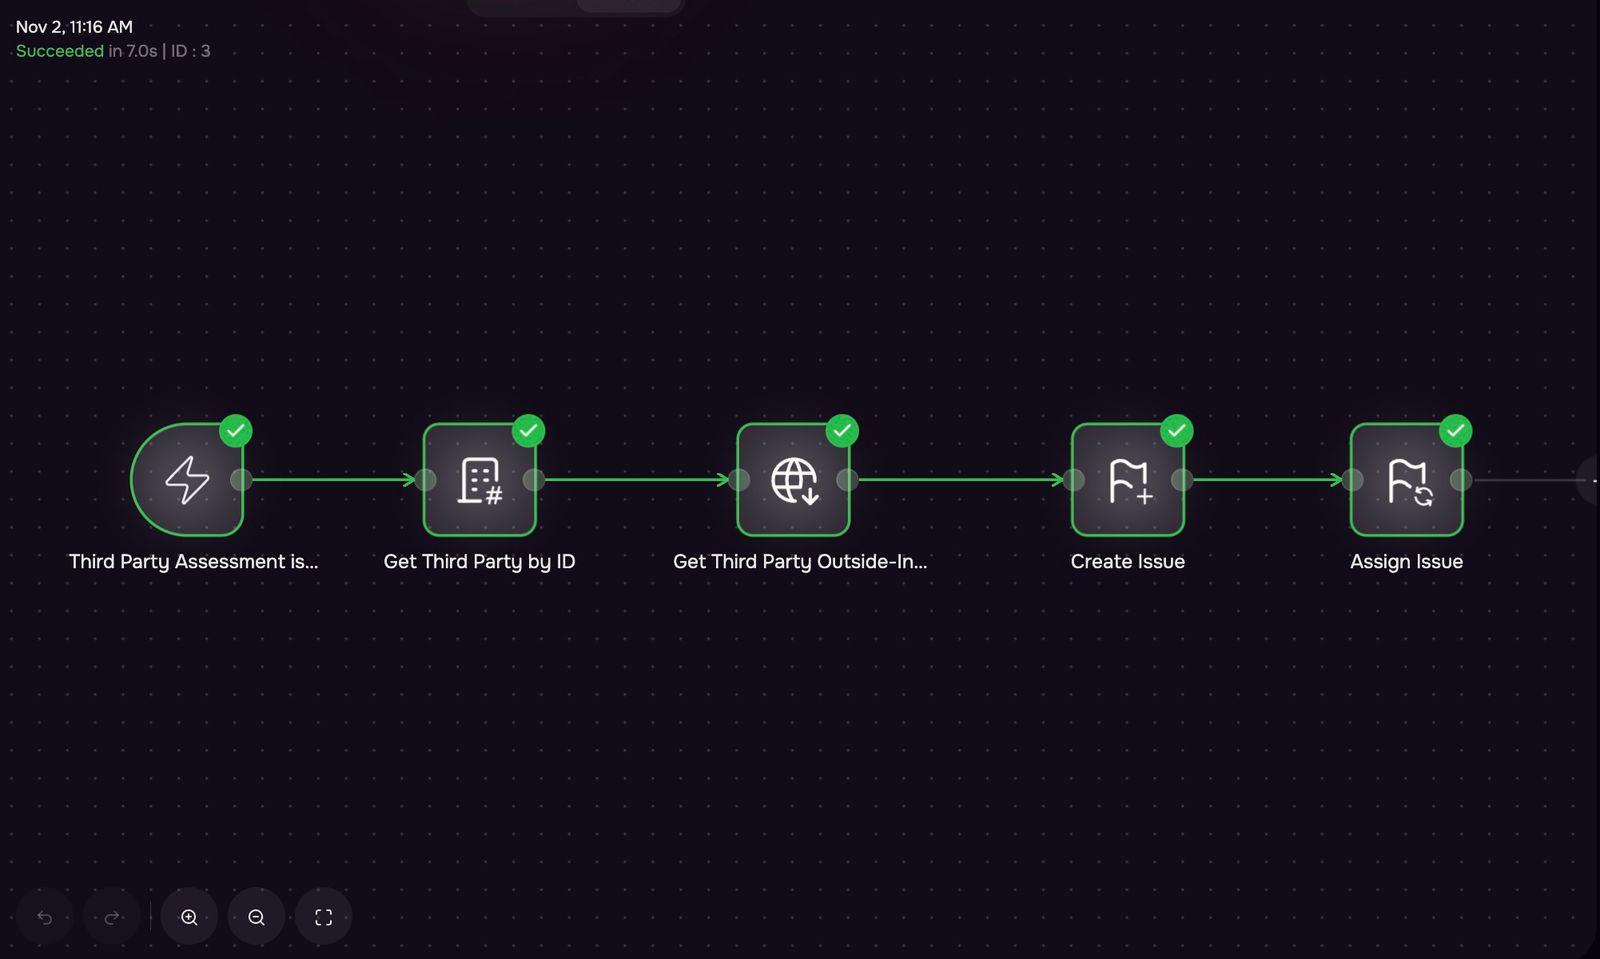
Workflow run with AI questionnaire assessment, AI summary and issue creation steps

Route material changes without manual triage

SAFE TPRM routes material vendor changes to the person who owns them and starts the right response.

  • Set rules on vendor tier, risk score, breach events, findings and assessment results.
  • Start a workflow, an issue or a reassessment from each event.
  • Get real-time alerts by email, in the platform or as a scheduled digest.
RBAC in SAFE

Run one program across every team

One TPRM program can serve every business unit, department and geography.

  • Role-based and attribute-based access segments third parties, assessments, issues and workflows.
  • Each team works in a view of the vendors it owns.
  • Administrators keep central control of policies, fields and AI behavior.
  • Every configuration change is recorded in an audit trail.
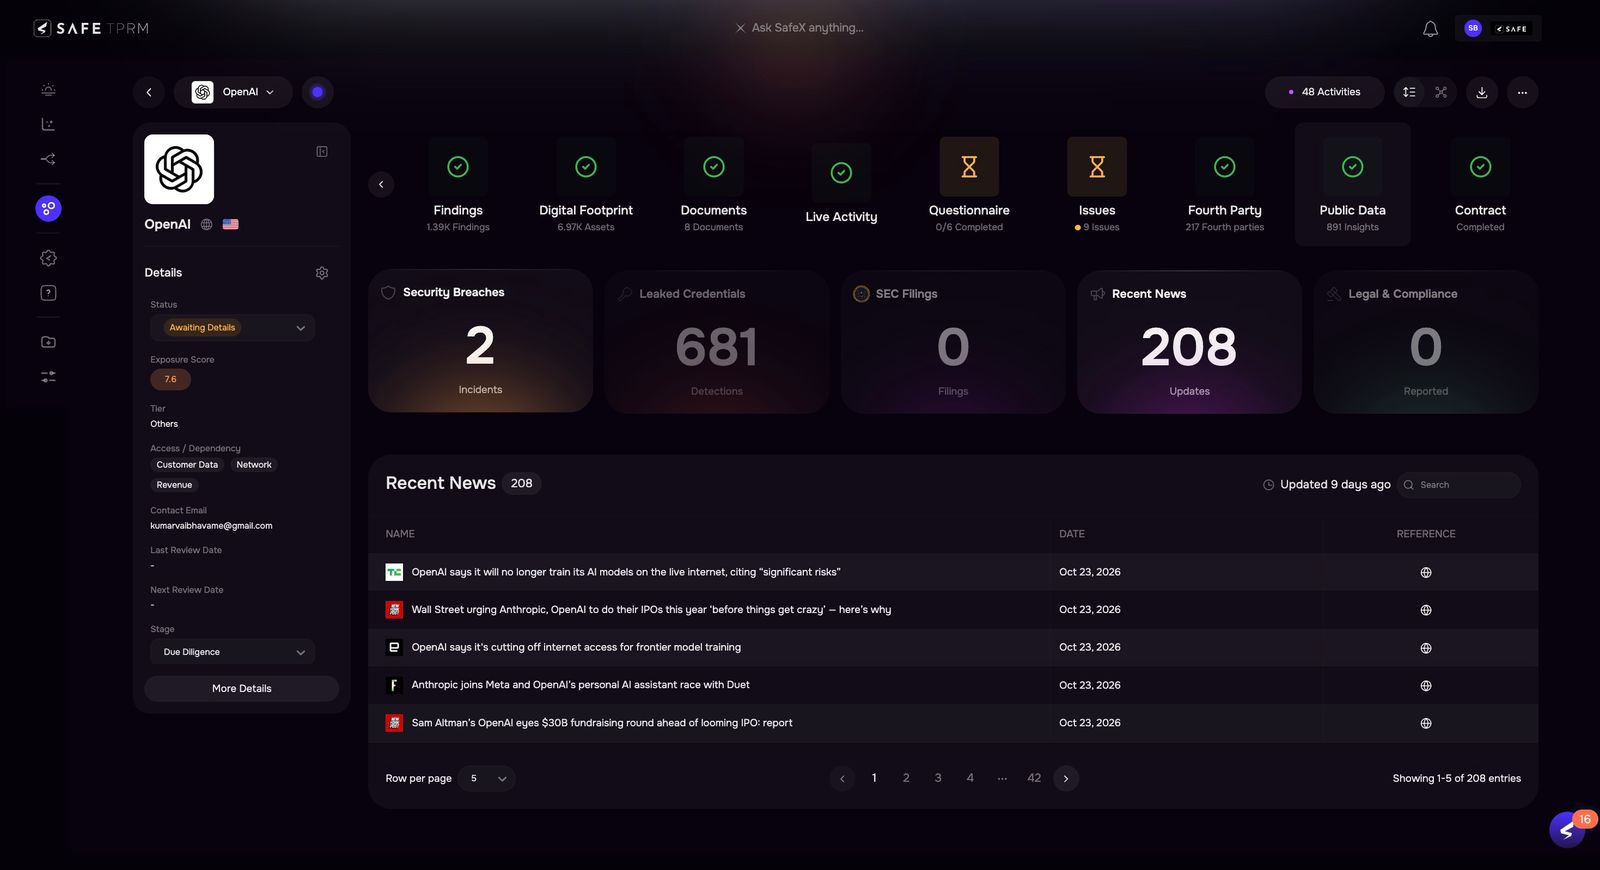
Breach event with the affected third and fourth parties listed

Answer breach questions without a manual hunt

SAFE TPRM monitors breach intelligence, leaked credentials and public sources for incidents affecting your third and fourth parties.

  • Checks each event against the vendors you actually use.
  • Alerts the right people with a scoped list of affected relationships.
  • Starts investigation, assessment and issue workflows straight from the event.
Explore breach detection and response
The Proof

Machine-Speed Defense. Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart's TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount
Book a demo

Ready to meet your AI Co-Workers?

Get a Demo