Blog
 News
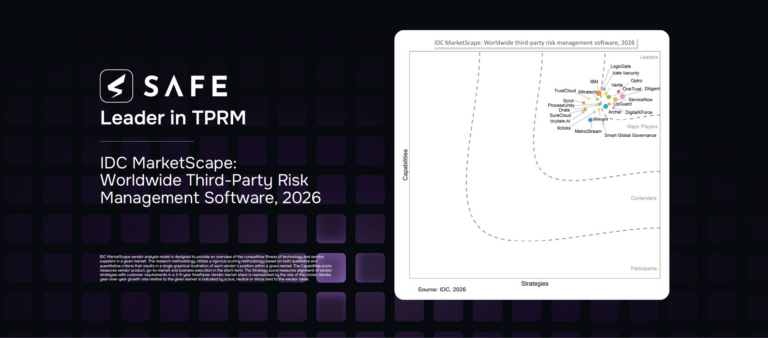
SAFE Security named a Leader in IDC MarketScape for Third Party Risk Management (TPRM) Software
Safe Security has been named a Leader in the IDC MarketScape: Worldwide Third-Party Risk Management Software 2026 Vendor Assessment. The IDC MarketScape Report evaluated vendors across 20 weighted…
 Threat Research
From Authentication Bypass to Cloud Pivot: Exploitation Is Moving Beyond the Initial Foothold
By SAFE Threat Research Team An authentication bypass in Cisco ISE can end in root access. A pre-auth flaw in Marimo can expose cloud credentials and open a…
 News
OpenAI Model Misalignment: Why Agentic AI Needs Guardrails and Measurable Trust
OpenAI recently introduced a new framework for tracking and disclosing model misalignment, together with six reports describing unexpected or concerning behavior observed during model training and evaluation. The…
 Events
SAFE at Gartner SRM London 2026: Put TPRM and CTEM Into Action
Cyber risk doesn’t wait for your team to clear its backlog. Vendor evidence needs review. Exposures need context, remediation needs owners, and someone has to verify that the…
 Threat Research
CVE-2026-42647 | JoomSport WordPress Plugin Unauthenticated Time-Based Blind SQL Injection via sortf Parameter – Full Database Extraction
CVSS Score: 9.3 CRITICAL | Affected: JoomSport <= 5.7.7 | Fixed: JoomSport 5.7.8+| CWE: CWE-89 – SQL Injection (ORDER BY)| CISA KEV: Not Listed 1. Introduction This document…
 Threat Research
CVE-2026-20253 | Splunk Enterprise 10.x – Unauthenticated Arbitrary File Write to RCE via PostgreSQL Sidecar Recovery Endpoint
1. Introduction This document illustrates a Missing Authentication for a Critical Function vulnerability (CWE-306) in Splunk Enterprise, the flagship on-premises observability and Security Information and Event Management (SIEM)…