Blog
 Customer Stories
From Months to Weeks: How a Manufacturer Cut Vendor Risk Assessments to Less than 2 Weeks
For most manufacturing organizations, suppliers and service providers are a growing concern. They host data, connect to internal systems, and keep operations running smoothly. And the risk keeps…
 Threat Research
CVE-2026-34486 | Apache Tomcat: EncryptInterceptor Bypass to Remote Code Execution
1. Introduction This article examines a Missing Encryption of Sensitive Data vulnerability in Apache Tomcat, a widely deployed open-source Java servlet container. The flaw allows an attacker with…
 Threat Research
This Week’s CVE Priorities: Citrix, Check Point, F5, Cisco, and PeopleSoft Under Active Exploitation
By SAFE Threat Research Team This week’s highest-priority vulnerabilities are concentrated across technologies that sit at critical enterprise trust boundaries, including application delivery, remote access, network management, and…
 Threat Research
CVE-2026-49049 | JoomShaper Helix3 (Joomla) – Unauthenticated Arbitrary JSON File Write
1. Introduction This document illustrates an unauthenticated arbitrary file write vulnerability in JoomShaper’s Helix3 template framework for Joomla — a widely adopted front-end framework used by tens of…
 Threat Research
CVE-2026-82329 | JFrog Artifactory Blank-Join-Key Authentication Bypass (Unauthenticated Admin Takeover)
1. Introduction This document illustrates an unauthenticated authentication bypass vulnerability in JFrog Artifactory – a widely deployed universal artifact repository manager used by thousands of enterprises across the…
 TPRM
AI Cybersecurity in 2027: Why TPRM and CTEM Must Move at Machine Speed
I want to start with one sentence that I believe every CISO should think about before 2027. You cannot defend a machine speed attack surface with a calendar…
 Threat Research
CVE-2026-60004 | Gitea 1.17–1.27.0 – Pre-Authentication Remote Code Execution via diffpatch Git Hook Injection
1. Introduction This document illustrates a pre-authentication Remote Code Execution (RCE) vulnerability in Gitea, the widely deployed open-source, self-hosted Git service used by development teams, enterprises and internal…
 News
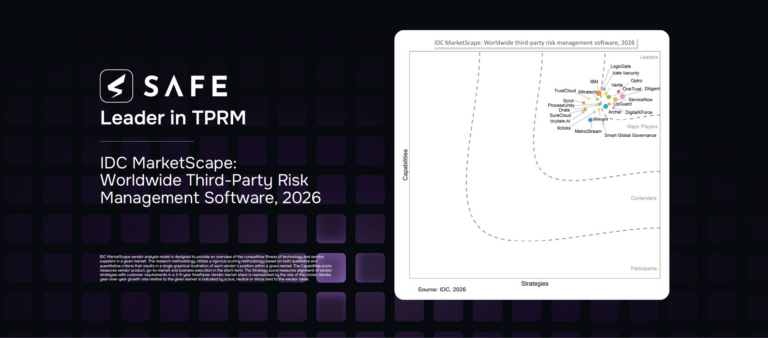
SAFE Security named a Leader in IDC MarketScape for Third Party Risk Management (TPRM) Software
Safe Security has been named a Leader in the IDC MarketScape: Worldwide Third-Party Risk Management Software 2026 Vendor Assessment. The IDC MarketScape Report evaluated vendors across 20 weighted…
 Threat Research
From Authentication Bypass to Cloud Pivot: Exploitation Is Moving Beyond the Initial Foothold
By SAFE Threat Research Team An authentication bypass in Cisco ISE can end in root access. A pre-auth flaw in Marimo can expose cloud credentials and open a…
 Trends
OpenAI Model Misalignment: Why Agentic AI Needs Guardrails and Measurable Trust
OpenAI recently introduced a new framework for tracking and disclosing model misalignment, together with six reports describing unexpected or concerning behavior observed during model training and evaluation. The…
 Events
SAFE at Gartner SRM London 2026: Put TPRM and CTEM Into Action
Cyber risk doesn’t wait for your team to clear its backlog. Vendor evidence needs review. Exposures need context, remediation needs owners, and someone has to verify that the…
 Threat Research
CVE-2026-42647 | JoomSport WordPress Plugin Unauthenticated Time-Based Blind SQL Injection via sortf Parameter – Full Database Extraction
CVSS Score: 9.3 CRITICAL | Affected: JoomSport <= 5.7.7 | Fixed: JoomSport 5.7.8+| CWE: CWE-89 – SQL Injection (ORDER BY)| CISA KEV: Not Listed 1. Introduction This document…