HIPAA Business Associate Risk: How to Run BAA Due Diligence That Protects PHI
Does a signed BAA mean your business associate is protecting PHI?
Every healthcare security leader has heard some version of this in a vendor review: “Don’t worry, they signed our BAA.” It sounds like the end of the conversation. It is closer to the start.
A business associate agreement is how you obtain what HIPAA calls satisfactory assurances that a vendor will safeguard protected health information. Under 45 CFR 164.502(e) and 164.308(b), you need those assurances before a business associate creates, receives, maintains, or transmits PHI on your behalf. But assurances on paper do not tell you whether the vendor runs multi-factor authentication on its support portal, whether its billing subcontractor in another state has a BAA of its own, or whether it can return your records when the contract ends.
The stakes are not theoretical. The February 2024 ransomware attack on Change Healthcare disrupted claims and payment processing for providers across the country, and HHS’s Office for Civil Rights published dedicated guidance on the incident. One vendor, many covered entities, one shared problem.
This guide covers what the HIPAA Privacy, Security, and Breach Notification Rules expect from business associate oversight, where programs fall short, and a practical model that holds up when an auditor, OCR, or your own board asks how you know.
Why do business associate programs fail?
Here is what nobody tells you about BAA programs: the contract is usually fine. The gaps sit around it. Five failure modes show up in almost every healthcare vendor portfolio.
You do not know who all your business associates are
The definition in 45 CFR 160.103 is broader than most procurement teams assume. It includes subcontractors that handle PHI on behalf of another business associate. HHS has also said a cloud provider that stores encrypted ePHI is a business associate even when it does not hold the decryption key, because it maintains the data. A department-purchased transcription tool or a cloud storage account set up outside procurement can become an unmanaged business associate relationship overnight.
The BAA is a template nobody compares to the regulation
Vendors often send their own BAA. Teams sign it because it has the right title. Then nobody checks it against 45 CFR 164.504(e) and 164.314(a), and the gaps (a missing termination right, vague subcontractor language, no return-or-destroy clause) only surface during an incident or an audit.
The subcontractor chain is invisible
Under 164.502(e)(1)(ii) and 164.308(b)(2), a business associate may let a subcontractor handle PHI only after obtaining the same satisfactory assurances from it. HHS guidance says the business associate must have that agreement in place before disclosing PHI to the subcontractor. You are not required to sign BAAs with your vendor’s subcontractors yourself, but you inherit their risk. If you cannot name them, you cannot assess them.
Breach reporting windows are assumed, not checked
Under 164.410, a business associate must notify you of a breach of unsecured PHI without unreasonable delay and no later than 60 calendar days after discovery. That is the outer limit, not a target. Your own notification obligations to individuals run on a clock that depends on when the breach is treated as discovered, so many covered entities negotiate shorter contractual windows. If nobody checks what the BAA actually says, you find out during the incident.
Oversight stops at the signature
Under 164.504(e)(1)(ii), a covered entity that knew of a pattern of activity or practice by a business associate that was a material breach of the contract is out of compliance unless it took reasonable steps to cure the breach or end the violation, and terminated the contract if those steps failed and termination was feasible. You cannot act on what you never look at. That is the case for continuous monitoring of business associates between scheduled reviews.
What does a defensible business associate due diligence model look like?
The short answer: five steps, each producing evidence you can produce later. The sequence mirrors how SAFE TPRM structures intake, assessment, monitoring, remediation, and offboarding, so the model works whether you run it in spreadsheets or a platform.
Step 1: Confirm business associate status and PHI exposure
At intake, answer four questions before any questionnaire goes out:
- Will the vendor create, receive, maintain, or transmit PHI for you? If yes, it is a business associate and needs a BAA before it touches the data.
- What PHI, roughly how many patient or member records, and in what form (paper, ePHI, both)?
- Which clinical or administrative systems will it access, and how (remote support, API, integration)?
- How essential is the service to care delivery or revenue cycle if it goes down for 72 hours?
An illustrative tiering rule: any business associate with access to an EHR, more than 50,000 patient records, or a role in claims and payment flows starts in the top tier. In SAFE TPRM, intake context produces an Intake Score, the inherent-risk view, kept separate from the evidence-based Exposure Score that develops as assessment and monitoring data comes in.
Step 2: Check the BAA against 164.504(e) and 164.314(a)
Use the regulation as your checklist. The contract should, among other terms:
- Establish the permitted and required uses and disclosures of PHI.
- Prohibit uses or disclosures beyond the contract or the law.
- Require appropriate safeguards, including Security Rule compliance for ePHI.
- Require reporting of unauthorized uses or disclosures, including breaches of unsecured PHI under 164.410, and security incidents.
- Require subcontractors that handle PHI to agree to the same restrictions and conditions.
- Support individuals’ rights to access, amend, and receive an accounting of disclosures.
- Make internal practices, books, and records available to the Secretary of HHS.
- Return or destroy PHI at termination, or extend protections where that is infeasible.
- Authorize termination if the business associate violates a material term.
HHS publishes sample business associate agreement provisions, and notes they are not required for compliance. Treat any gap as a tracked issue with an owner. For contract tracking across a portfolio, see vendor contract risk management.
Step 3: Verify Security Rule safeguards with evidence
Business associates are directly subject to the Security Rule’s administrative, physical, and technical safeguards. Ask for the artifacts that show it:
- The vendor’s most recent risk analysis summary and risk management plan.
- A current SOC 2 Type II report, ISO/IEC 27001 certificate, or HITRUST report, with scope covering the service you buy.
- Access control evidence: MFA coverage, privileged access, remote support controls.
- Backup and recovery test results for the systems that hold your ePHI.
- Incident response plan and the named contact for breach reporting.
Read the reports, do not just collect them. Check that the audit scope names the system or service that will hold your ePHI, that the audit period ended within the last 12 months, and whether any exceptions touch access control, logging, or backup. Note any subservice organizations carved out of scope, because those are often the hosting or support providers that actually handle your data. The risk analysis matters too: 164.308(a)(1)(ii)(A) requires an accurate and thorough assessment of risks to ePHI, and a vendor that cannot show one is telling you something.
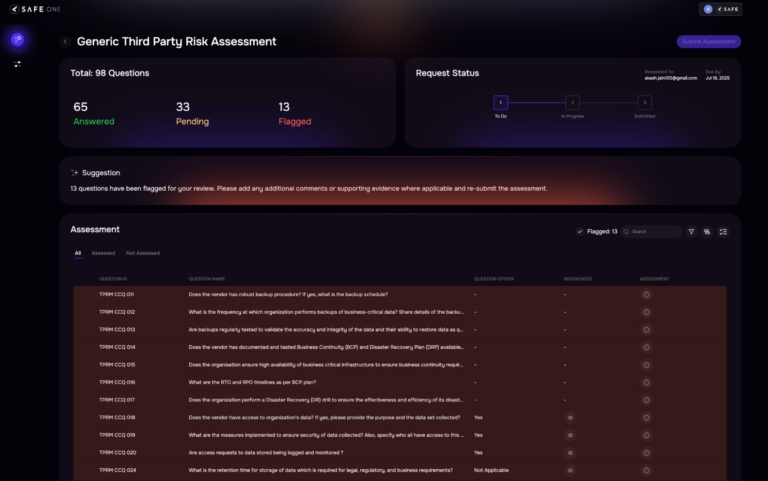
Our free healthcare vendor ePHI questionnaire covers these areas. In SAFE TPRM, document analysis reads SOC 2 and ISO evidence, suggests questionnaire answers with citations to the source document, and flags where a vendor’s answers conflict with its own reports. Analysts review and decide.
Step 4: Map the subcontractor chain
Ask every top-tier business associate for its subcontractors that handle your PHI: name, function, location, and confirmation that a BAA is in place. Look for shared dependencies. If five of your business associates run on the same claims clearinghouse or cloud region, that is concentration risk worth naming. Our guide to fourth-party risk management walks through how to scope this without drowning.
Step 5: Monitor, reassess, and plan the exit before you need it
Set reassessment triggers: a breach or incident notice, expired evidence, a material external finding on the vendor’s internet-facing infrastructure, a new subcontractor, or a scope change such as new PHI types. Then plan the exit at onboarding. The BAA’s return-or-destroy clause does little unless someone collects proof of destruction, confirms access removal, and documents any records that must be retained. Our sibling guide on vendor offboarding covers the steps.
What breaks when you manage business associates at scale?
Health systems and payers rarely have a small vendor footprint. Here is how the work grows, using an illustrative assumption that 40% of vendors are business associates:
- 200 vendors: about 80 business associates. A privacy analyst can track BAAs in a spreadsheet, but Security Rule evidence review is already a part-time job.
- 1,000 vendors: about 400 business associates. If a third are top tier and each produces a SOC 2 or HITRUST report annually, that is roughly 11 long reports a month, before questionnaires, subcontractor lists, and incident notices.
- 5,000-plus vendors: about 2,000 business associates. Nobody can answer “which business associates with EHR access lack current MFA evidence” without a structured, queryable record.
What breaks is not just volume. It is the link between findings and action. A gap found in March sits in a report until the next annual review. SAFE TPRM connects assessment findings to tracked remediation with owners and status, and its portfolio reporting shows coverage and open issues across every business associate. San Francisco Health Plan uses SAFE to speed up third-party risk assessments by 90%.
Which business associate trade-offs do healthcare teams actually face?
Three tensions come up in nearly every healthcare program. None of them has to be an either/or.
Clinical urgency versus review depth
A clinical department needs a new telehealth or diagnostics vendor live in two weeks. A full review takes six. Tiering is the answer: get the BAA signed before any PHI flows, run a targeted evidence review scaled to PHI exposure, and track open items as issues with deadlines rather than blocking go-live indefinitely. SAFE TPRM routes vendors to questionnaire profiles based on intake context, so a scheduling app and an EHR integrator do not get the same 300 questions.
Your BAA versus theirs
Large EHR, cloud, and clearinghouse vendors will insist on their own paper. Accept that, then review their BAA against 164.504(e) and record each deviation as a decision. A documented, approved exception is defensible. An unread vendor template is not. Pay closest attention to three terms: the breach reporting window, the subcontractor clause, and what happens to PHI at termination. Those are where vendor templates tend to diverge from what your incident response and offboarding plans assume.
Today’s rule versus the proposed one
In January 2025, HHS published a proposed Security Rule update. Among other changes, it would require covered entities to obtain written verification from business associates, at least every 12 months, that required technical safeguards are in place, supported by a written analysis and certification. As of this writing it remains a proposal, and the current rule still applies. Building evidence-based oversight now covers today’s obligations and puts you in position if the rule is finalized. SAFE TPRM supports periodic reassessment with pre-fill from prior responses, so an annual cycle does not mean starting from zero.
Why SAFE TPRM for HIPAA business associate risk?
We built SAFE TPRM because lean healthcare security and privacy teams were managing hundreds of business associates with spreadsheets, shared inboxes, and PDFs nobody had time to read. The platform supports the evidence, assessment, monitoring, and reporting work behind business associate oversight. It does not make you HIPAA compliant on its own, and it does not replace your privacy officer’s or counsel’s judgment.
What the platform does today:
- Governed intake and tiering that captures PHI exposure, system access, and criticality, with separate Intake Score (inherent) and Exposure Score (residual) views.
- Document analysis of SOC 2 and ISO evidence that extracts controls, exceptions, audit periods, and subservice organizations, and suggests answers with citations.
- AI review that flags vague, unsupported, or conflicting answers for analyst attention, with humans approving material decisions.
- Contract analysis that surfaces relevant terms from vendor agreements for reviewer attention.
- Continuous Outside-In monitoring that shows what changed in a vendor’s external exposure and supports reassessment.
- Issues, remediation, and offboarding workflows that keep accountability visible through the exit.
Read more about TPRM in healthcare, see the lifecycle in SAFE TPRM in action, or schedule a demo.
Frequently Asked Questions
Under 45 CFR 160.103, a business associate is a person or entity that performs functions or services for a covered entity that involve creating, receiving, maintaining, or transmitting protected health information. The definition also covers subcontractors that do the same on behalf of another business associate. Common examples include billing and revenue cycle vendors, EHR and cloud hosting providers, transcription services, and IT support firms with system access. HHS has stated that a cloud provider storing encrypted ePHI is still a business associate even without the decryption key.
The required terms are set out in 45 CFR 164.504(e) and, for ePHI, 164.314(a). They include permitted uses and disclosures, safeguards, reporting of unauthorized uses and breaches, flow-down to subcontractors, support for individual rights, access for the Secretary of HHS, return or destruction of PHI at termination, and a termination right for material violations. HHS publishes sample provisions you can adapt. See our overview of TPRM compliance frameworks for how HIPAA fits alongside SOC 2 and ISO 27001.
Yes, for specific requirements. The HITECH Act and the 2013 final rule made business associates directly liable for, among other things, Security Rule compliance, breach notification to the covered entity, impermissible uses and disclosures, and failing to sign BAAs with subcontractors. Direct liability does not remove your own obligations as the covered entity, including acting on known material breaches of the BAA. This page is general information, not legal advice. Confirm your obligations with counsel.
Under 45 CFR 164.410, without unreasonable delay and no later than 60 calendar days after discovering a breach of unsecured PHI. Many covered entities negotiate a shorter window in the BAA so they have time to meet their own obligations. SAFE TPRM can treat a reported incident as a reassessment trigger and track the follow-up as an issue with an owner, so the response does not live in an email thread.
Set a cadence by tier, for example annually for business associates with EHR access or large PHI volumes and every two to three years for low-exposure ones, then add event triggers such as incidents, expired evidence, new subcontractors, and material external findings. SAFE TPRM supports both periodic and event-driven reassessment and pre-fills new assessments from prior responses and previously submitted documents.
If finalized as proposed, yes. The January 2025 proposal would require covered entities to obtain written verification from business associates, at least every 12 months, that required technical safeguards are deployed, and business associates would obtain the same from their subcontractors. It is a proposal, not a final rule, as of this writing. Programs that already collect current safeguard evidence on a set cadence will have less to change. Our sibling guide on SOC 2 third-party requirements covers how to read the reports you will lean on.