Third-Party Risk Management
for Financial Services
Reduce breach exposure from providers handling transactions, account information, and critical banking services.

Business challenges
-
Limited visibility into critical vendor dependencies can disrupt payment rails and core banking.
-
Hidden fourth parties can disrupt payment rails and core banking.
-
Weak vendor controls can expose accounts, transactions, and customer data.
-
Scattered evidence complicates reviews under DORA, GLBA, and FFIEC guidance.
-
Incomplete vendor exits leave payment access and customer data exposed.
Protect financial operations across
every vendor relationship
SAFE TPRM AI Co-Worker drives intake, due diligence, remediation, monitoring, and offboarding, helping financial institutions scale vendor oversight while retaining human control over critical decisions.
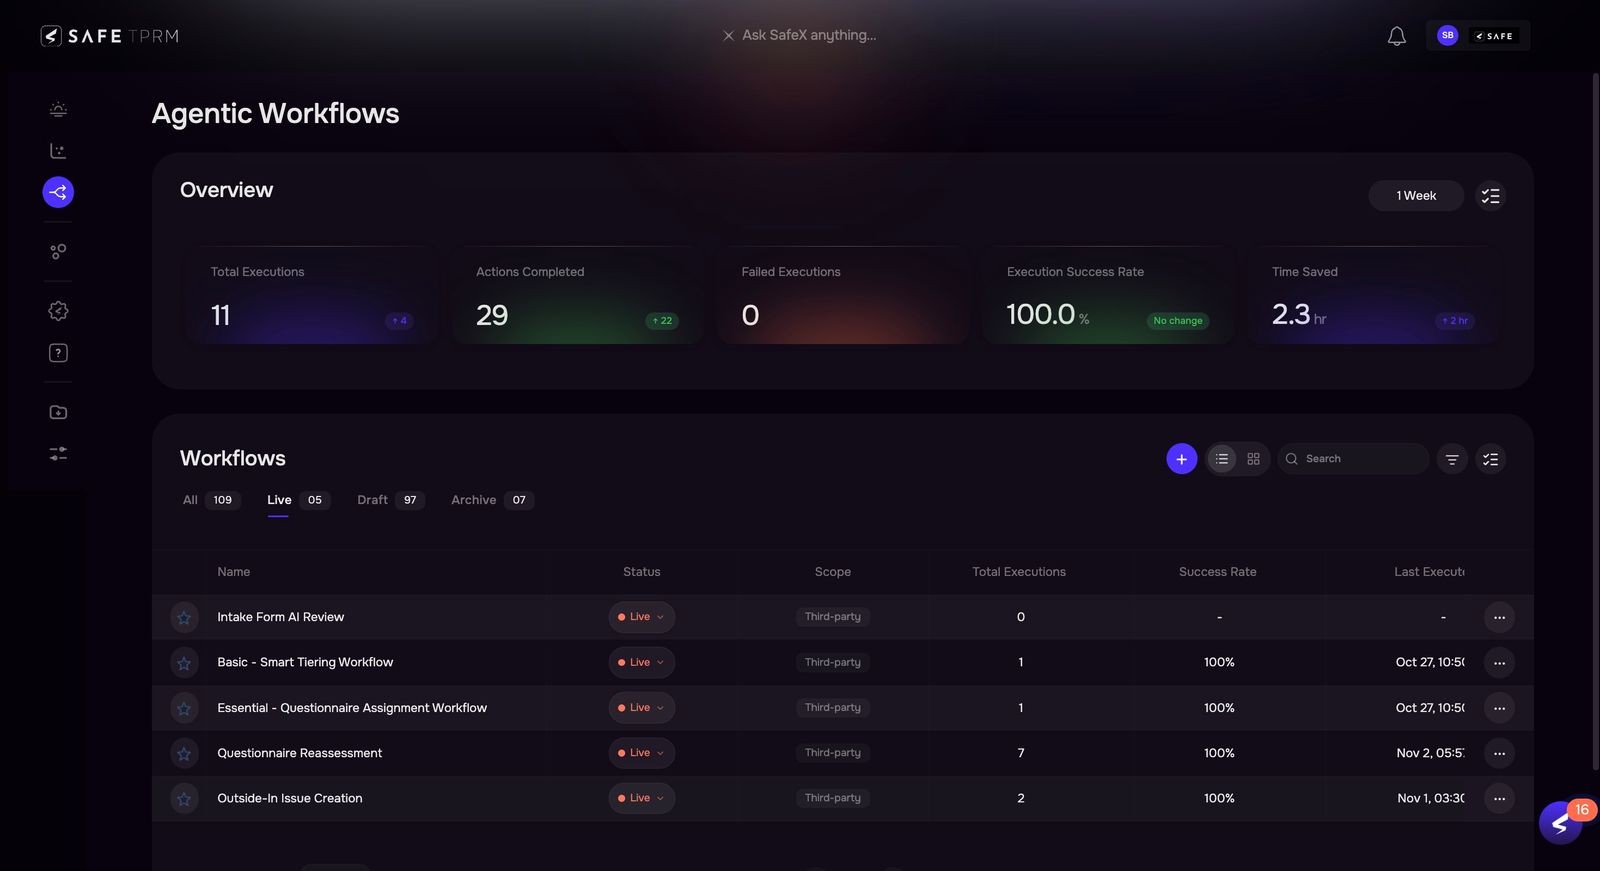
Accelerate onboarding for critical financial partners
Bring fintech partners, payment providers, and banking technology vendors onboard faster with risk-based intake and zero-touch due diligence.
Establish risk upfront: Enrich vendor profiles using intelligence from 60M+ companies and assess customer data access, operational dependency, and service criticality.
Focus every assessment: Tailor questions, evidence requirements, and approval paths to the vendor's services and risk tier.
Remove the follow-up burden: Let the AI Co-Worker collect documents, review responses, and resolve missing information directly with vendors through agentic workflows.
Route decisions efficiently: Automatically direct high-risk findings, exceptions, and approval requests to the right stakeholders for timely review.

Expose dependencies that threaten financial operations
Understand how third- and fourth-party exposures could affect payments, core banking, and customer-facing services.
Reveal hidden concentration: Identify shared providers and downstream dependencies across your vendor ecosystem.
Keep oversight current: Correlate outside-in signals, questionnaires, documents, contracts, and threat intelligence to surface material changes.
Trigger a timely response: Initiate reassessments, remediation, or escalation when relevant breaches or deteriorating controls affect critical vendors.
Prioritize operational impact: Rank dependencies by their potential effect on payment continuity, customer access, regulatory obligations, and recovery plans.
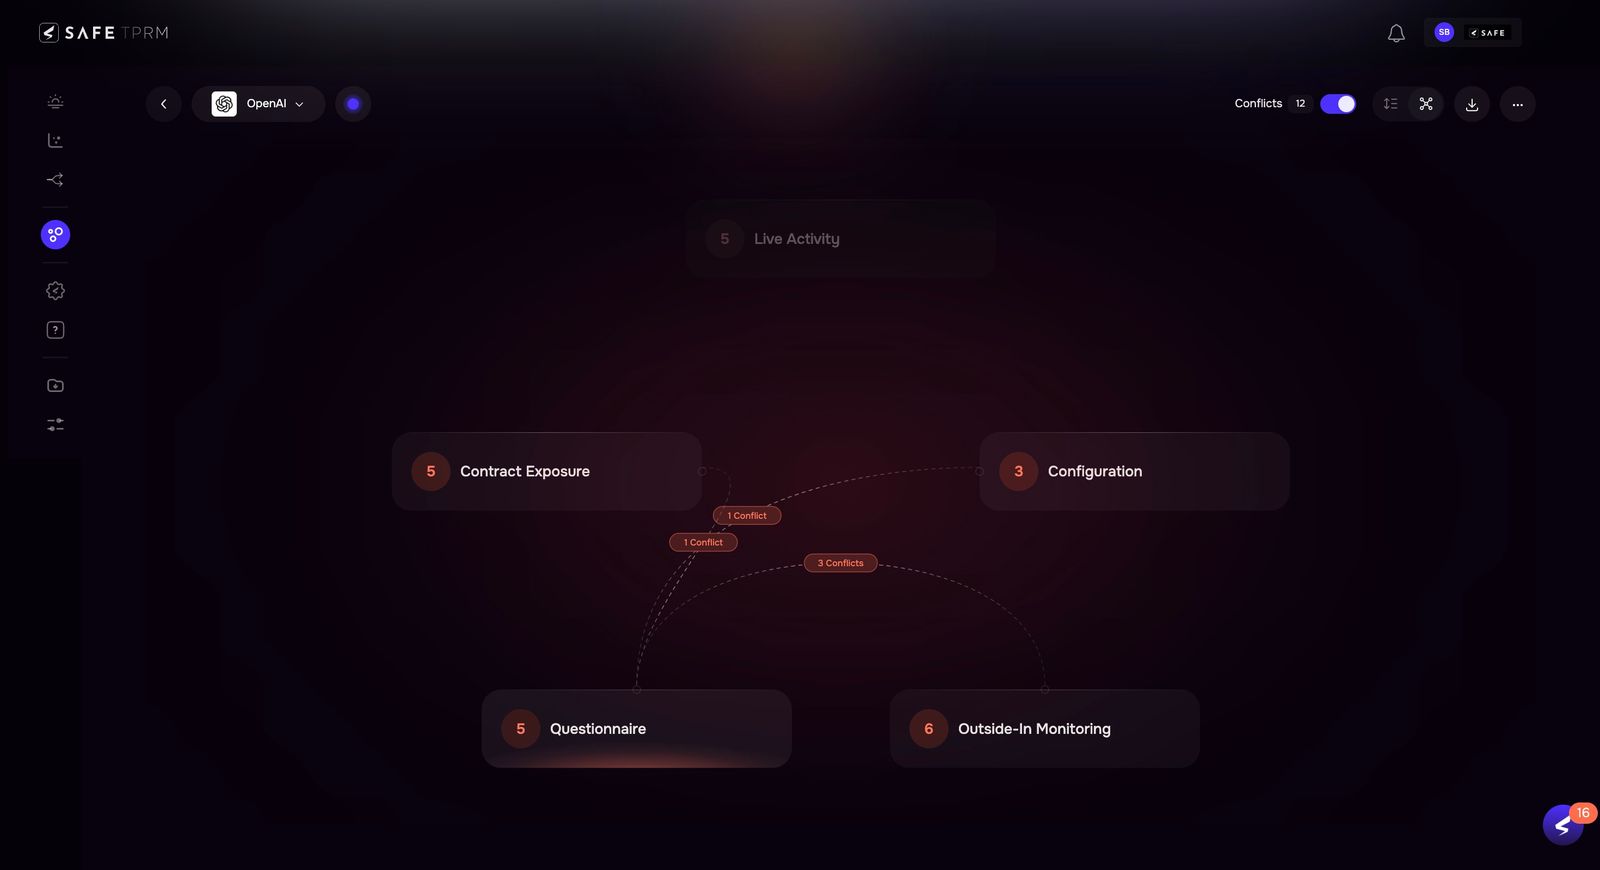
Close vendor gaps that put customer data at risk
Turn conflicting evidence and control weaknesses into accountable remediation, prioritized by business exposure.
Challenge unsupported claims: Detect discrepancies between vendor responses, SOC reports, contractual commitments, and external findings.
Drive vendors toward resolution: Assign actions, owners, and deadlines; request evidence; and automatically escalate overdue work through agentic workflows.
Validate the outcome: Review remediation evidence and route exceptions or risk acceptance to designated decision-makers.
Measure remediation progress: Track recurring issues, overdue actions, and control improvements across vendors to identify systemic risk trends.

Make vendor oversight defensible under scrutiny
Give risk, compliance, and audit teams a traceable record of how vendors are assessed, monitored, and managed.
Connect findings to evidence: Link assessment answers and control gaps to source documents, pages, and supporting text.
Apply consistent governance: Configure review criteria, evidence requirements, and approval thresholds around institutional policies and applicable requirements.
Explain every decision: Preserve findings, vendor communications, remediation history, and approvals so teams can demonstrate how risk was addressed.
Generate review-ready reporting: Produce consistent summaries of vendor risk, control status, exceptions, and oversight activity for audits, committees, and regulators.
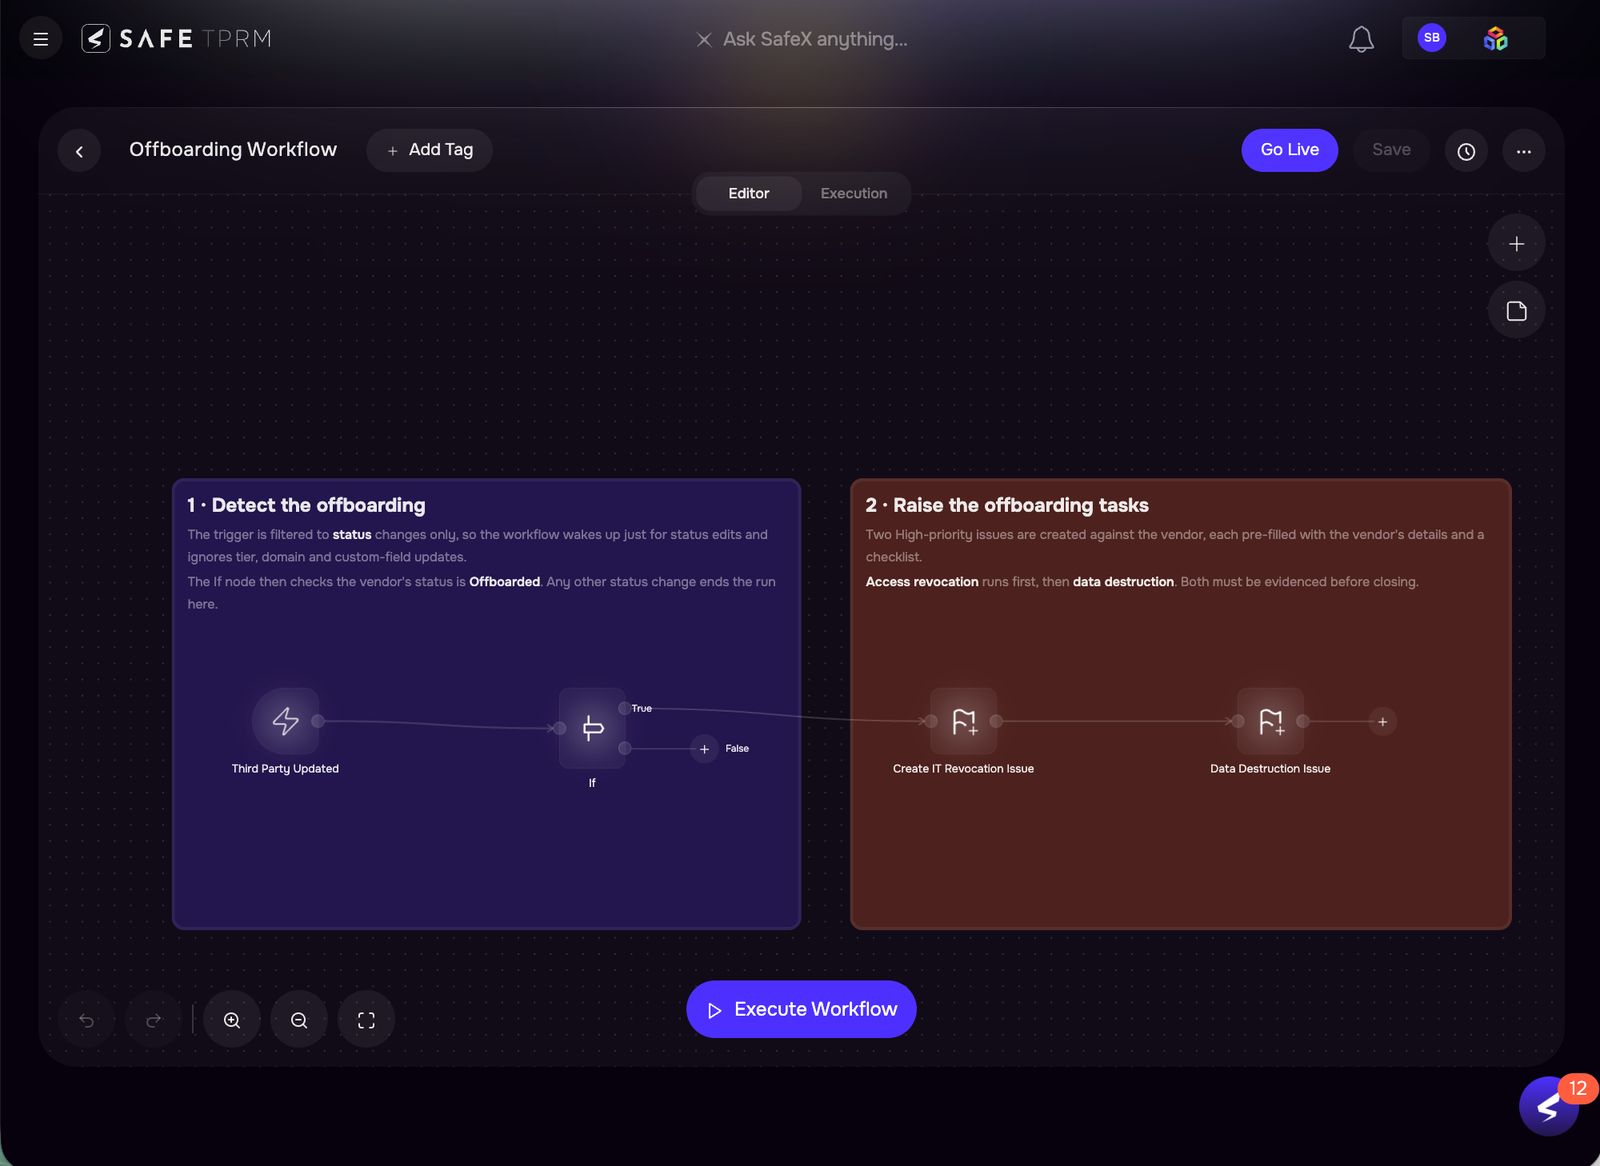
Close vendor relationships with evidence and control
Coordinate vendor exits so customer information, system access, and outstanding obligations remain accountable through termination.
Orchestrate the exit: Use 20+ automated offboarding workflows to coordinate security, IT, privacy, procurement, legal, and business owners.
Track access and data closure: Collect confirmation of access revocation, integration deactivation, and customer data return or deletion.
Resolve remaining exposure: Escalate outstanding issues, document accepted risks, and preserve an audit-ready exit record.
Confirm post-termination obligations: Monitor retention requirements, transition activities, and continuing contractual responsibilities until closure is verified.
Built for everyone who owns vendor risk
CISO
Protect critical financial services and customer trust with continuous visibility into vendor exposures, emerging threats, and the remediation actions that matter most.
Head of TPRM
Scale oversight across fintech partners, payment providers, and critical suppliers with autonomous workflows, consistent governance, and clear accountability throughout the vendor lifecycle.
TPRM Analyst
Spend less time chasing questionnaires and reconciling documents. Review cited evidence, investigate meaningful changes, and drive vendor issues to verified resolution.
Financial services teams running on SAFE

Trusted By 10% of Fortune 500


Related Resources
 Third Party Risk Management
TPRM for Financial Services
Why Third-Party Risk in Financial Services Is a Different Category of Problem Most industries face vendor risk. Financial services faces vendor risk and three additional layers of pressure…

 Third Party Risk Management
Vendor Contract Risk Management
The Contract Is a Risk Document. Your Team Is Not Treating It That Way. Somewhere in your contract repository there is a vendor agreement that specifies how long…
 TPRM
Healthcare Providers Need a New TPRM Playbook
Why Traditional TPRM Fails Healthcare Providers and What Needs to Change By: Sweta Bhattacharya In healthcare, a vendor breach is a clinical crisis. When a supplier goes dark, the…


 Datasheets
Effortlessly Scale TPRM Across Customer Tenants
SAFE TPRM is the industry’s first Agentic AI-driven, multi-tenant Third-Party Risk Management platform, purpose-built for MSSPs. Orchestrating 100+ specialized AI Agents, it automates vendor intake, due diligence, remediation,…
 Third Party Risk Management
How to Get Internal Buy-In for TPRM
The Policy Is Written. Nobody Is Following It. The TPRM policy is documented and approved. The process is posted on the intranet. Business units are still onboarding vendors…