A breach or outage during peak season hits revenue and brand trust at the worst moment.
02
Seasonal launches, campaigns, and agency work spin up new internet-facing assets faster than security can review.
03
Payment, loyalty, and purchase data bring PCI DSS and privacy obligations.
04
Thousands of stores, POS endpoints, and e-commerce services sprawl across tools and teams.
05
Change freezes narrow the window to fix anything.
How SAFE Helps
Run CTEM on a retail calendar
The SAFE CTEM AI Co-Worker keeps exposure work moving between peaks and focuses it on what protects sales.
Scoping: Start with what keeps revenue flowing
Scoping that starts with the business, not the scanner.
Identify revenue-critical systems:
The Asset Criticality Agent flags checkout, payment, order management, and customer-data systems.
Organize the way retail works:
Business groups by channel, brand, region, store estate, or environment.
Include partners in the picture:
Connect first-party assets and third parties, such as payment and fulfillment partners, within common business groups.
Know where sensitive data lives:
Surface assets holding payment and customer data, not just generic knowledge.
Discovery: See every store, storefront, and campaign site
One prioritized view you can rely on.
One graph, 150+ tools:
Unify exposure data across your stack without replacing the specialized tools you use.
Zero-drop ingestion:
Deduplicated, normalized findings with no data loss.
Find the forgotten:
Reveal shadow IT, abandoned campaign infrastructure, and unmanaged cloud.
Respond to zero-days fast:
Correlate a newly disclosed vulnerability across your estate in one place.
Prioritization: Same CVE, different business risk
CVSS tells you how severe. SAFE tells you what it costs.
Weigh what’s at stake:
A flaw on a payment or checkout service ranks against one on a back-office server using business impact, exposure, threat activity, and controls.
Quantify the loss:
Show which fixes avoid the most financial risk.
Cut the noise:
Fully mitigated criticals can drop, and reachable, unprotected ones rise.
Show your work:
Every ranking is explainable to a CISO, auditor, or store operations lead.
Validation: Confirm what’s really exploitable
Before you disrupt the business to deploy the patch, your Co-Worker confirms it’s worth disrupting for.
Measure control effectiveness:
WAF, segmentation, EDR, and hardening are assessed for relevance and evidence, not just presence.
Prove reachability:
Confirm which internet-facing exposures can actually be reached and exploited.
Adversarial Exposure Validation:
Safely test exploitability so peak-season change windows go to real risk.
Reduce unnecessary changes:
Avoid disruptive patching for exposures already neutralized.
Mobilization: Get fixes done inside the freeze calendar
From findings to fixes.
Route to the right team:
The Ownership Resolution Agent finds the e-commerce, store, or infrastructure owner.
Initiate the fix:
The Remediation Ticketing Agent creates tickets with context and evidence.
Track vendor patches:
Patch Intelligence follows availability and drives next steps.
Document the trade-offs:
The Exception Agent records time-bound risk acceptance for items deferred through peak periods, with audit trail and SLA reporting.
Who Wins?
Built for everyone who owns exposure
CISO
Protect sales and shopper trust with exposure reported in business terms.
Head of Vulnerability / Exposure Management
Prioritize by checkout and customer impact, not raw severity.
Security Operations Analyst
Stop chasing owners and duplicate findings, and focus on the exposures that matter.
Exposure ManagementThe Comprehensive Exposure Management GuideExposure management in cybersecurity is the process of identifying, assessing, and mitigating potential vulnerabilities and threats to minimize the risk of cyberattacks on an organization’s assets. Unlike traditional…SAFESafe SecurityFeb 23, 202614 min read
Exposure ManagementUnderstanding Continuous Threat Exposure Management (CTEM)Cybersecurity threats evolve faster than traditional defenses can adapt. Organizations face hundreds of vulnerabilities daily, but not all pose an immediate risk. How do you determine which ones…SAFESafe SecurityFeb 23, 202610 min read
CTEMHow CTEM Turns Vulnerability Data Into Risk ReductionSeries: Understanding CTEM and Why It Matters | Part 2 of 3: Scoping, Discovery, and Prioritization By: Ramesh Ramachandran In the first blog of this series, we talked about…SAFESafe SecuritySep 1, 20269 min read
Exposure ManagementContinuous Exposure Management ProgramGartner Defined CTEM in 2022. Most Teams Are Still Running 2015 Processes. Gartner introduced the Continuous Threat Exposure Management framework in 2022 to describe a structured approach to…SAFESafe SecurityJul 16, 202611 min read




 Exposure Management
The Comprehensive Exposure Management Guide
Exposure management in cybersecurity is the process of identifying, assessing, and mitigating potential vulnerabilities and threats to minimize the risk of cyberattacks on an organization’s assets. Unlike traditional…
 Exposure Management
Understanding Continuous Threat Exposure Management (CTEM)
Cybersecurity threats evolve faster than traditional defenses can adapt. Organizations face hundreds of vulnerabilities daily, but not all pose an immediate risk. How do you determine which ones…
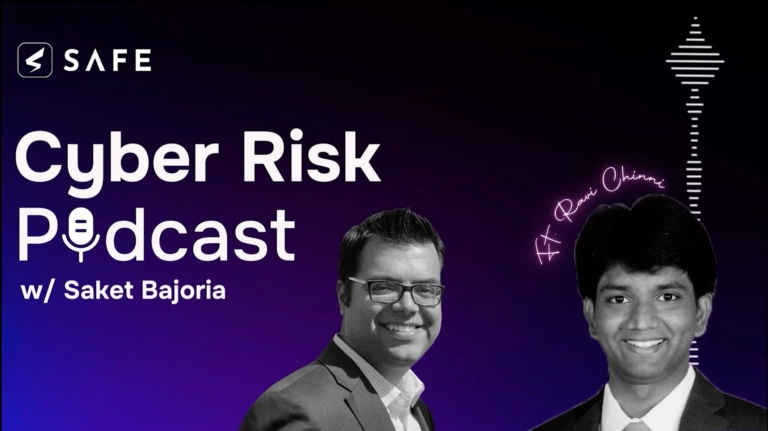 Podcasts
The Cyber Risk Podcast with Ravi Chinni, S&P Global, on Scaling Cyber Risk Bottom-Up
How to ensure teams take the right actions and executives stay informed on cyber risk burndown. In Episode Six of The SAFE Cyber Risk Podcast, host Saket Bajoria,…
 CTEM
Shift Two: Centralizing Exposure Data Is Not the Same as Understanding It
Part 3 of a four-part series on what the defender’s window requires at enterprise scale. Risk-based prioritization only works when the underlying exposure data can be reconciled, contextualized,…
 CTEM
Shift One: Why CTEM Has to Prioritize Business Risk, Not Severity
Part 2 of a four-part series on what the defender’s window requires at enterprise scale. In the first article in this series, we argued that the defender’s window…
 CTEM
How CTEM Turns Vulnerability Data Into Risk Reduction
Series: Understanding CTEM and Why It Matters | Part 2 of 3: Scoping, Discovery, and Prioritization By: Ramesh Ramachandran In the first blog of this series, we talked about…
 CTEM
The Defender’s Window Is Open. Here Is What Enterprise Security Has to Change.
Part 1 of a four-part series on what the defender’s window requires at enterprise scale. This week, OpenAI and more than 100 organizations, including Google, Microsoft, CrowdStrike, and…
 Exposure Management
Continuous Exposure Management Program
Gartner Defined CTEM in 2022. Most Teams Are Still Running 2015 Processes. Gartner introduced the Continuous Threat Exposure Management framework in 2022 to describe a structured approach to…