Blog
 Blog
Third Party Breach Detection and Notifications with SAFE TPRM
Your vendor passed its assessment. The questionnaire is complete, the security report is on file, and the next review is months away. Then someone forwards a breach headline…
 Blog
Best Third Party Risk Management Solutions
A buyer’s guide for 2026 and 2027 to what modern TPRM platforms really do, and how SAFE Security handles vendor risk from the first intake form to the…
 Threat Research
CVE-2026-33032 nginx-ui ≤ 2.3.3 – Unauthenticated MCP Authentication Bypass via Missing AuthRequired() Middleware on /mcp_message
1. Introduction This document illustrates an unauthenticated authentication bypass in nginx-ui, the open-source web interface used to manage Nginx web servers. The flaw lets an anonymous network client…
 Blog
Gartner UK from the Practitioner’s Seat: Everyone Wants to Be an Orchestrator. Now What?
Be an orchestrator. Don’t buy, build. Automate the low-level tasks so your team can focus on the work that matters. Those are just a few of the buzzwords…
 Blog
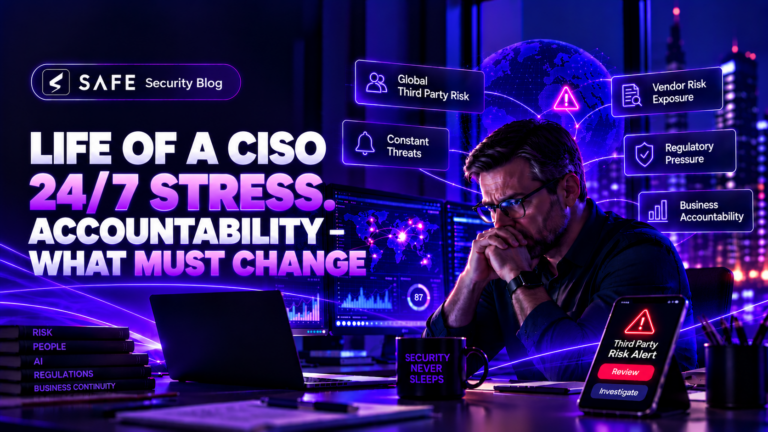
Life of a CISO in the Frontier AI Era : The Thankless Job With 24/7 Stress and What Must Change
What breach cases, boardroom pressure, budget gaps and AI-enabled attacks reveal about the world’s most exposed executive role A CISO’s job can feel thankless. The organization expects continuous…
 Threat Research
CVE-2026-87902 WordPress: Unauthenticated Path Traversal Leading to Conditional RCE
1. Introduction CVE-2026-87902 is an unauthenticated path traversal vulnerability in WordPress page-template resolution. Under specific theme and server conditions, a remote attacker can include a readable local PHP…