Third-Party Risk Management
for Retail
Reduce third-party breach exposure across payment, loyalty, marketing, and fulfillment partners.

Business challenges
-
Third-party outages trigger costly, long-term disruptions across critical business operations.
-
Accelerated peak-season onboarding often outpaces thorough vendor security reviews under tight deadlines.
-
Retail partners handle extensive customer and payment data, where security exposure severely damages brand trust.
-
Hidden Nth-party dependencies disrupt omnichannel sales channels.
-
Siloed vendor documentation complicates compliance and privacy oversight
Protect sales and revenue across
every vendor relationship
The SAFE TPRM AI Co-Worker automates workflows across intake, due diligence, remediation, continuous monitoring, and offboarding, enabling retailers to safeguard revenue, protect customer data, and scale third-party risk management through peak seasonal demand.
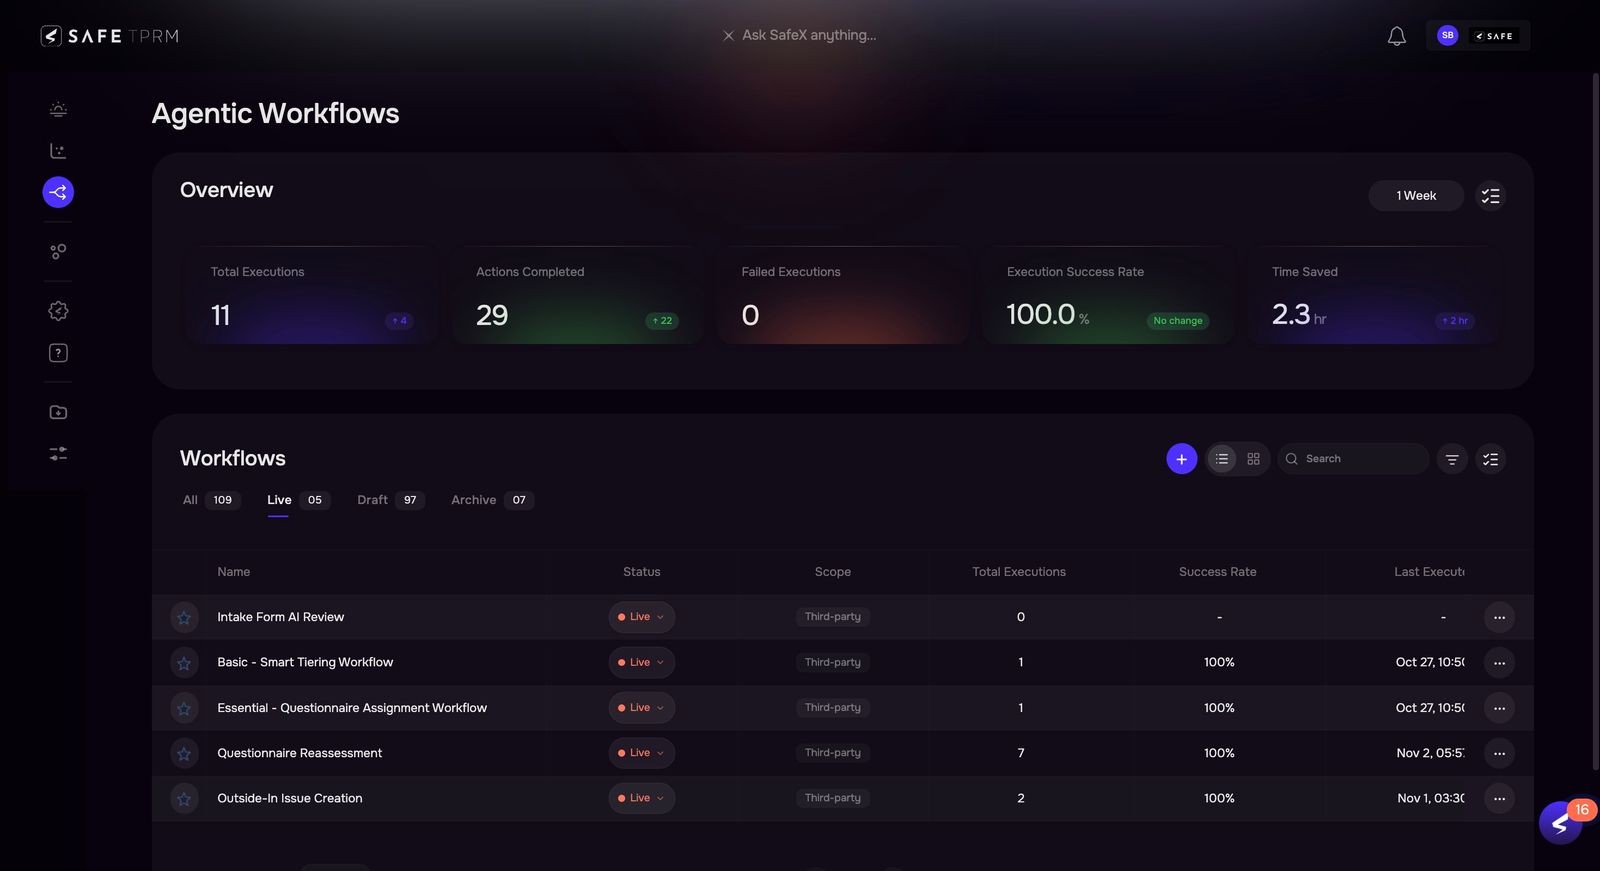
Accelerate vendor onboarding for retail launches
Efficiently onboard payment, e-commerce, marketing, and fulfillment partners using risk-based due diligence tailored to their system access and role in the customer journey.
Establish retail context upfront: Capture whether vendors support checkout, handle customer profiles, connect to inventory systems, or enable order fulfillment.
Tailor assessments to the relationship: Apply different evidence requirements to a payment processor, a loyalty platform, a digital agency, and a warehouse technology provider.
Review readiness for critical trading periods: Assess vendor recovery plans and incident response commitments against your requirements for sales availability and service restoration.
Eliminate assessment backlogs: Leverage autonomous AI agents to collect documentation, analyze responses, and track missing evidence while seamlessly routing launch approvals and exceptions to accountable stakeholders.

Expose dependencies that threaten checkout and fulfillment
Gain complete visibility into how vendor incidents impact order intake, payment processing, and fulfillment reliability.
Reveal shared points of failure: Identify common technology providers and subcontractors supporting multiple storefronts, payment services, or fulfillment partners.
Connect dependencies to retail operations: Assess vendor criticality using the channels, locations, and services that depend on the relationship.
Maintain continuous risk monitoring: Correlate threat intelligence, external ratings, questionnaires, certifications, and contracts to detect material changes in vendor risk profiles between formal reviews.
Mobilize the affected business teams: Trigger reassessment and escalation to ecommerce, store operations, payments, or logistics owners based on the service at risk.
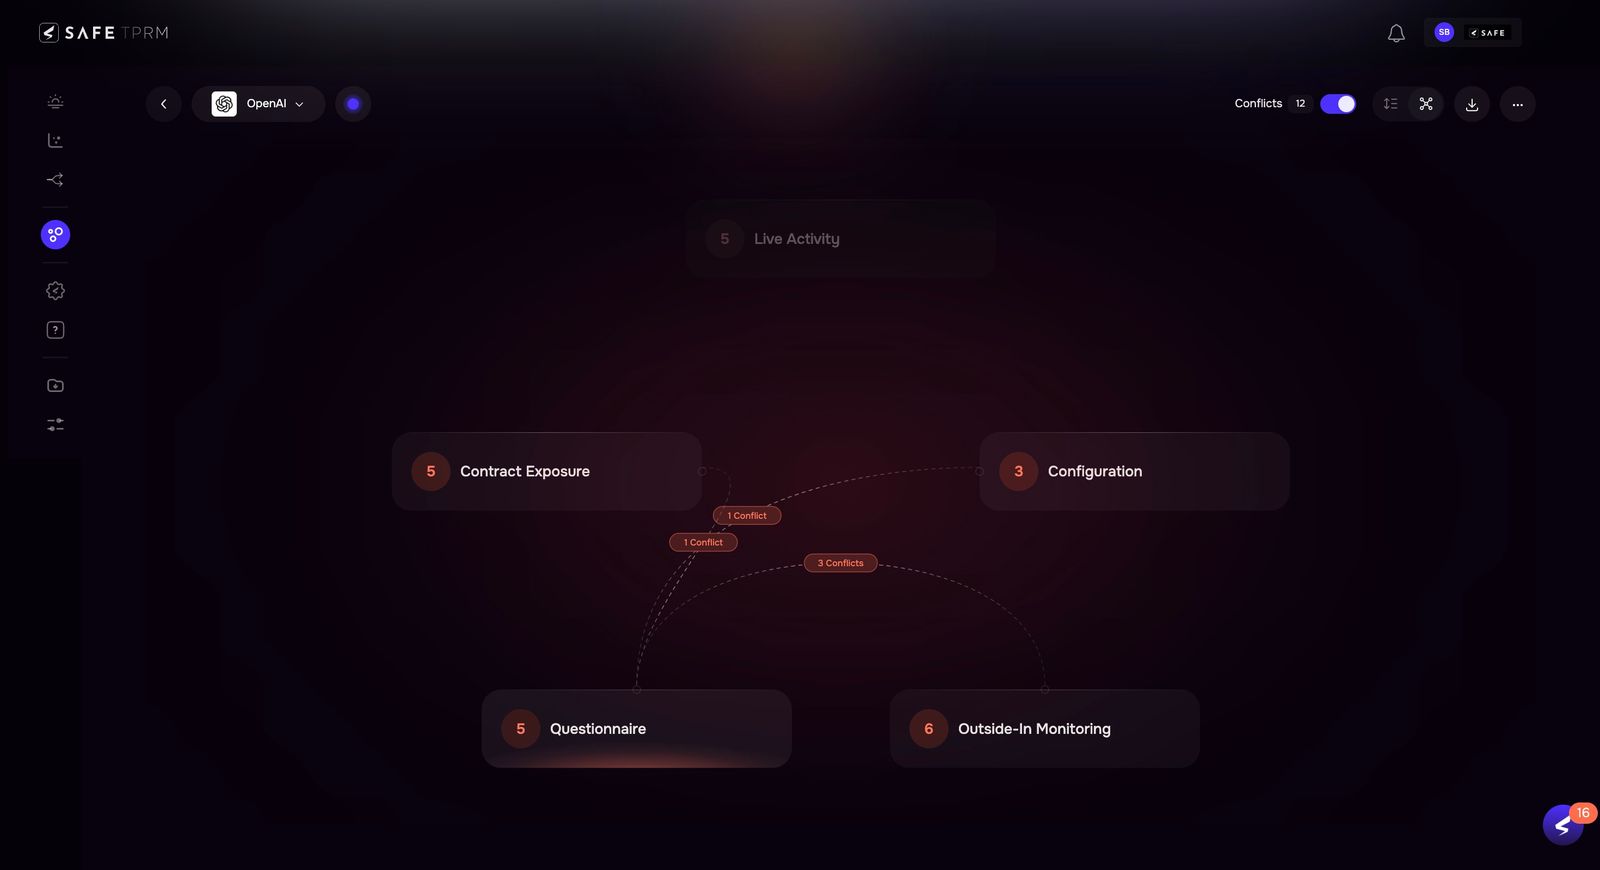
Close vendor gaps that expose shoppers and stores
Accelerate remediation of security gaps across payment infrastructure, customer data environments, and third-party access points.
Challenge access-control assurances: Compare vendor claims about authentication, privileged access, and remote support with evidence covering point-of-sale and ecommerce services.
Scrutinize customer data handling: Identify conflicts between contractual commitments and evidence about how partners protect, share, or retain loyalty profiles and purchase histories.
Drive action across vendor owners: Use agentic workflows to assign corrective actions, request evidence, and escalate overdue issues to the teams managing each relationship.
Verify fixes with business oversight: Validate remediation responses and route changes affecting checkout or fulfillment to appropriate operational approvers.

Make payment and privacy oversight defensible
Provide security, risk, compliance, and procurement teams with a unified, audit-ready record of vendor commitments and supporting evidence.
Validate payment compliance scope: Verify PCI DSS attestations and supporting documentation to confirm coverage spans all utilized vendor services and infrastructure.
Clarify shared responsibilities: Extract contractual security commitments and flag gaps in ownership between the retailer, payment providers, and supporting technology partners.
Review customer data obligations: Assess commitments for permitted data use, retention, subcontractor access, and incident notification against configured privacy requirements.
Keep review evidence connected: Link findings to source documents, vendor clarifications, corrective actions, and approvals so teams can substantiate oversight decisions.
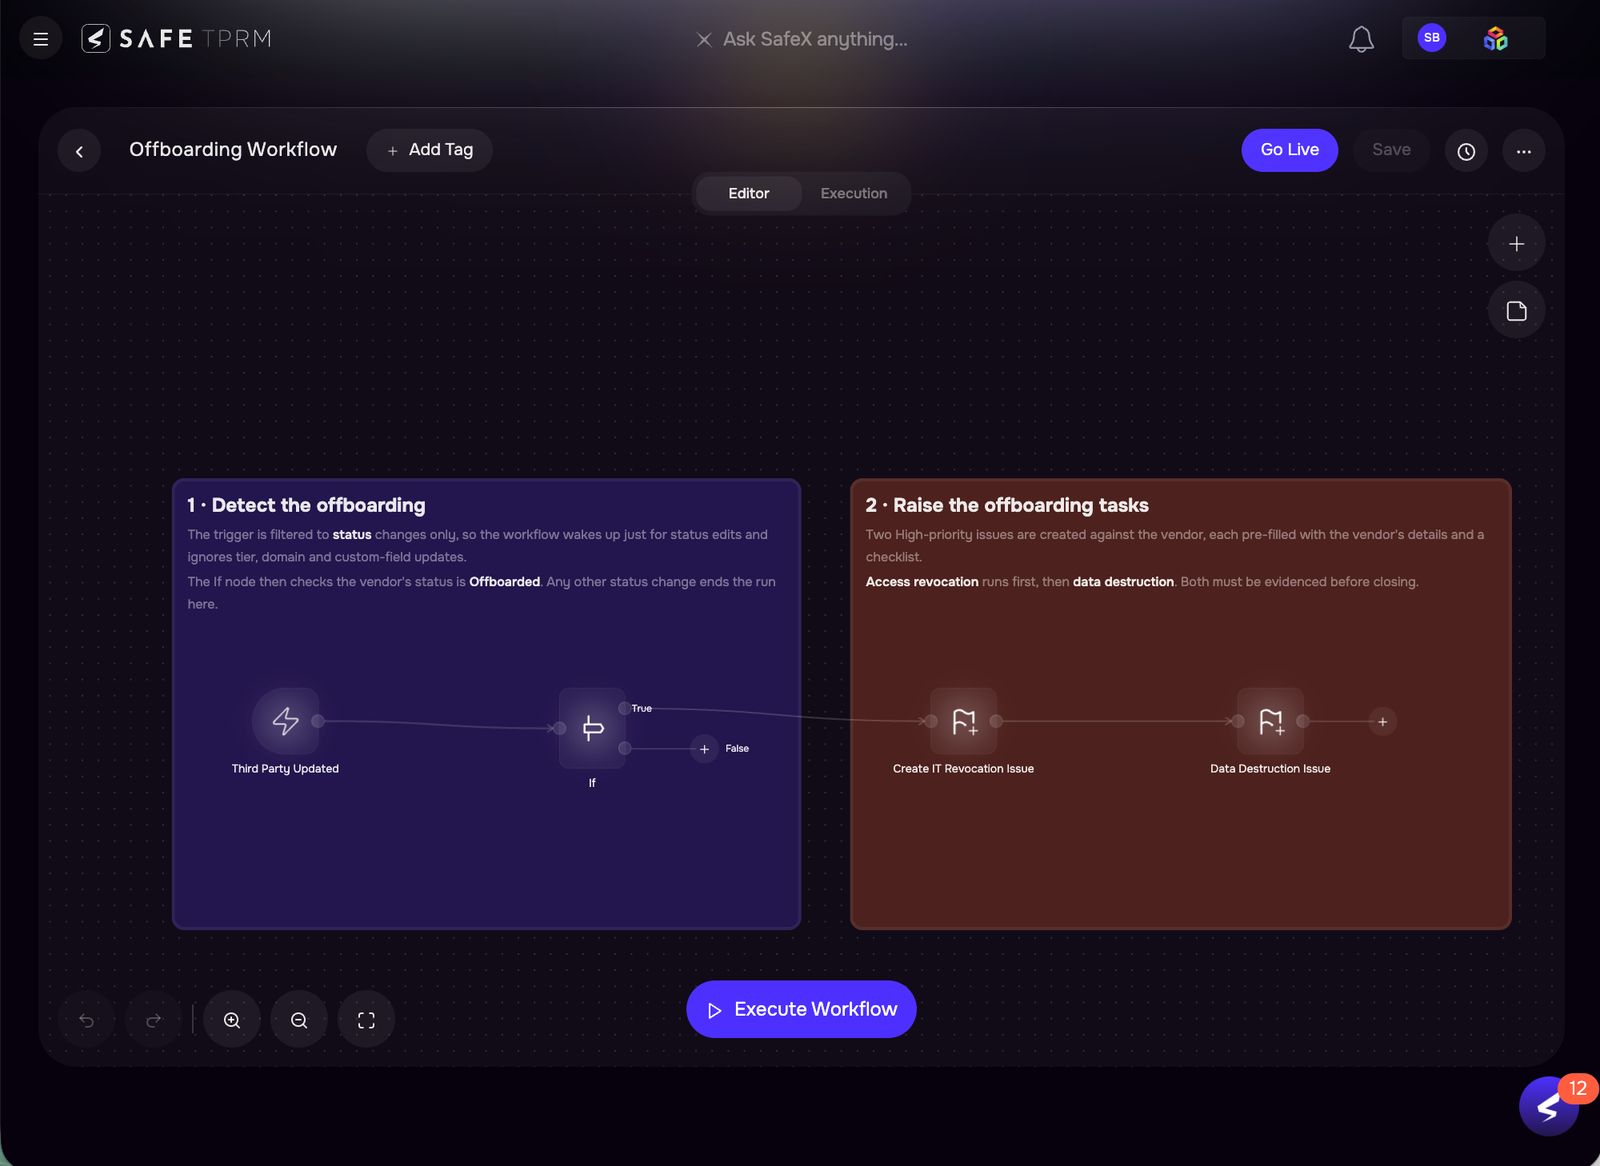
Close vendor access when campaigns and contracts end
Orchestrate offboarding across marketing, e-commerce, store operations, IT, and procurement to eliminate residual exposure when campaigns or contracts conclude.
Automate milestone-driven offboarding: Deploy over 20 pre-built workflows to coordinate system and access revocation when campaigns finish, seasonal services end, or vendor contracts expire.
Confirm retail access removal: Collect confirmation that agency accounts, vendor credentials, API connections, and remote support access have been revoked or deactivated.
Account for shared shopper information: Track the return or deletion of customer lists, loyalty data, and order records, documenting approved retention obligations.
Coordinate outstanding service obligations: Assign owners for transition tasks, unresolved risks, and continuing responsibilities for orders, returns, or customer support before final closure.
Built for everyone who owns vendor risk
CISO
Protect sales and shopper trust with continuous visibility into vendor exposures affecting checkout, customer information, and retail operations.
Head of TPRM
Scale oversight across payment, ecommerce, marketing, and fulfillment partners with agentic workflows and priorities tied to trading periods and customer impact.
TPRM Analyst
Eliminate manual evidence collection and vendor follow-ups. Focus on investigating high-priority risk gaps and driving targeted remediation around payment security, data protection, and operational continuity.
Retail teams running on SAFE

Trusted By 10% of Fortune 500


Related Resources
 Third Party Risk Management
TPRM for Financial Services
Why Third-Party Risk in Financial Services Is a Different Category of Problem Most industries face vendor risk. Financial services faces vendor risk and three additional layers of pressure…
 Third Party Risk Management
Vendor Contract Risk Management
The Contract Is a Risk Document. Your Team Is Not Treating It That Way. Somewhere in your contract repository there is a vendor agreement that specifies how long…
 TPRM
Healthcare Providers Need a New TPRM Playbook
Why Traditional TPRM Fails Healthcare Providers and What Needs to Change By: Sweta Bhattacharya In healthcare, a vendor breach is a clinical crisis. When a supplier goes dark, the…


 Datasheets
Effortlessly Scale TPRM Across Customer Tenants
SAFE TPRM is the industry’s first Agentic AI-driven, multi-tenant Third-Party Risk Management platform, purpose-built for MSSPs. Orchestrating 100+ specialized AI Agents, it automates vendor intake, due diligence, remediation,…
 Third Party Risk Management
How to Get Internal Buy-In for TPRM
The Policy Is Written. Nobody Is Following It. The TPRM policy is documented and approved. The process is posted on the intranet. Business units are still onboarding vendors…