AI Vendor Risk Assessment and Governance | SAFE
Approve AI Tools With Confidence

AI vendors need more than
a standard security questionnaire

Every AI tool your business adopts is a third party with access to your data. SAFE TPRM assesses AI vendors on the evidence behind their answers, finds AI tools that entered without review and keeps watching for model, data and security changes after approval.

The Problem

How AI vendor risk is handled today

  1. Standard questionnaires miss AI risk

    AI vendors are assessed with traditional security questionnaires that rarely cover models, training or data use.

  2. Data practices stay unclear

    Visibility into models, training practices, data usage, retention, permissions and subprocessors remains limited.

  3. AI arrives through existing vendors

    AI features added to SaaS tools you already use can bypass intake and assessment entirely.

  4. Approval is a one-time event

    AI vendors can change models, data practices, subprocessors or capabilities after approval without triggering a reassessment.

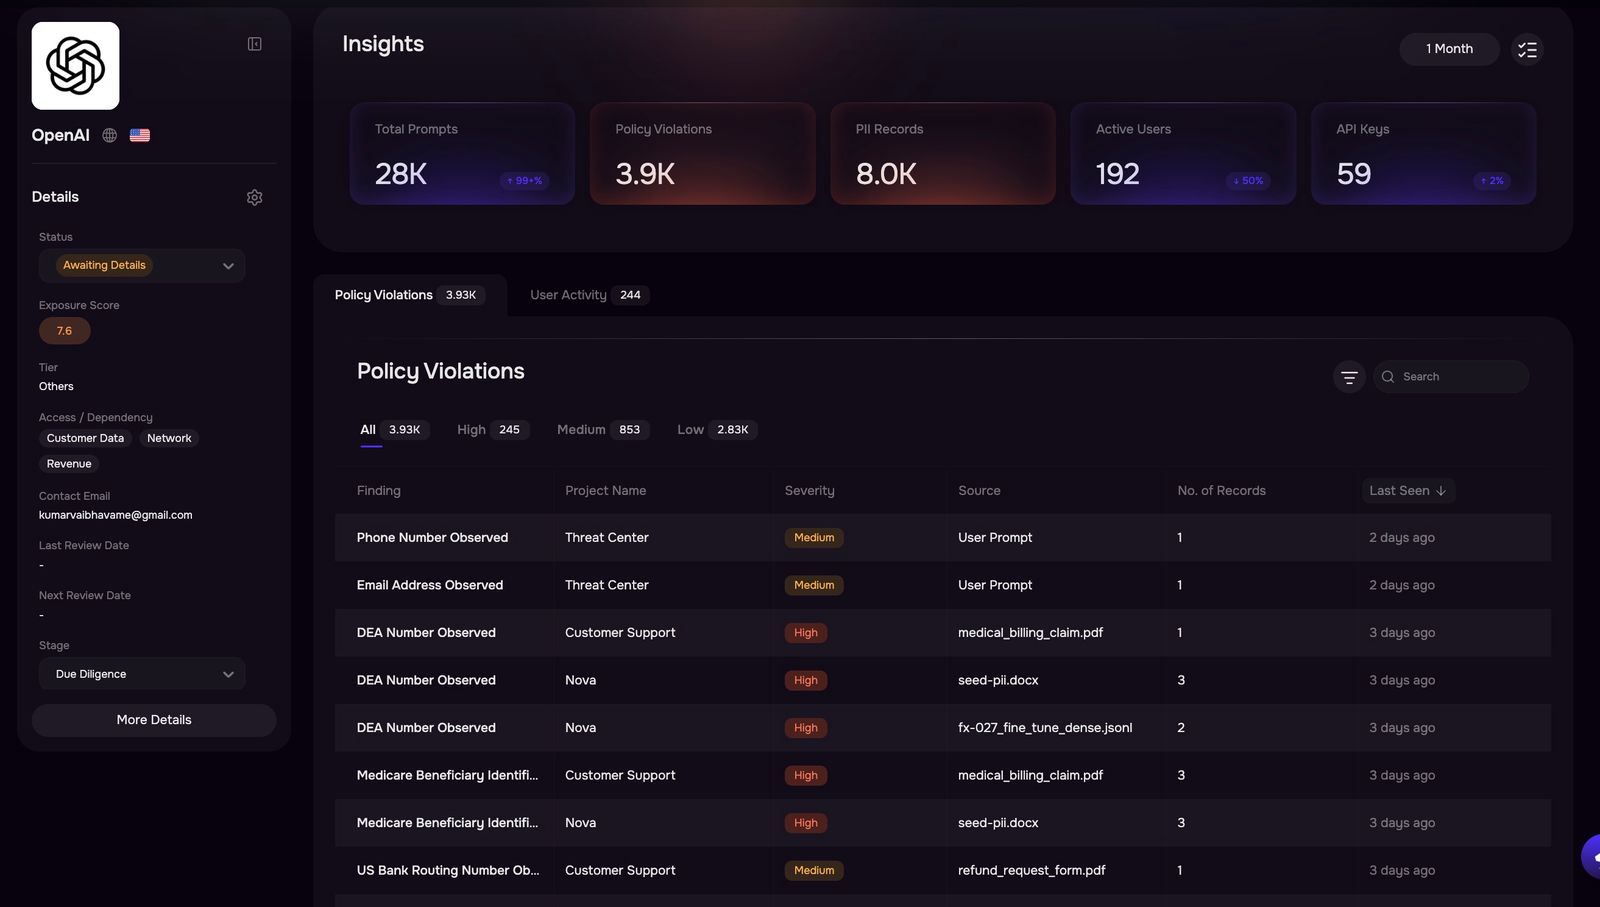
AI vendor assessment with document evidence mapped to controls

From a generic review to an evidence-backed AI vendor decision

When AI vendors get a generic review

  • Security cannot say with confidence whether an AI tool is safe to use.
  • Data usage, model, privacy and dependency risks go unidentified.
  • AI enters the organization without the right governance.
  • The original approval stops reflecting how the tool is used today.

When AI vendor risk is assessed on evidence

  • Security understands the material risks before an AI tool is approved.
  • More AI relationships enter the security and governance process.
  • Governance keeps pace as AI tools, models and data practices change after approval.
  • Better evidence lets security support broader AI adoption with confidence.
How SAFE Helps

Assess AI vendors like the third parties they are

Three capabilities in SAFE TPRM bring AI tools into the same evidence-based review, discovery and monitoring as every other vendor.

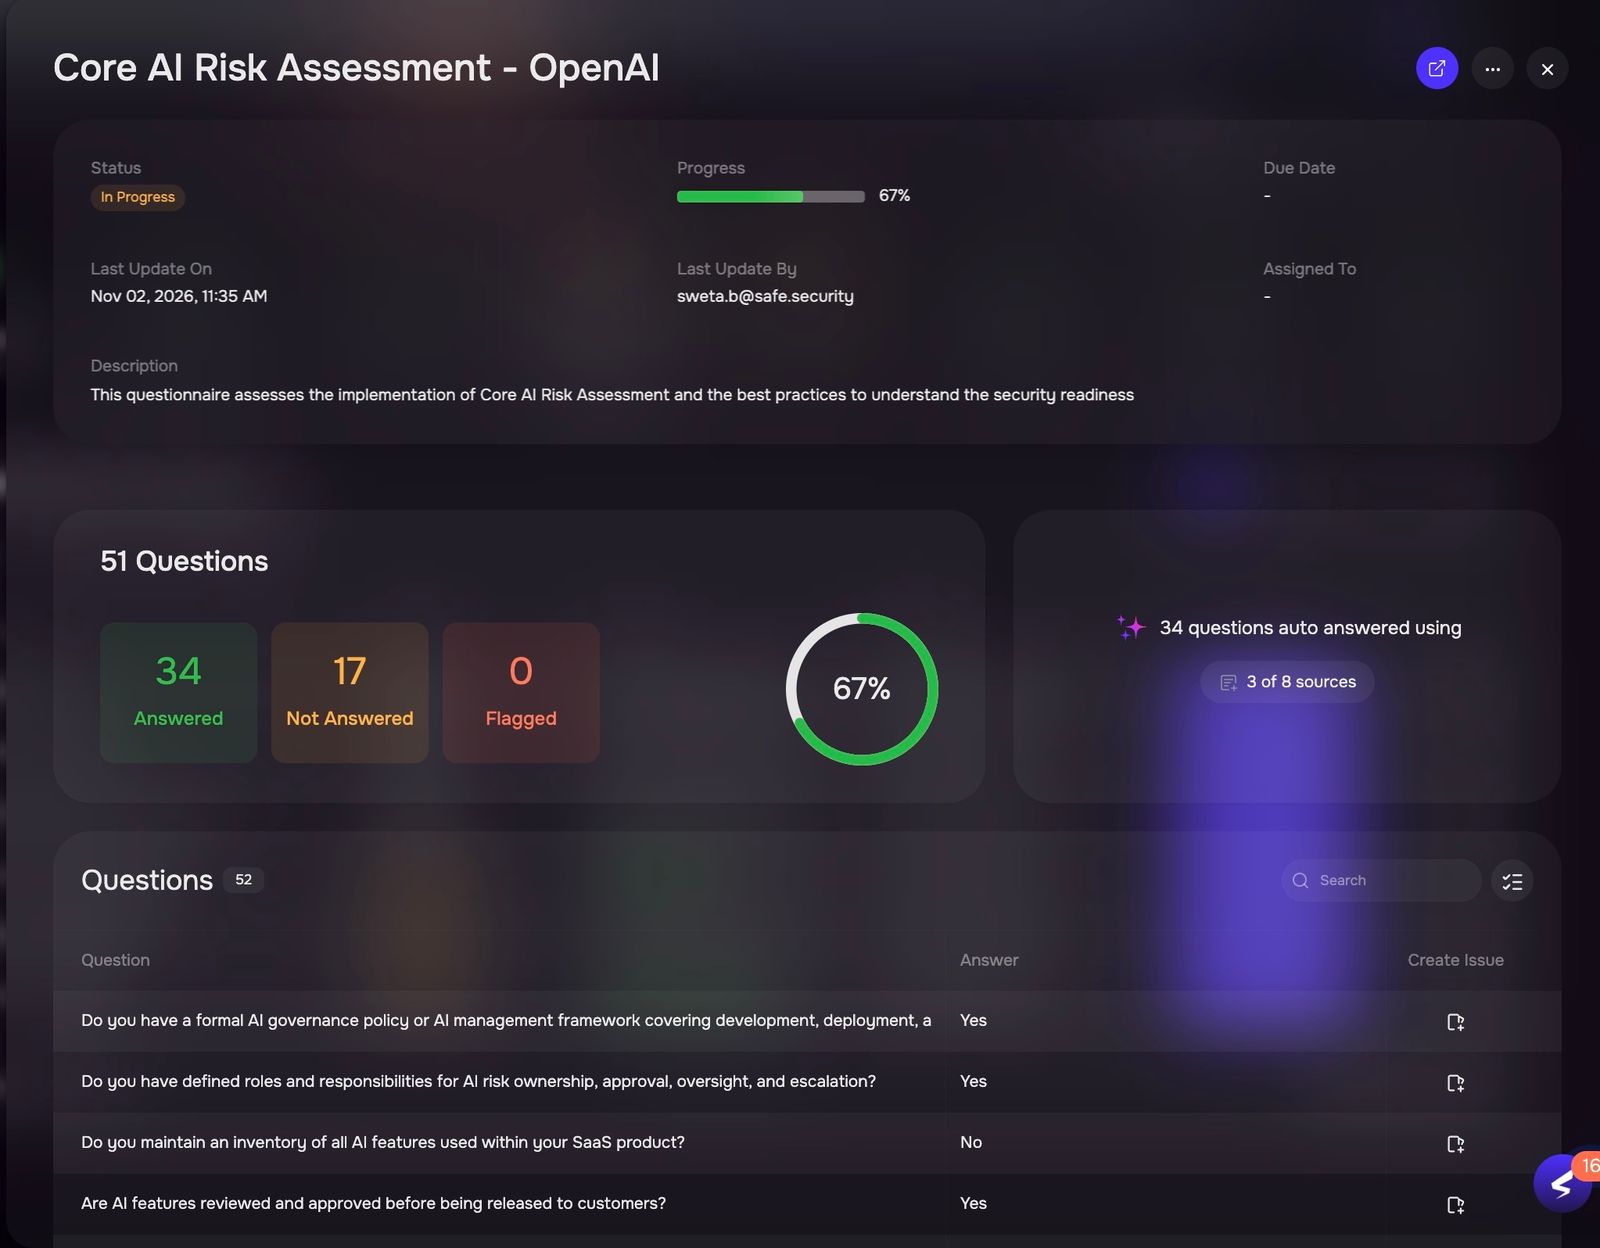
AI vendor questionnaire with AI review flags and linked policy evidence

Assess AI vendors against their own evidence

SAFE TPRM assesses AI vendors against their own evidence, with questionnaires scoped to how they will use models and your data.

  • SOC 2 reports, policies, AI-BOM and SBOM are read alongside the vendor's answers.
  • Model, training-data, data usage, retention, permission and subprocessor risks are assessed against AI governance standards.
  • AI flags inconsistencies and weak evidence while the vendor is still responding.
  • Gaps become findings for your analysts to review.
  • AI governance, data usage, ownership and model output terms are reviewed in contract risk and obligations.
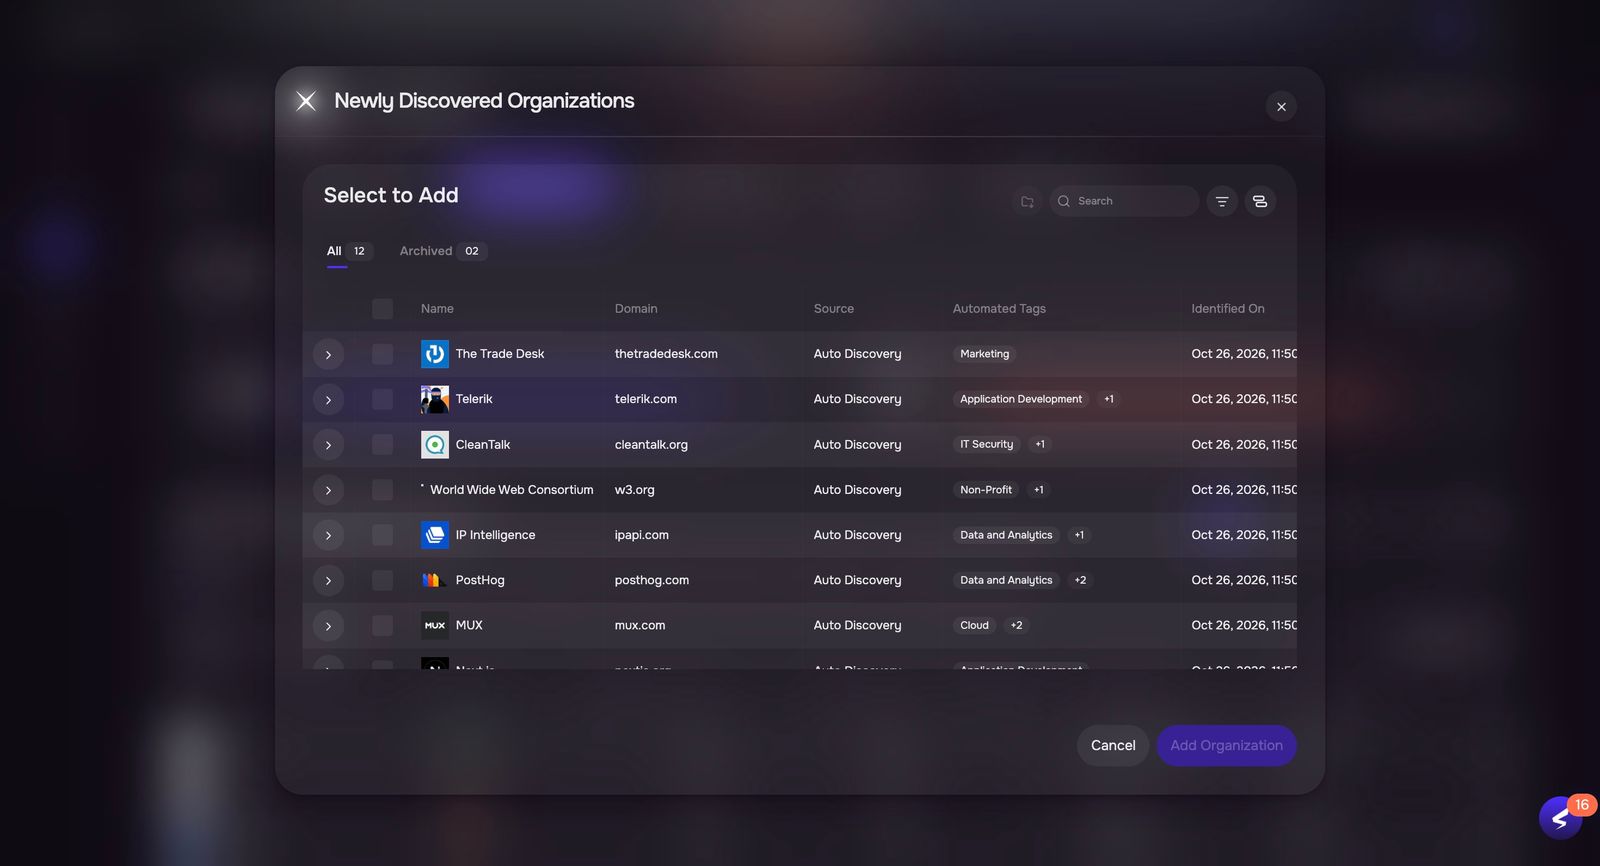
Newly Discovered queue on the inventory page with source and discovery reason

Find AI vendors that skipped the review

SAFE TPRM finds third parties, AI vendors included, that are in use but outside your managed inventory.

  • Discovery connects to systems such as ServiceNow, OneTrust and Ironclad, and to your identity provider's app catalog.
  • New AI usage inside vendors you already work with is identified too.
  • Each one lands in a discovery queue with its source and the reason it was found.
  • Your team routes it into intake for a risk-based assessment, or archives it if it needs no governance.
Explore shadow third-party discovery
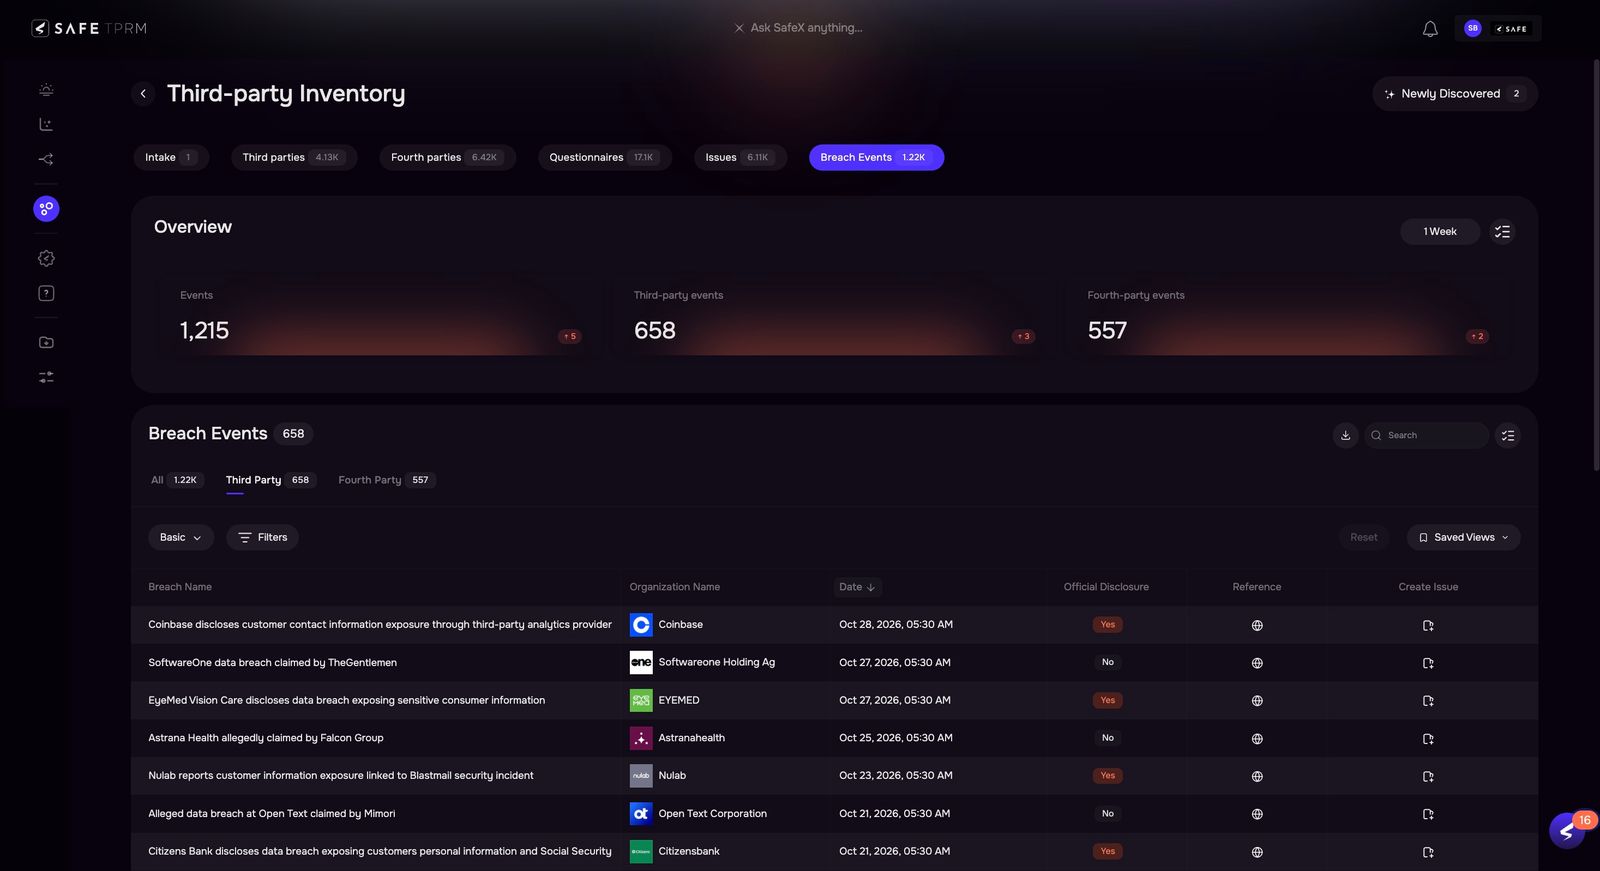
Breach event detail with affected third and fourth parties

Keep watching AI vendors after approval

SAFE TPRM detects material changes to an approved AI vendor and triggers a scoped reassessment or escalation.

  • Material changes include a new model, a change in data practices or a new subprocessor.
  • Breach intelligence, leaked credentials and public sources are monitored for incidents affecting your third and fourth parties.
  • When an approved AI vendor, or a provider it depends on, is breached, the right people are alerted.
  • Investigation, assessment and issue workflows can start from the event.
Explore breach detection and response
The Proof

Machine-Speed Defense. Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart's TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount
Book a demo

Ready to meet your AI Co-Workers?

Get a Demo