Fourth-Party and Concentration Risk | SAFE
Continuous Monitoring

Fourth-Party and
Concentration Risk

See who your vendors depend on, not only who you contract with. Discover fourth-party dependencies across 8,000+ fourth parties, score concentration where many vendors share one provider, and scope the impact when that provider is breached.

The Problem

Your vendors' vendors are part of your risk.

  1. Declared lists are incomplete

    Vendor-declared subcontractor lists are often partial or out of date, and rarely change when a vendor switches providers.

  2. Dependencies are hard to prove

    Without evidence behind a relationship, teams cannot tell a confirmed dependency from a guess.

  3. Shared providers stay hidden

    When many vendors rely on the same hosting, cloud or software provider, one failure can reach large parts of your business at once.

  4. Downstream breaches are slow to scope

    When a fourth party is breached, finding out which of your vendors depend on it is manual research.

How It Works

From hidden dependency to scoped impact

SAFE discovers fourth parties from external signals and vendor documents, shows the evidence behind each relationship, connects every fourth party to the third parties that depend on it, and keeps monitoring those dependencies as they change.

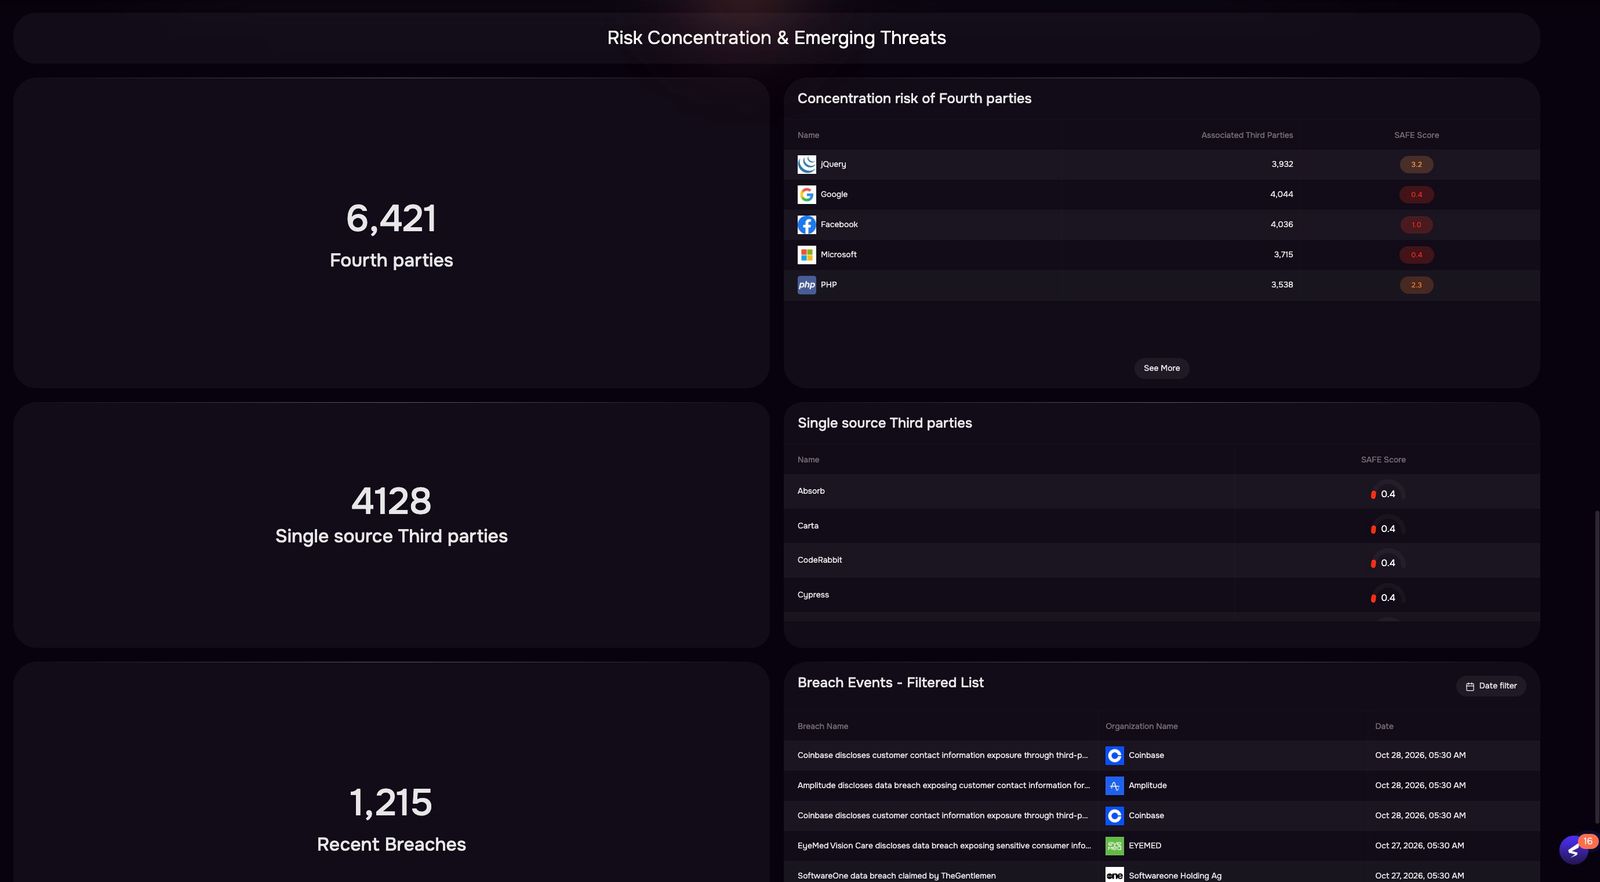
Portfolio concentration view with linked third-party counts and concentration scores

Discover fourth parties automatically

SAFE identifies downstream dependencies across a coverage base of 8,000+ fourth parties, without relying on vendor self-reporting.

  • Dependencies are discovered through outside-in analysis.
  • Subservice organizations are extracted from SOC reports, contracts and other vendor documents, linked to the source page.
  • Analysts can add a known fourth party manually when they learn about it another way.
  • Every newly discovered fourth party is risk assessed automatically, so new dependencies arrive with context.
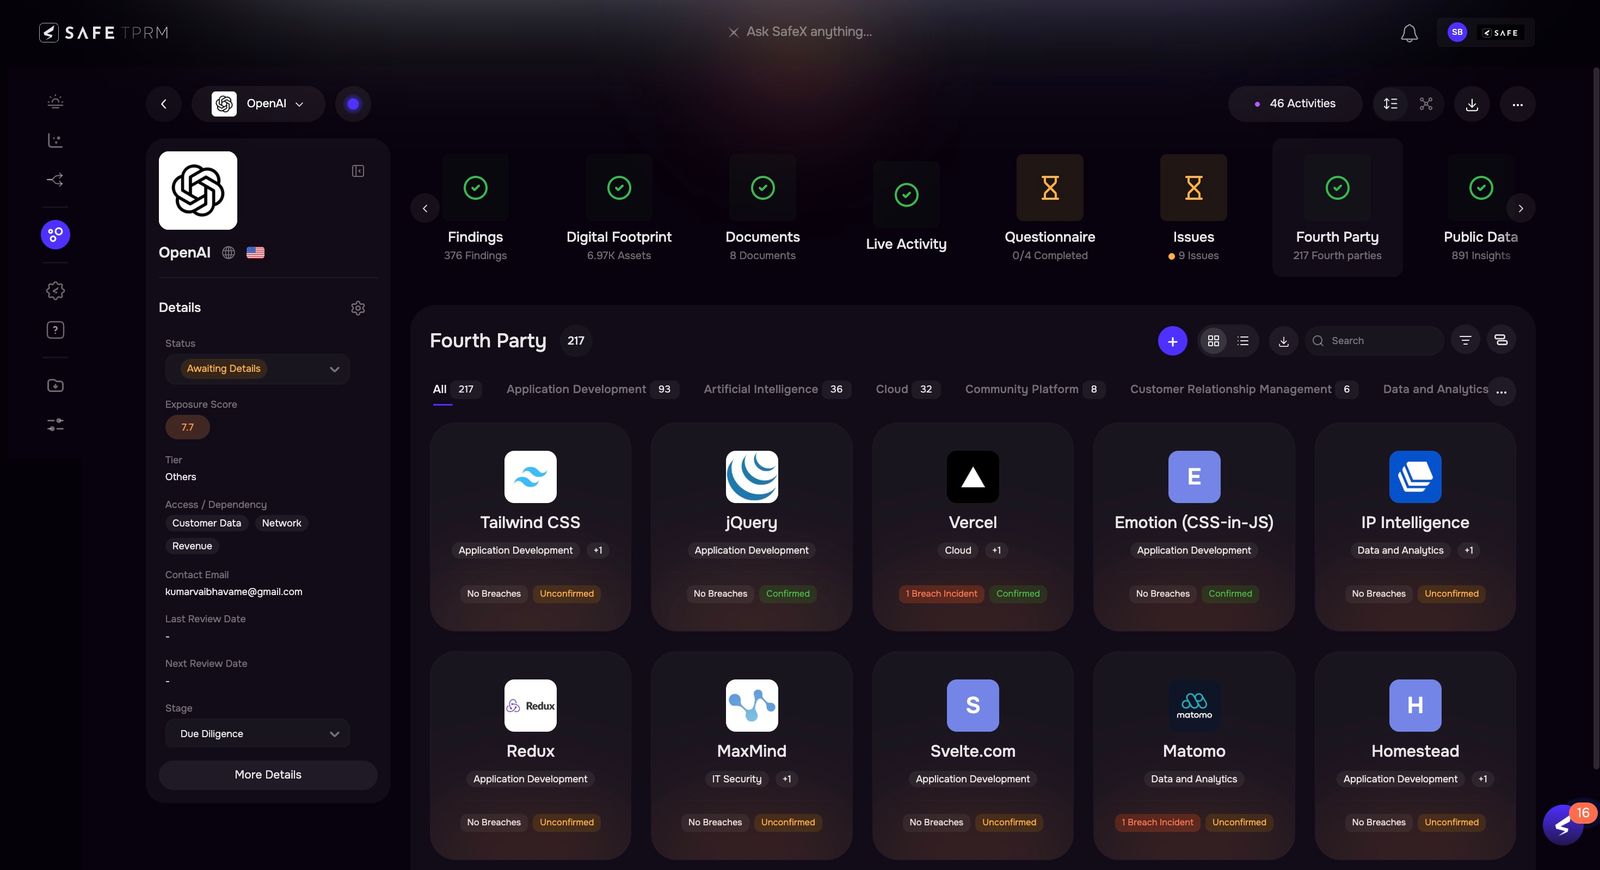
Fourth parties discovered for a vendor, with detection source

See the evidence behind every relationship

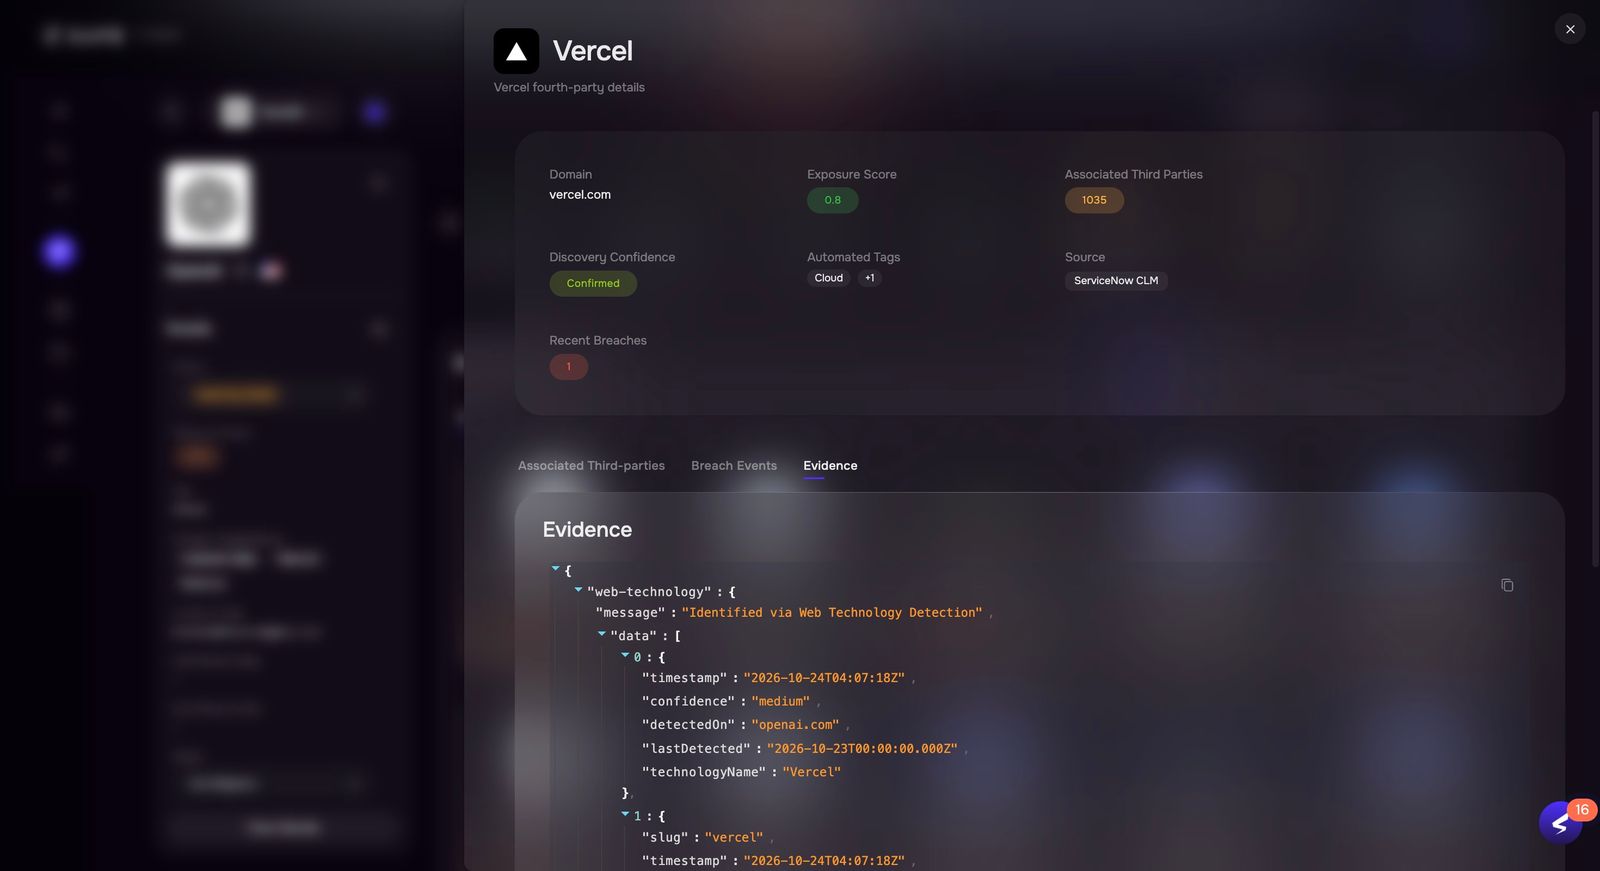
Each fourth-party connection shows its category, the supporting signals and a confidence level.

  • Confirmed relationships are separated from potential ones.
  • Your team can explain any dependency when leadership or an auditor asks how it was found.
  • Fourth parties are monitored continuously, so exposure stays current between reviews.
Fourth-party detail with category, confidence and evidence

Score concentration across your portfolio

SAFE connects each fourth party to every third party that relies on it and scores concentration across your portfolio.

  • Concentration insights show where critical vendors rely on the same suppliers or regions.
  • The linked third-party count shows where a single provider supports many of your relationships.
  • When concentration crosses your risk appetite, SAFE escalates it to the right risk owner.
  • Ask which providers sit behind your critical services and get a concentration brief with business impact.
  • Filters, widgets and exports let teams review dependencies by third party or by provider.
Affected third parties linked to a breached fourth party

Scope the blast radius of a fourth-party breach

When a fourth party is breached, SAFE identifies the third parties that depend on it, so you can scope downstream impact quickly.

  • Prepare impact and continuity briefs for the critical services involved.
  • Fourth-party breach events appear in breach notification email alongside third-party events.
  • The list of affected vendors can be exported for follow-up.
  • Breach events come from breach detection and response, and alerts reach owners through risk-based escalation.
  • Fourth-party visibility is part of continuous monitoring, alongside external exposure monitoring.
Why SAFE

Fourth-party visibility built on evidence

Discovered from signals

Fourth-party dependencies are identified passively from external signals, so you are not limited to incomplete or outdated vendor-declared lists.

Evidence behind every relationship

The signals and confidence level for each connection make every discovered dependency explainable and defensible.

Concentration before incidents

Concentration scoring and portfolio insights show where a single provider could create systemic exposure across your business.

Breach blast radius at a glance

See which third parties depend on a breached fourth party and scope potential downstream impact.

The Proof

Machine-Speed Defense. Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart's TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount
Book a demo

Ready to meet your AI Co-Workers?

Get a Demo