Blog
 Threat Research
No Credentials Required: How the Most Dangerous New CVEs Invite Themselves into Your Systems
Vulnerabilities in Windows LNK, Adobe Acrobat, Android Framework and more are actively exploited. By SAFE Threat Research Team This week’s trending vulnerabilities span phishing campaigns targeting national infrastructure,…
 TPRM
The 400-Question Trap: How to Build a Defensible TPRM Posture in the Age of Vendor Breaches
Your detailed questionnaire may create a paper trail for a negligence claim By Grant Rexer and Jacqueline Lebo Let’s talk about the elephant in the TPRM room: You…
 TPRM
SAFE TPRM Now Available on AWS Marketplace
Get fast time to value: Modernize vendor management with one click for the first fully autonomous TPRM solution By Jen Dawson Vendor sprawl, AI risk, sharper regulatory pressure…
 Events
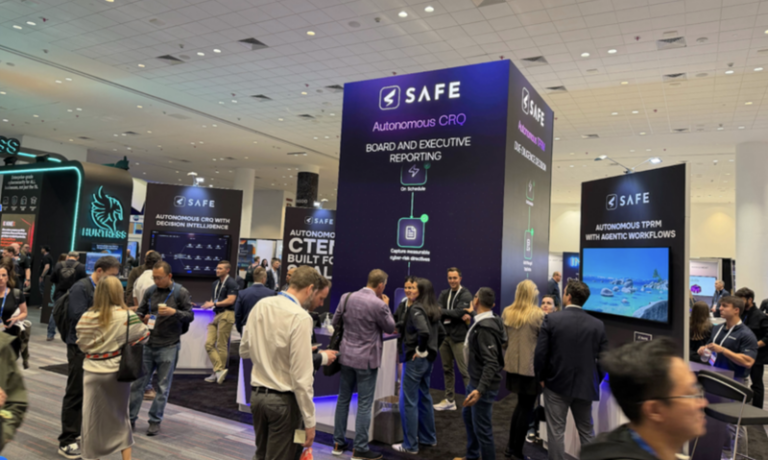
RSAC 2026 Takeaways: The End of Dashboards, the Start of Decisions
By Resha Chheda Another RSAC done, and like every year, there was a lot of noise, big claims, and booths trying to say something slightly different but mostly…
 Threat Research
Latest Critical CVEs Signal a Shift in Attacker Strategy: Go for Full System Control
Compromise software supply chains, exploit internet-facing apps, chain vulnerabilities By SAFE Threat Research Team This week’s vulnerabilities reinforce a clear shift in attacker strategy: compromise the software supply…
 Threat Research
Six Critical CVE Clusters Security Teams Should Be Watching This Week (Mar 23)
Recognize the attack patterns shaping today’s threat landscape By SAFE Threat Research Team This week’s vulnerabilities highlight a consistent and concerning pattern: unauthenticated access, internet-facing systems, and active…
 TPRM
A New Training Guide for a TPRM Analyst
Don’t let AI define you – write your next job description By Jeff Copeland A while ago, we introduced you to The Painful Reality of a TPRM Analyst:…
 CTEM
CTEM: Coming of Age in the Age of AI
Solving the “unsolvable” – it’s been a journey. Author Chris Griffith is VP-Product for SAFE and a veteran of CTEM development. The $10 Million Blind Spot Picture this:…
 Threat Research
Critical CVE Clusters Security Teams Should Be Watching Now
Recognize the attack patterns shaping today’s threat landscape By SAFE Threat Research Team In the past few days, several high-impact vulnerabilities have emerged across enterprise infrastructure, browsers, mobile…
 Podcasts
The Cyber Risk Podcast: Third-Party Risk Management Goes Agentic in 2026
Vincent Scales of CVS Health discusses the breaking point, the industry shift, and the agentic horizon for TPRM By Sweta Bhattacharya n this episode of The Cyber Risk…
 Trends
Is Artificial Intelligence About to Commoditize Cybersecurity Software?
By Saket Modi, CEO, SAFE The debate just hit a boiling point. Recent demonstrations of Claude discovering hundreds of vulnerabilities in audited open-source code – combined with research…
 Trends
The Coming 5x Transition for CISOs – John Chambers, Saket Modi Recap
Watch on demand their fireside chat forecasting 2026, the year AI disrupts cybersecurity By Jeff Copeland In a recent fireside chat between John Chambers and Saket Modi, the…