Vendor Assessment Coverage at Scale | SAFE
Reduce Third-Party Breach Exposure

Only the top tier
gets a real vendor review

Most programs can assess a fraction of their vendors in depth. The rest get a light review, or none, while the vendor list keeps growing. SAFE TPRM gives every vendor the right level of oversight and saves analyst time for the exceptions that need judgment.

The Problem

What limited assessment coverage looks like today

  1. A subset gets the full review

    Only part of the vendor population receives a comprehensive annual assessment.

  2. Capacity sets the scope

    Analyst hours and manual effort decide how many vendors get assessed.

  3. Lower tiers go unwatched

    Lower-tier vendors get a brief review and little ongoing security monitoring.

  4. The vendor list outgrows the team

    New vendors arrive faster than the TPRM team can assess them.

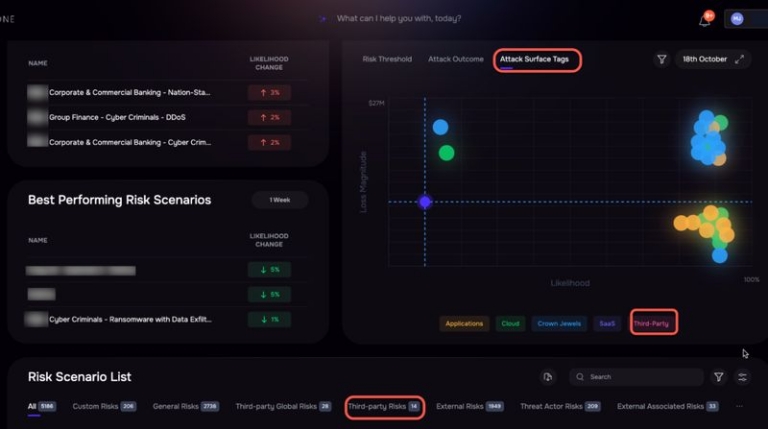
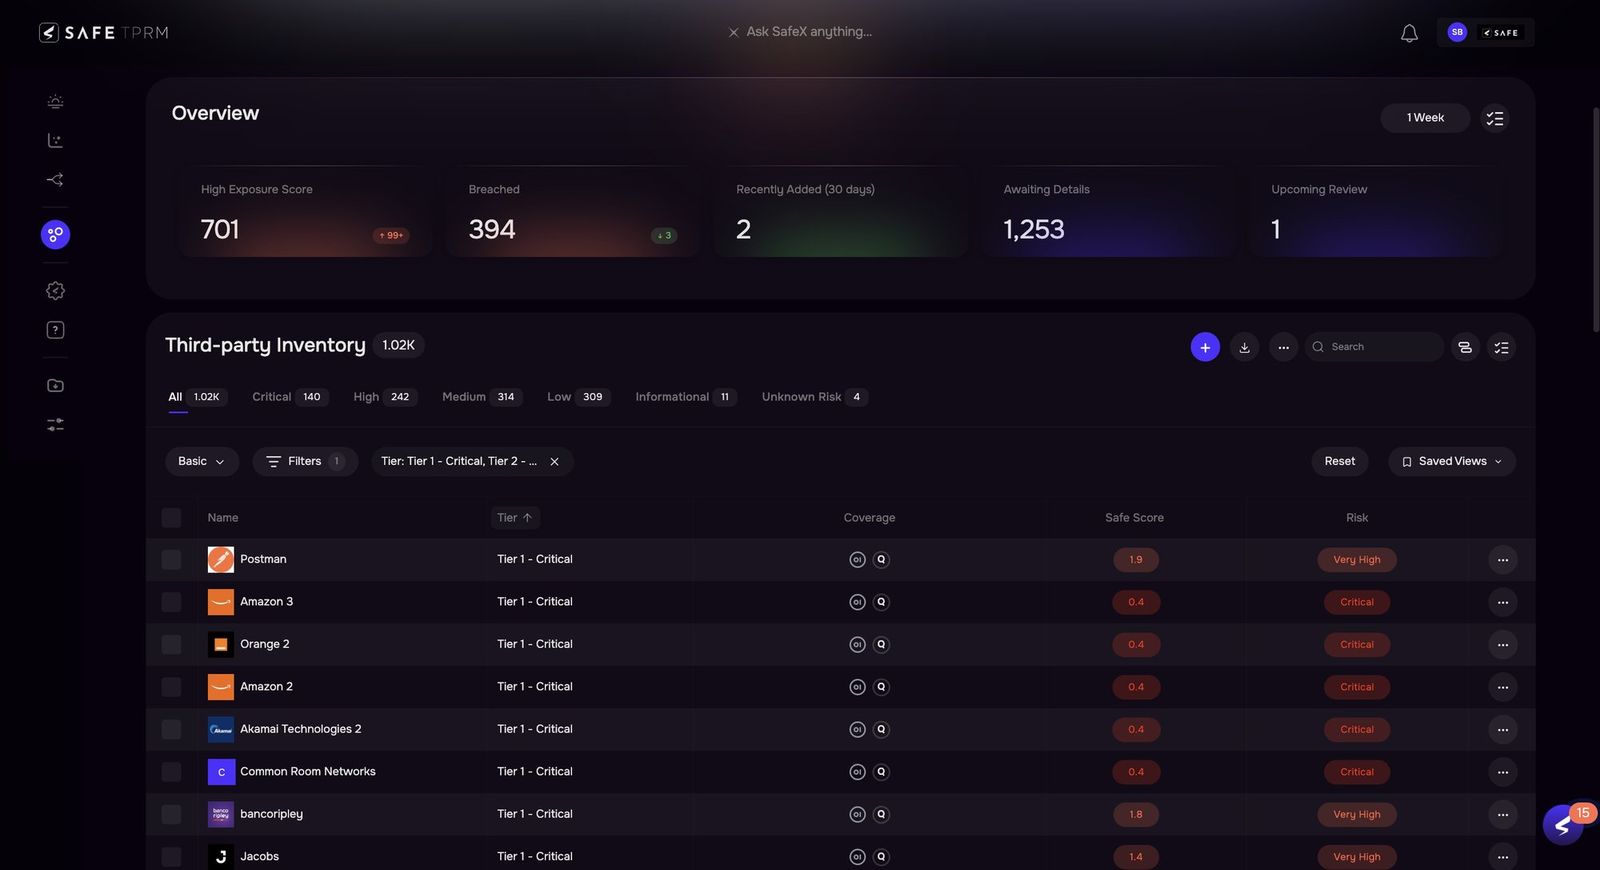
Third-party inventory in SAFE TPRM showing vendors by tier, coverage and risk

From a reviewed few to a covered portfolio

When coverage depends on headcount

  • Large parts of your third-party exposure stay unknown.
  • Lower-tier vendors can still create serious cyber exposure, and it goes unnoticed.
  • Each new vendor adds risk faster than the team can assess it.
  • Leadership sees only the exposure from vendors that were actively assessed.

When every vendor gets the right level of oversight

  • Visibility extends consistently across the whole vendor ecosystem.
  • Material risks surface whatever tier a vendor started in.
  • Analysts spend their time on vendors that need deeper human judgment.
  • Vendor growth stops adding unmanaged exposure at the same rate.
How SAFE Helps

Coverage that scales with your vendor list

Seven capabilities take on the evidence review, vendor follow-up and routing work that usually limits how many vendors a team can cover. Assessment depth follows each vendor's criticality and observed risk.

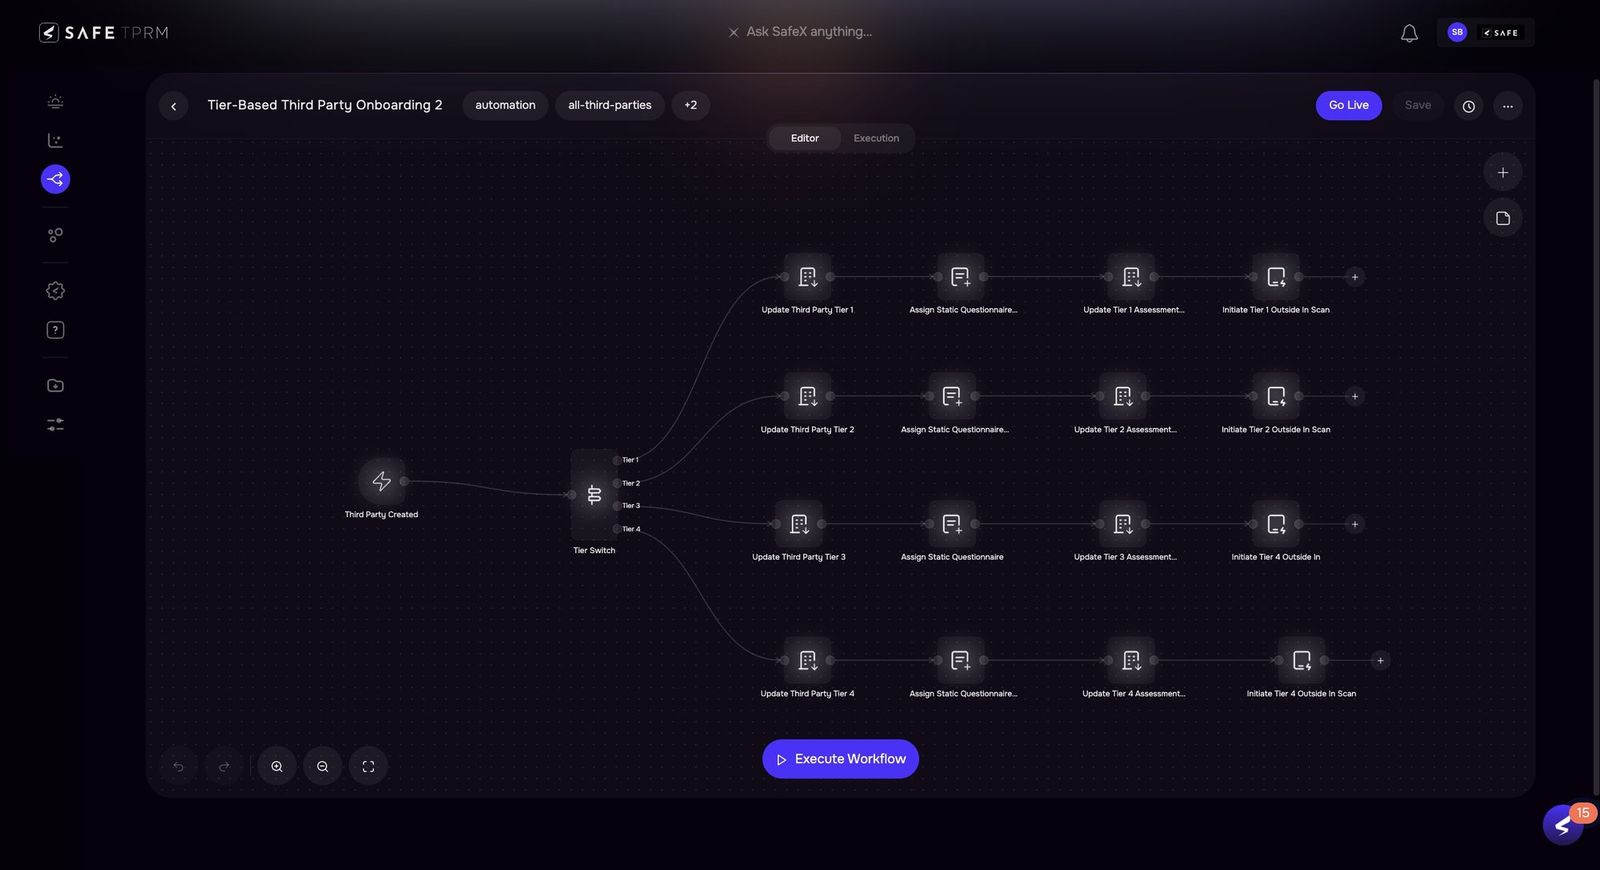
Tier-based onboarding workflow in the SAFE TPRM no-code workflow builder

Run every vendor through the right workflow

A no-code builder lets you configure intake, tiering, assessment, review, issue and reassessment workflows that mirror your own policies.

  • Triggers can be event-based, scheduled or manual.
  • AI steps assess questionnaires, summarize evidence and review responses.
  • Pre-built templates, such as smart tiering and questionnaire assignment, get common workflows running quickly.
  • Human checkpoints sit wherever your program requires an approval.
  • Execution insights show runs, actions completed, success rate and time saved, so you can see how much manual effort automation removes.
Explore agentic workflows
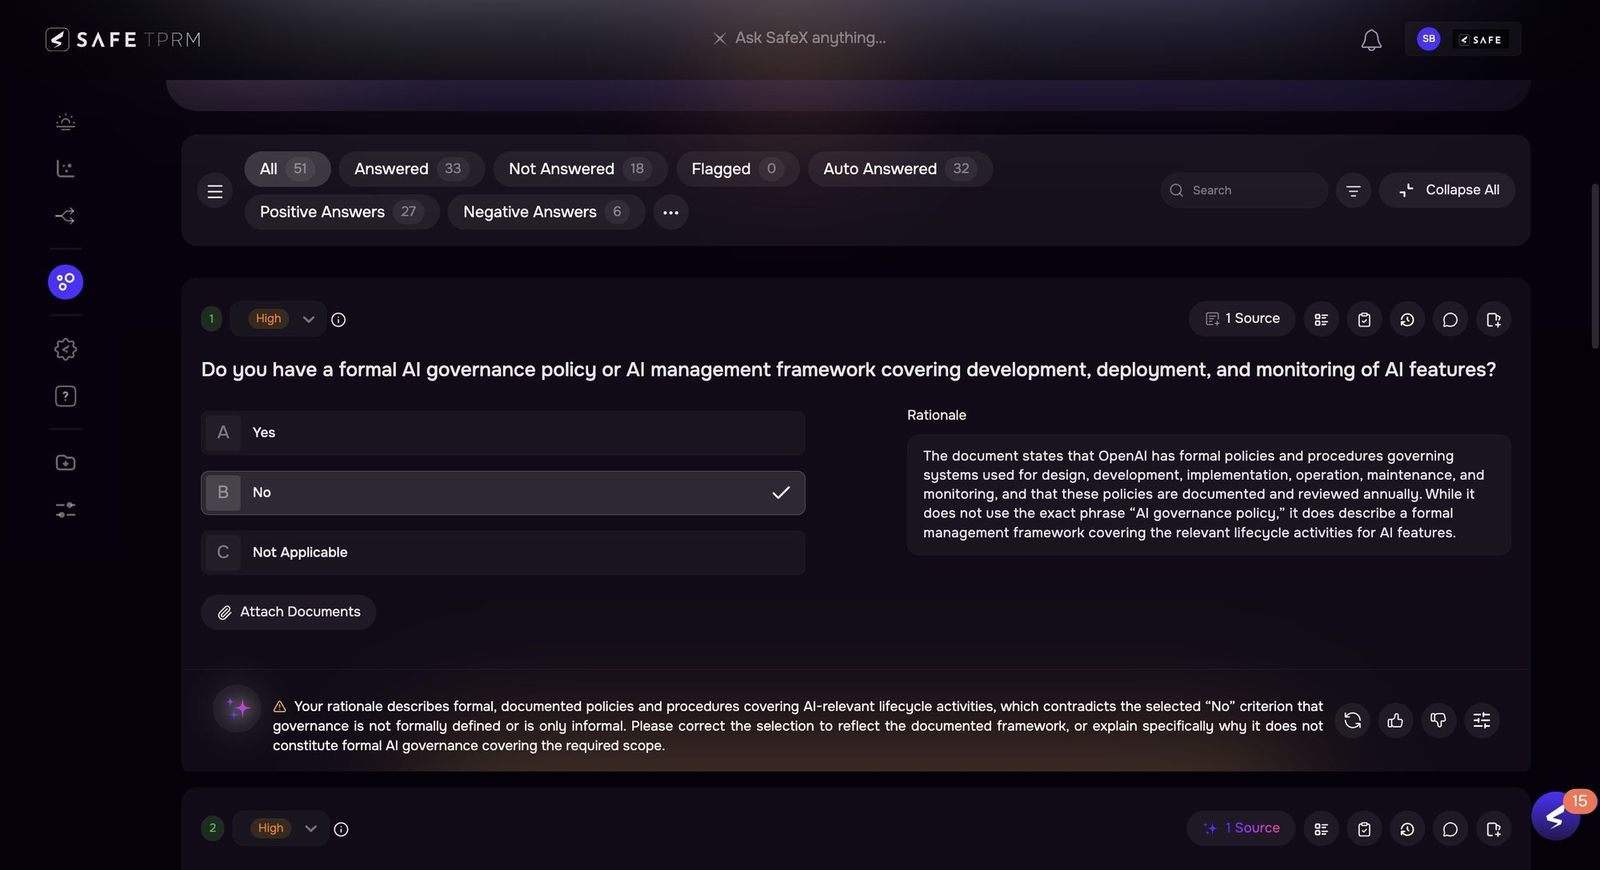
AI review flagging a vendor questionnaire answer that conflicts with its rationale

Let AI do the first review of vendor evidence

SAFE reviews questionnaires, SOC 2 reports, certificates, policies and penetration tests as they arrive.

  • Evidence is mapped to controls, with gaps, inconsistencies and weak evidence flagged.
  • Analysts open an assessment that has already been reviewed.
  • Control-level findings link to the source document.
  • Analysts spend their time on the questions that need judgment.
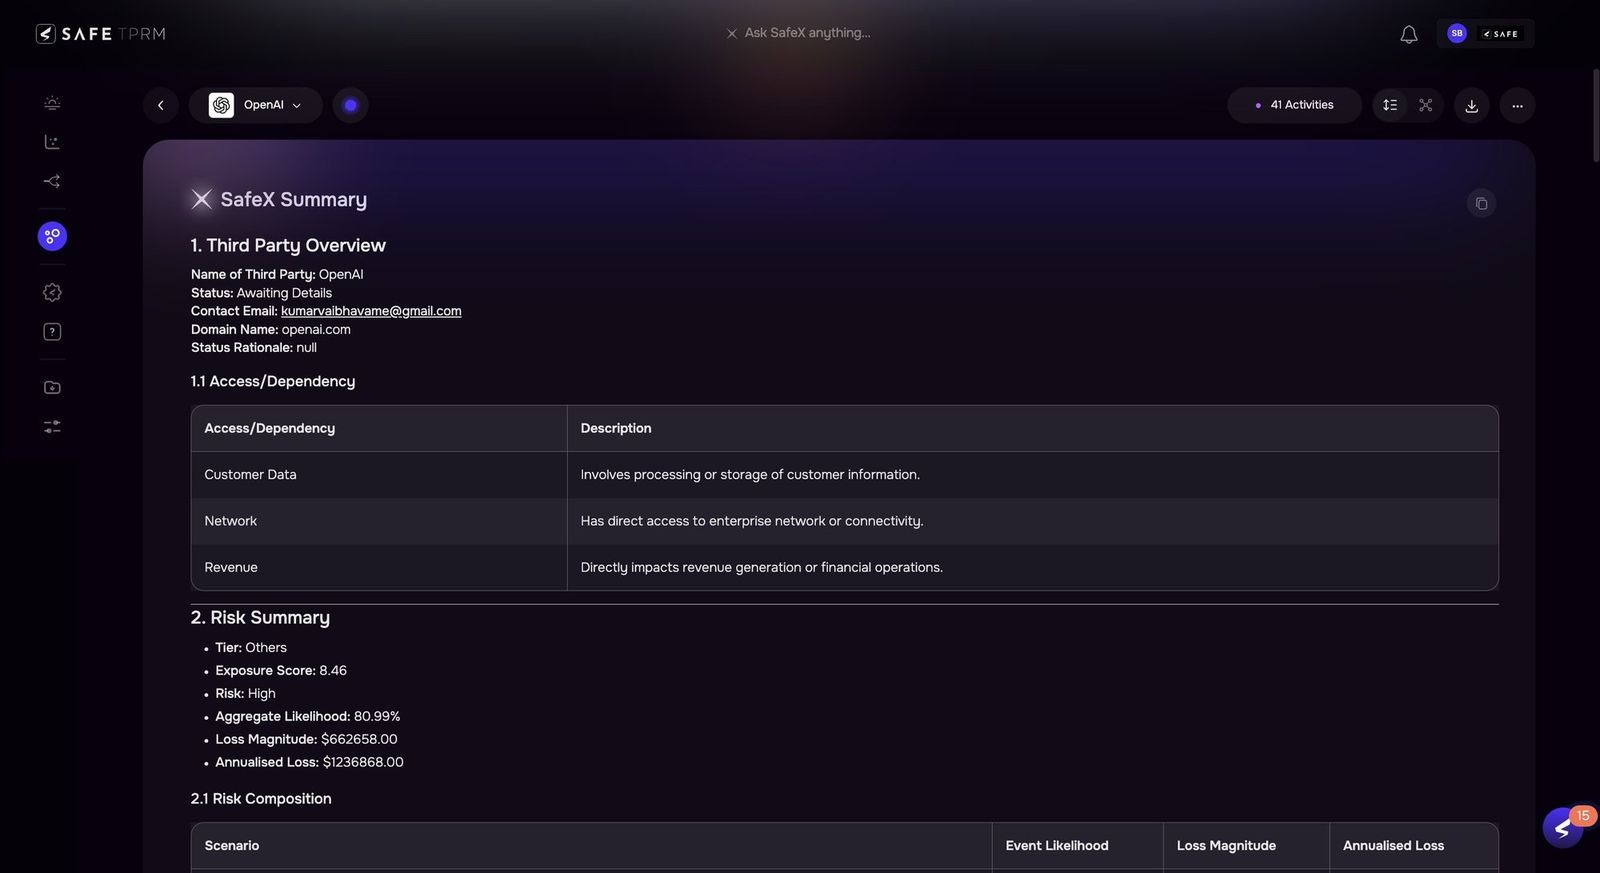
SafeX summary of a third party with access, risk and loss exposure

Know which vendors need a person

AI brings together each vendor's assessments, findings, documents and external exposure, and explains what drives its risk.

  • AI recommends the next step, with its evidence.
  • Recommendations wait for analyst approval.
  • Material decisions stay with your team while routine vendors keep moving.
Explore AI risk decisioning
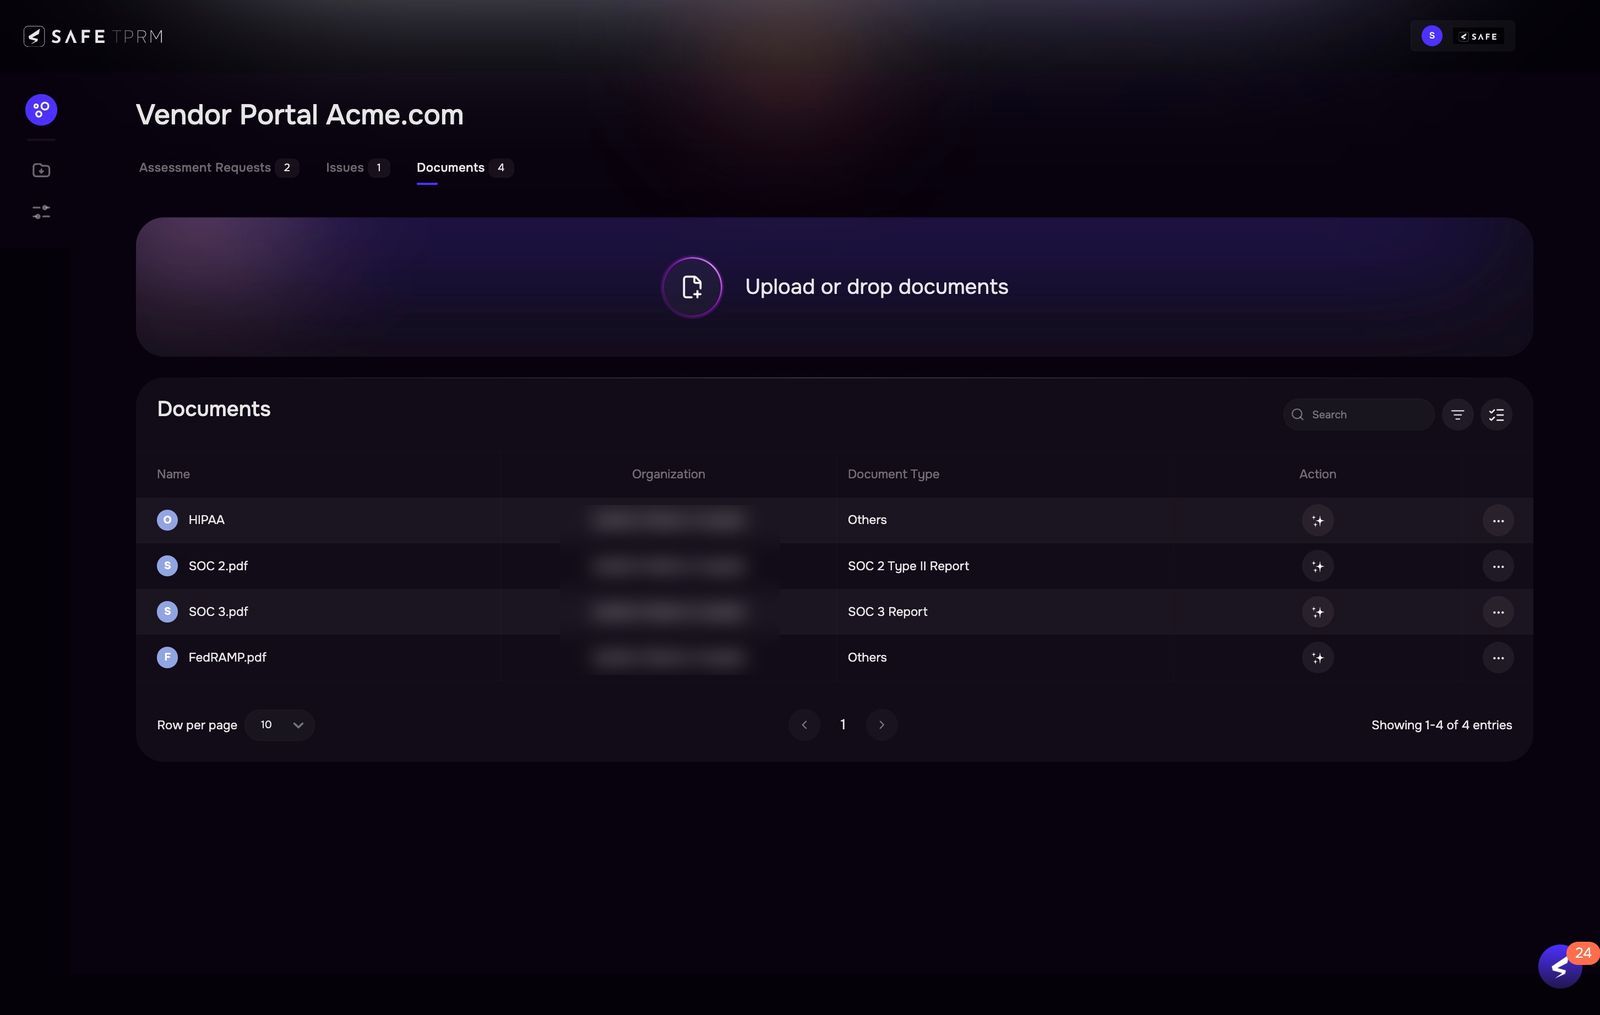
SAFE TPRM vendor portal where third parties answer requests without creating an account

Give vendors a portal that needs no account

Vendors open assessments, evidence requests and issues through passcode-protected links, with no account to create.

  • Several people at the vendor can collaborate, delegate questions and save progress.
  • Documents upload to one secure place.
  • Earlier responses and evidence can be reused at reassessment.
  • Less back-and-forth means each analyst can cover more vendors.
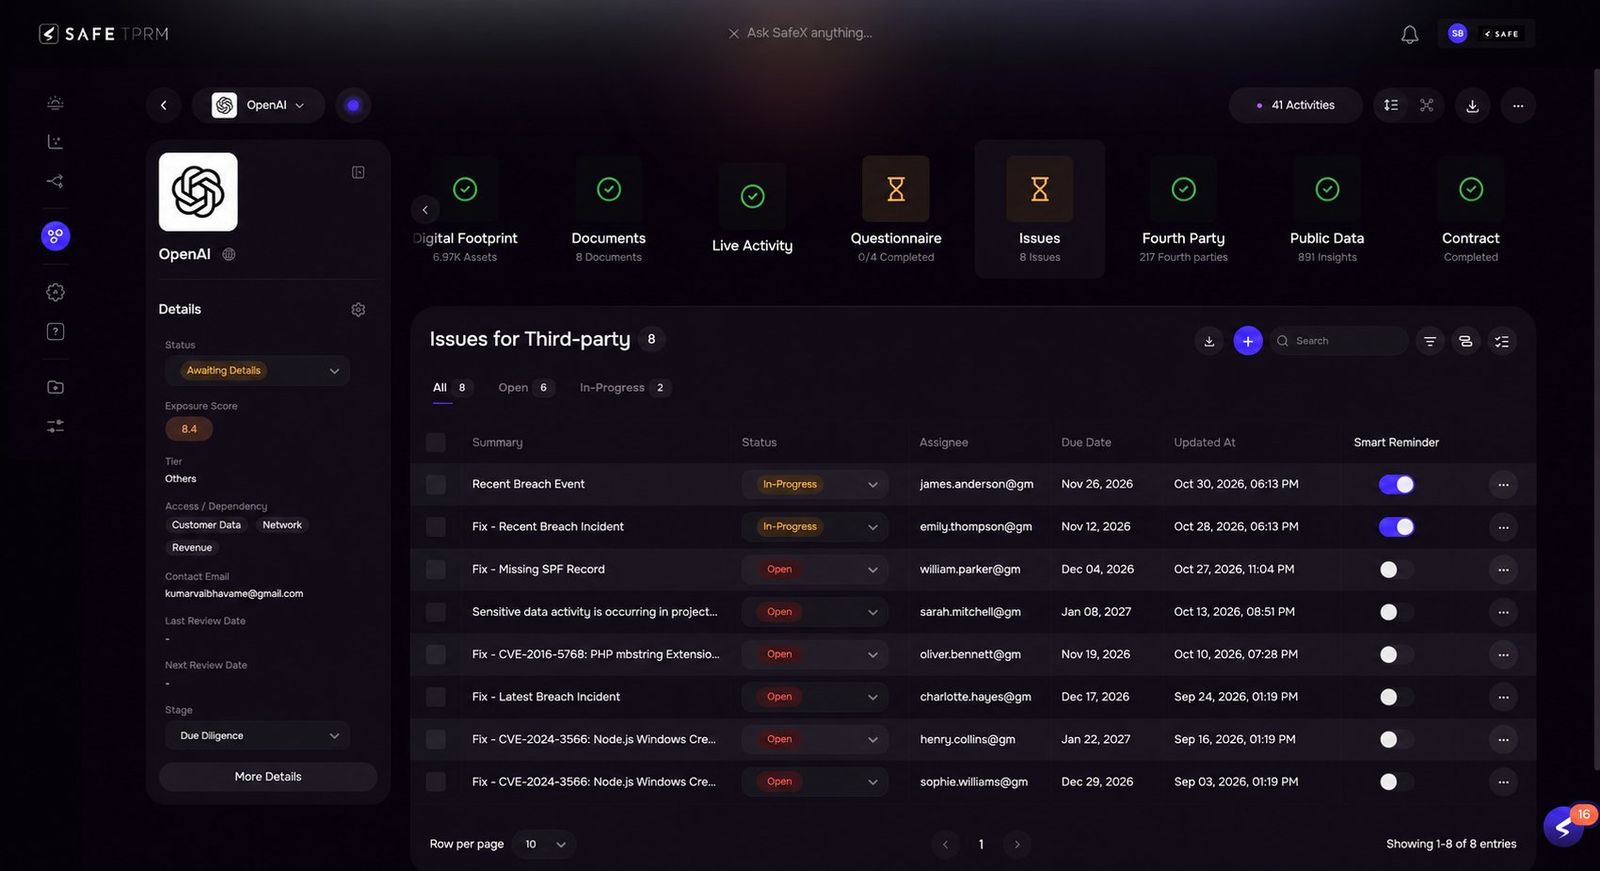
Third-party issues with owners, due dates and smart reminders

Turn findings into tracked issues automatically

Questionnaire gaps, external exposures, assessment findings and AI-identified risks become issues individually, in bulk or automatically.

  • Each issue gets an owner, a due date and automated reminders.
  • Related findings can be grouped into one remediation action.
  • Follow-up across a large portfolio does not depend on one analyst's inbox.
  • Each outside-in finding type is listed across all vendors, so a shared weakness is handled once.
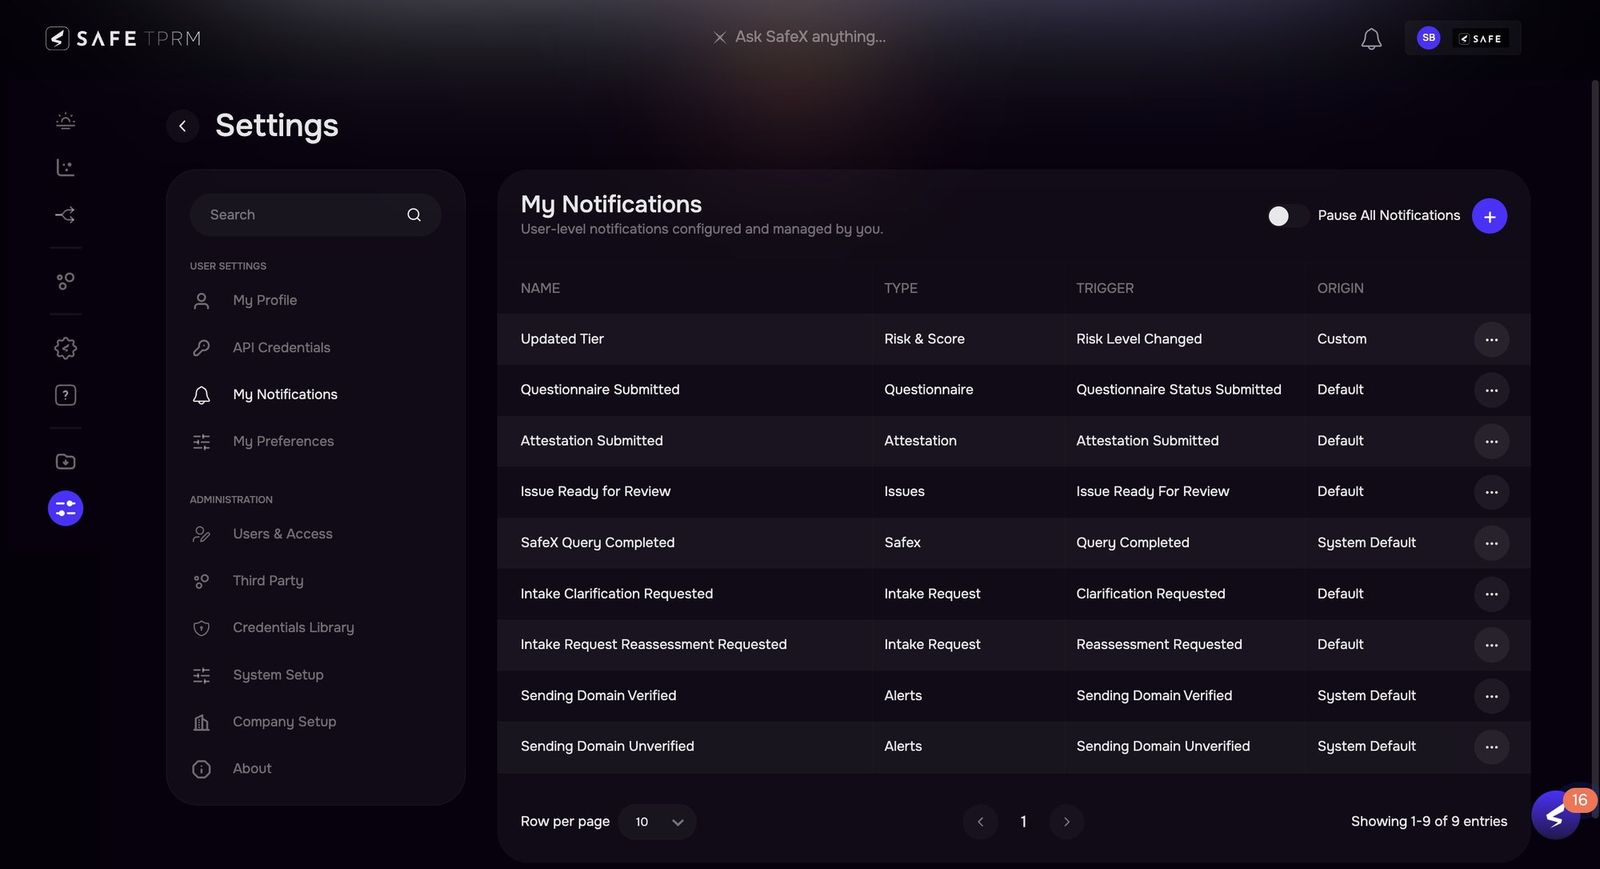
Notification rules by trigger and type in SAFE TPRM settings

Bring only material changes to an analyst

Rules based on vendor tier, score changes, breach events, findings and assessment results decide what needs attention and who acts.

  • SAFE starts the matching response, from an issue to a reassessment.
  • Lower-priority updates can arrive as scheduled digests.
  • Notifications can be scoped to a group, user or role.
  • Delivery options include email, in-platform, mobile push, Slack and Teams.
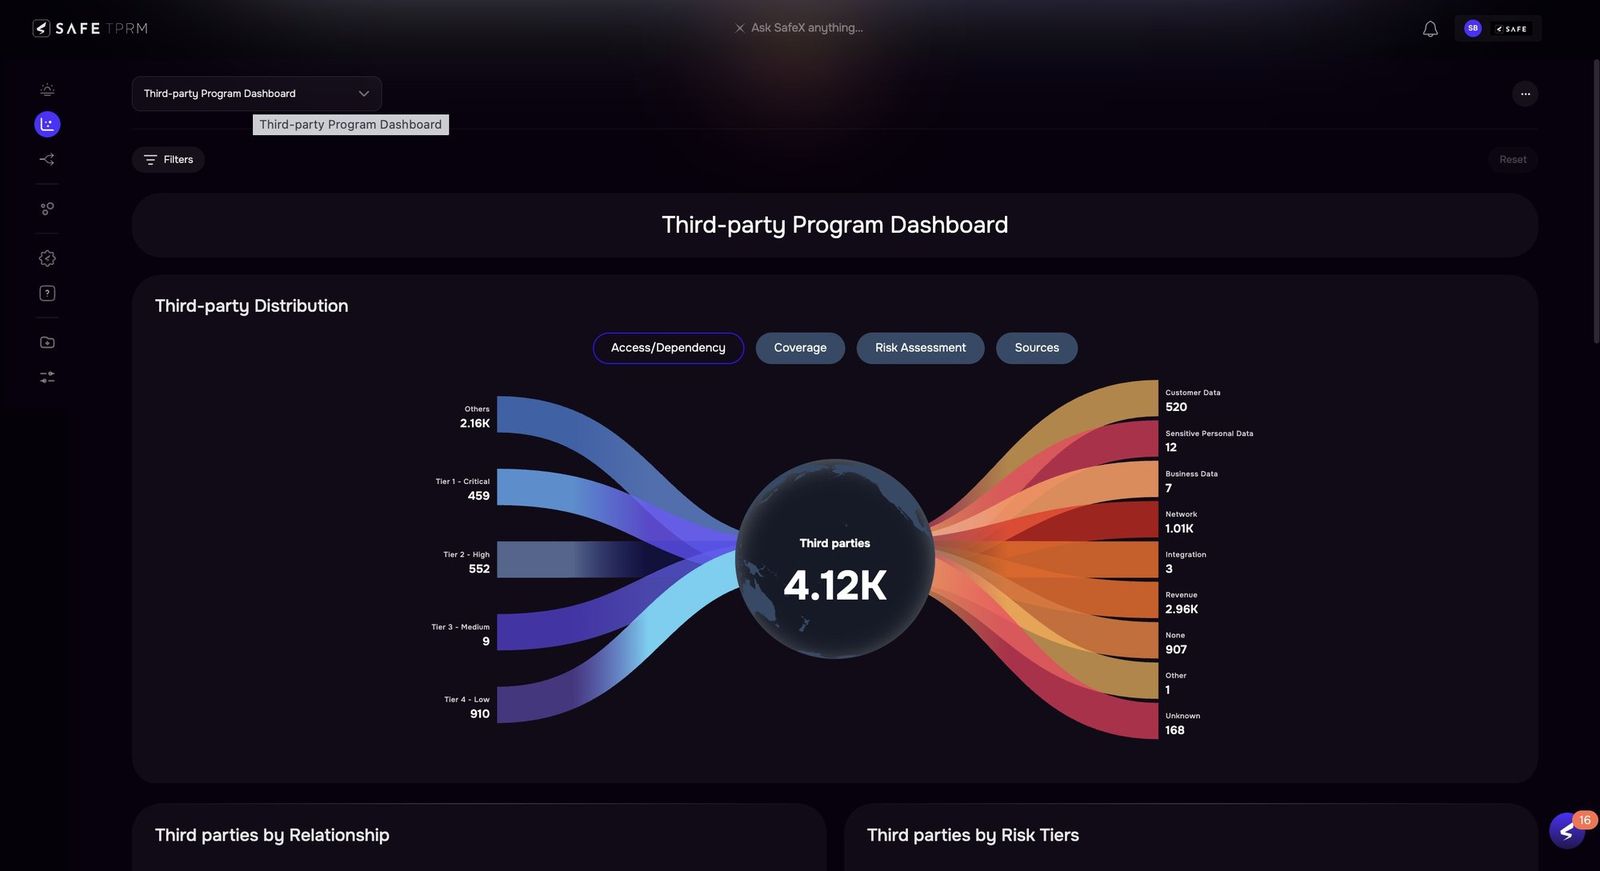
Third-party program dashboard showing distribution by tier, access and data

Show coverage across the whole portfolio

Dashboards show third-party risk, exposure and program metrics by tier, business unit or any custom field.

  • Dashboards point to the vendors that need attention.
  • Leaders drill from any metric into the vendors and evidence behind it.
  • Full vendor data exports support board and audit reporting.
  • Scheduled AI portfolio summaries reach stakeholders without anyone building a report.
Explore dashboards and reporting
The Proof

Machine-Speed Defense. Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart's TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount
Book a demo

Ready to meet your AI Co-Workers?

Get a Demo