Banking & Financial Services: Cyber Risk Management Solution - Safe Security

SAFE One for Financial Services

Managing cyber risk to keep money, markets, and customers safe

The Paradox

Business Challenges

  1. Open banking APIs, cloud-native applications, and rapid SaaS integrations accelerate innovation but introduce risks

  2. Disruptions across payment processors, core banking vendors, SaaS platforms leads to customer impact & financial loss

  3. NYDFS, FFIEC, OCC, FDIC, SEC– all demand timely, defensible evidence of incident response readiness & material impact

  4. Thousands of external partners, yet little real-time visibility into vendor posture, emerging threats, or critical dependencies

  5. Risk leaders must defend budgets and prove ROI, often without the quantitative insights needed to make investment decisions

The Solution

Solution Highlights

Securing financial services so trust and operations never break

Quantitative Risk Analysis, SAFE One Platform

Know, understand, and communicate cyber risk in real time

Get continuous risk visibility across core banking systems, fintech partners, cloud providers, & vendors

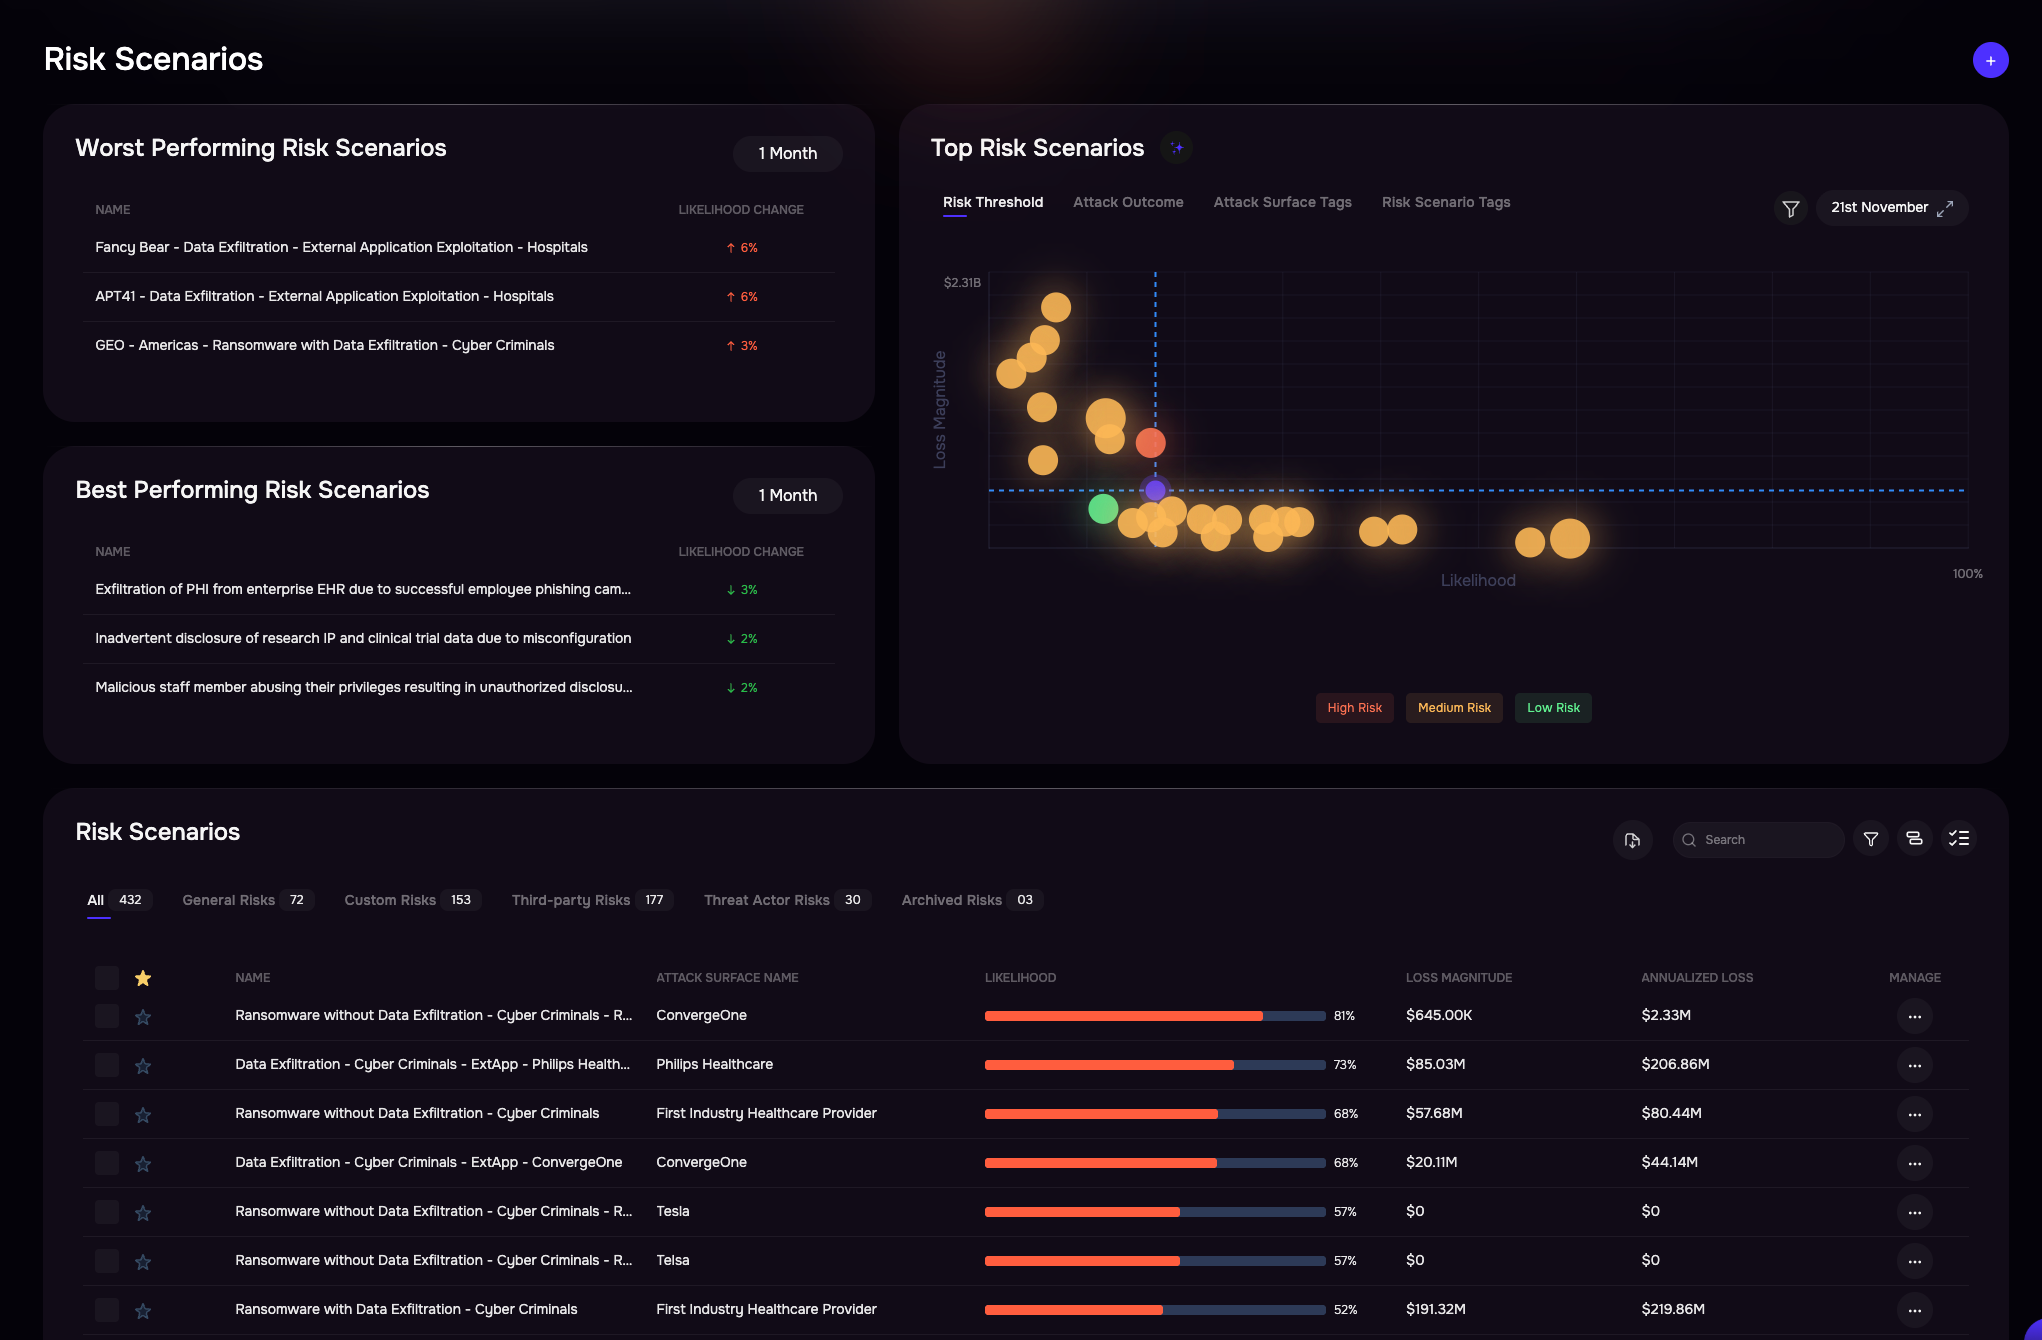
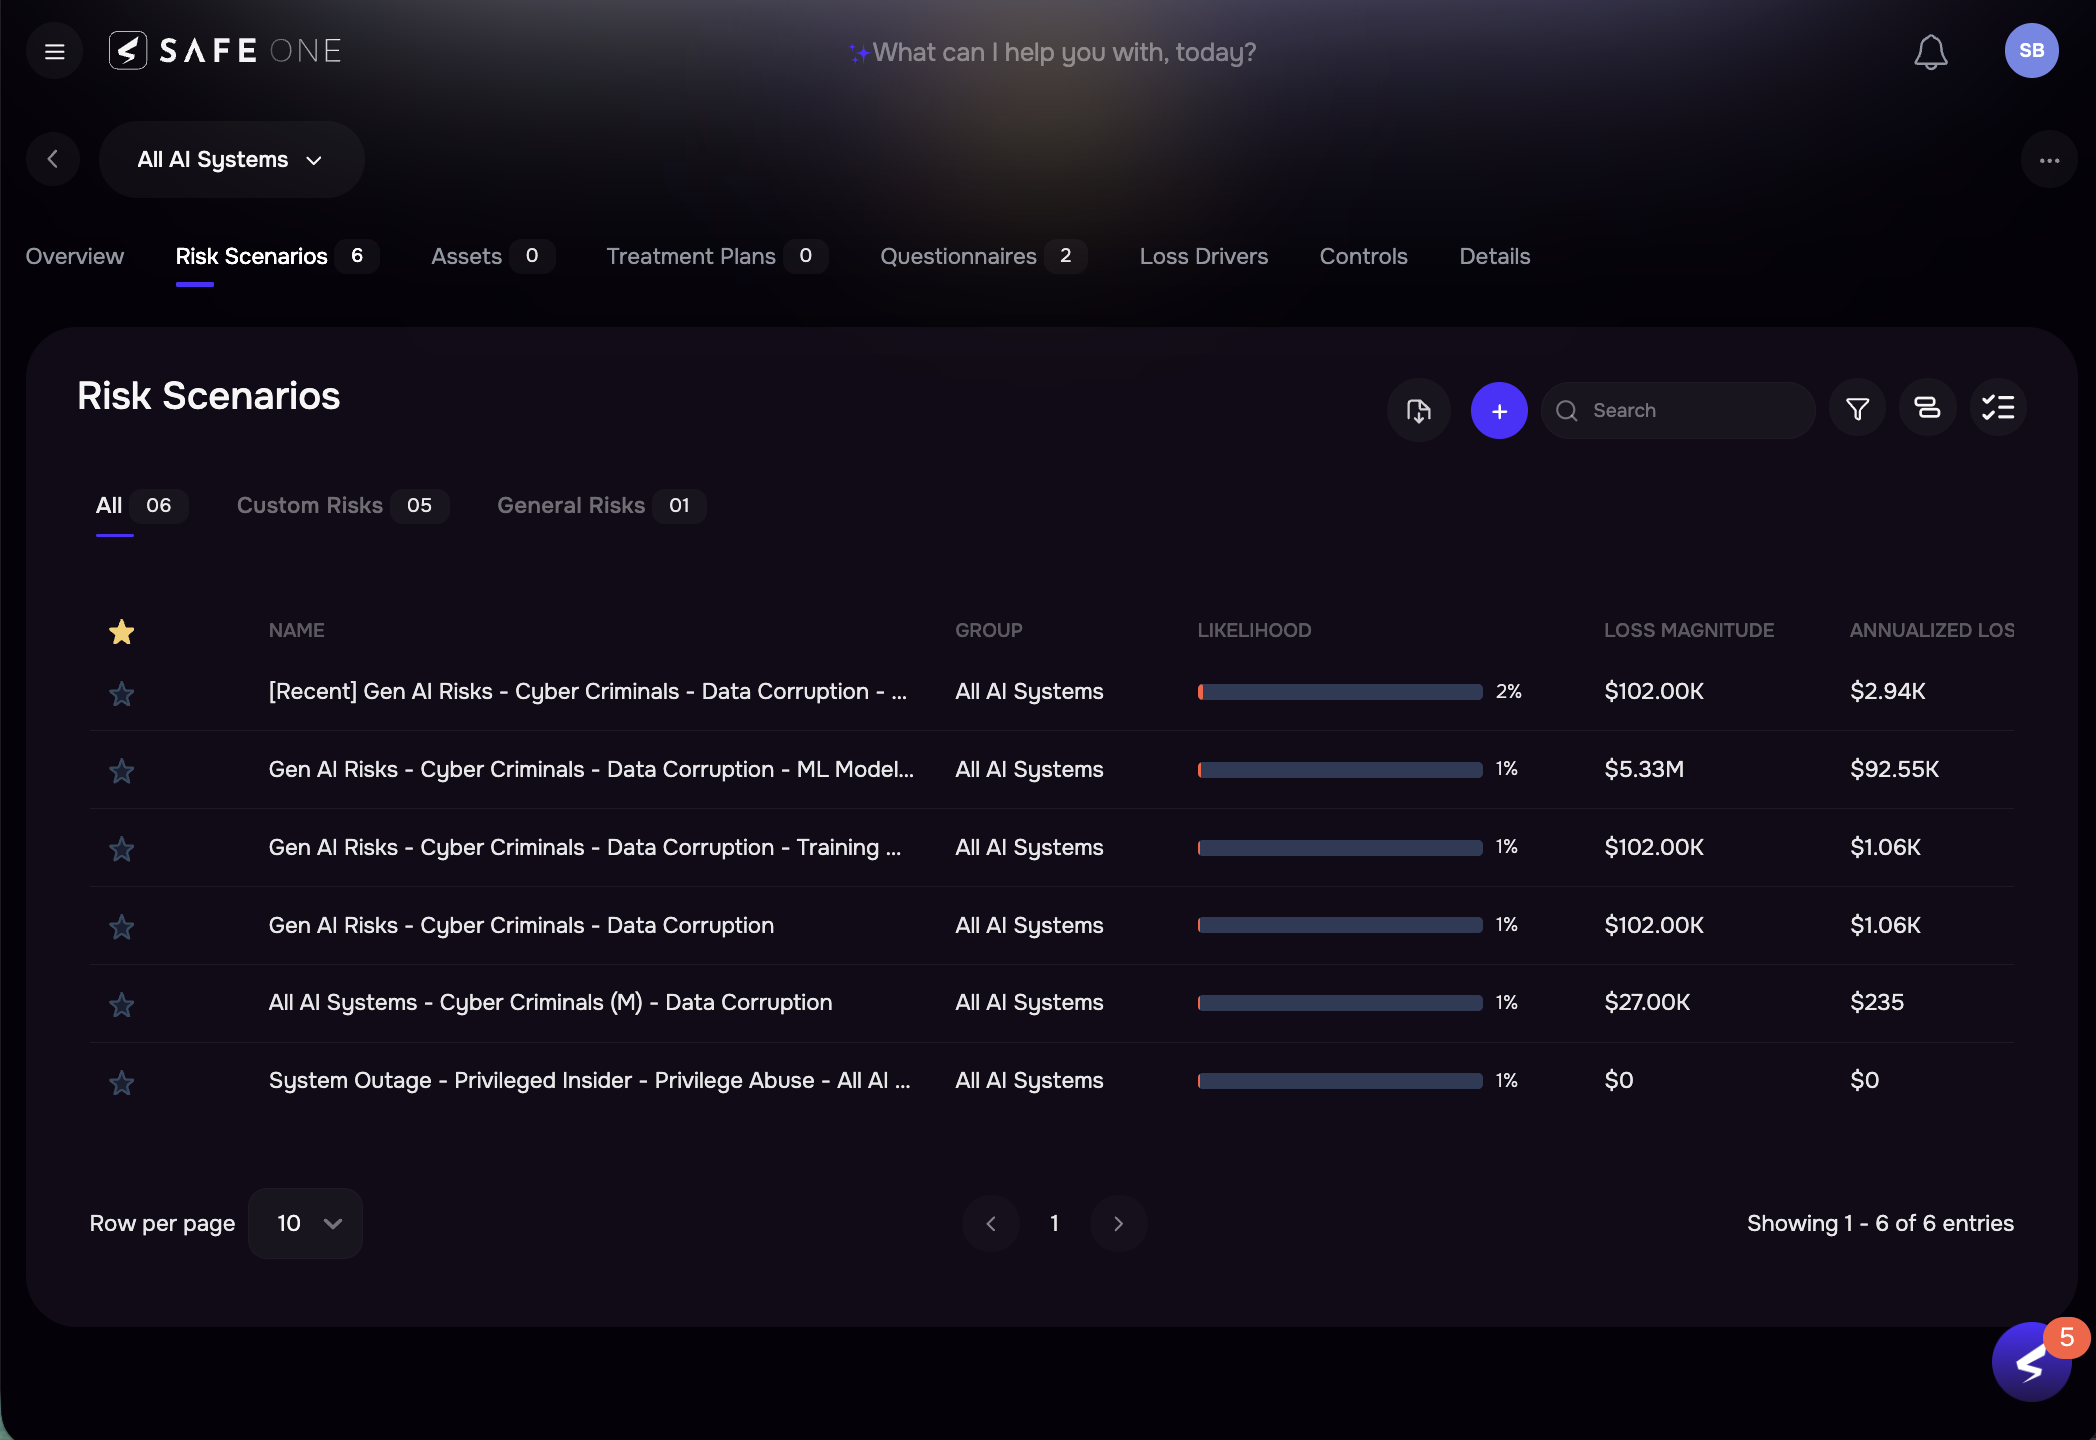
Map risk scenarios across BUs & assets to disruptions such as ransomware, data exfiltration, and more

Communicate the impact of risk in financial terms to drive informed decisions and risk reduction

Meet and report compliance and regulatory requirements

Meet strict regulatory timelines for reporting cyber incident materiality with FAIR-MAMTM

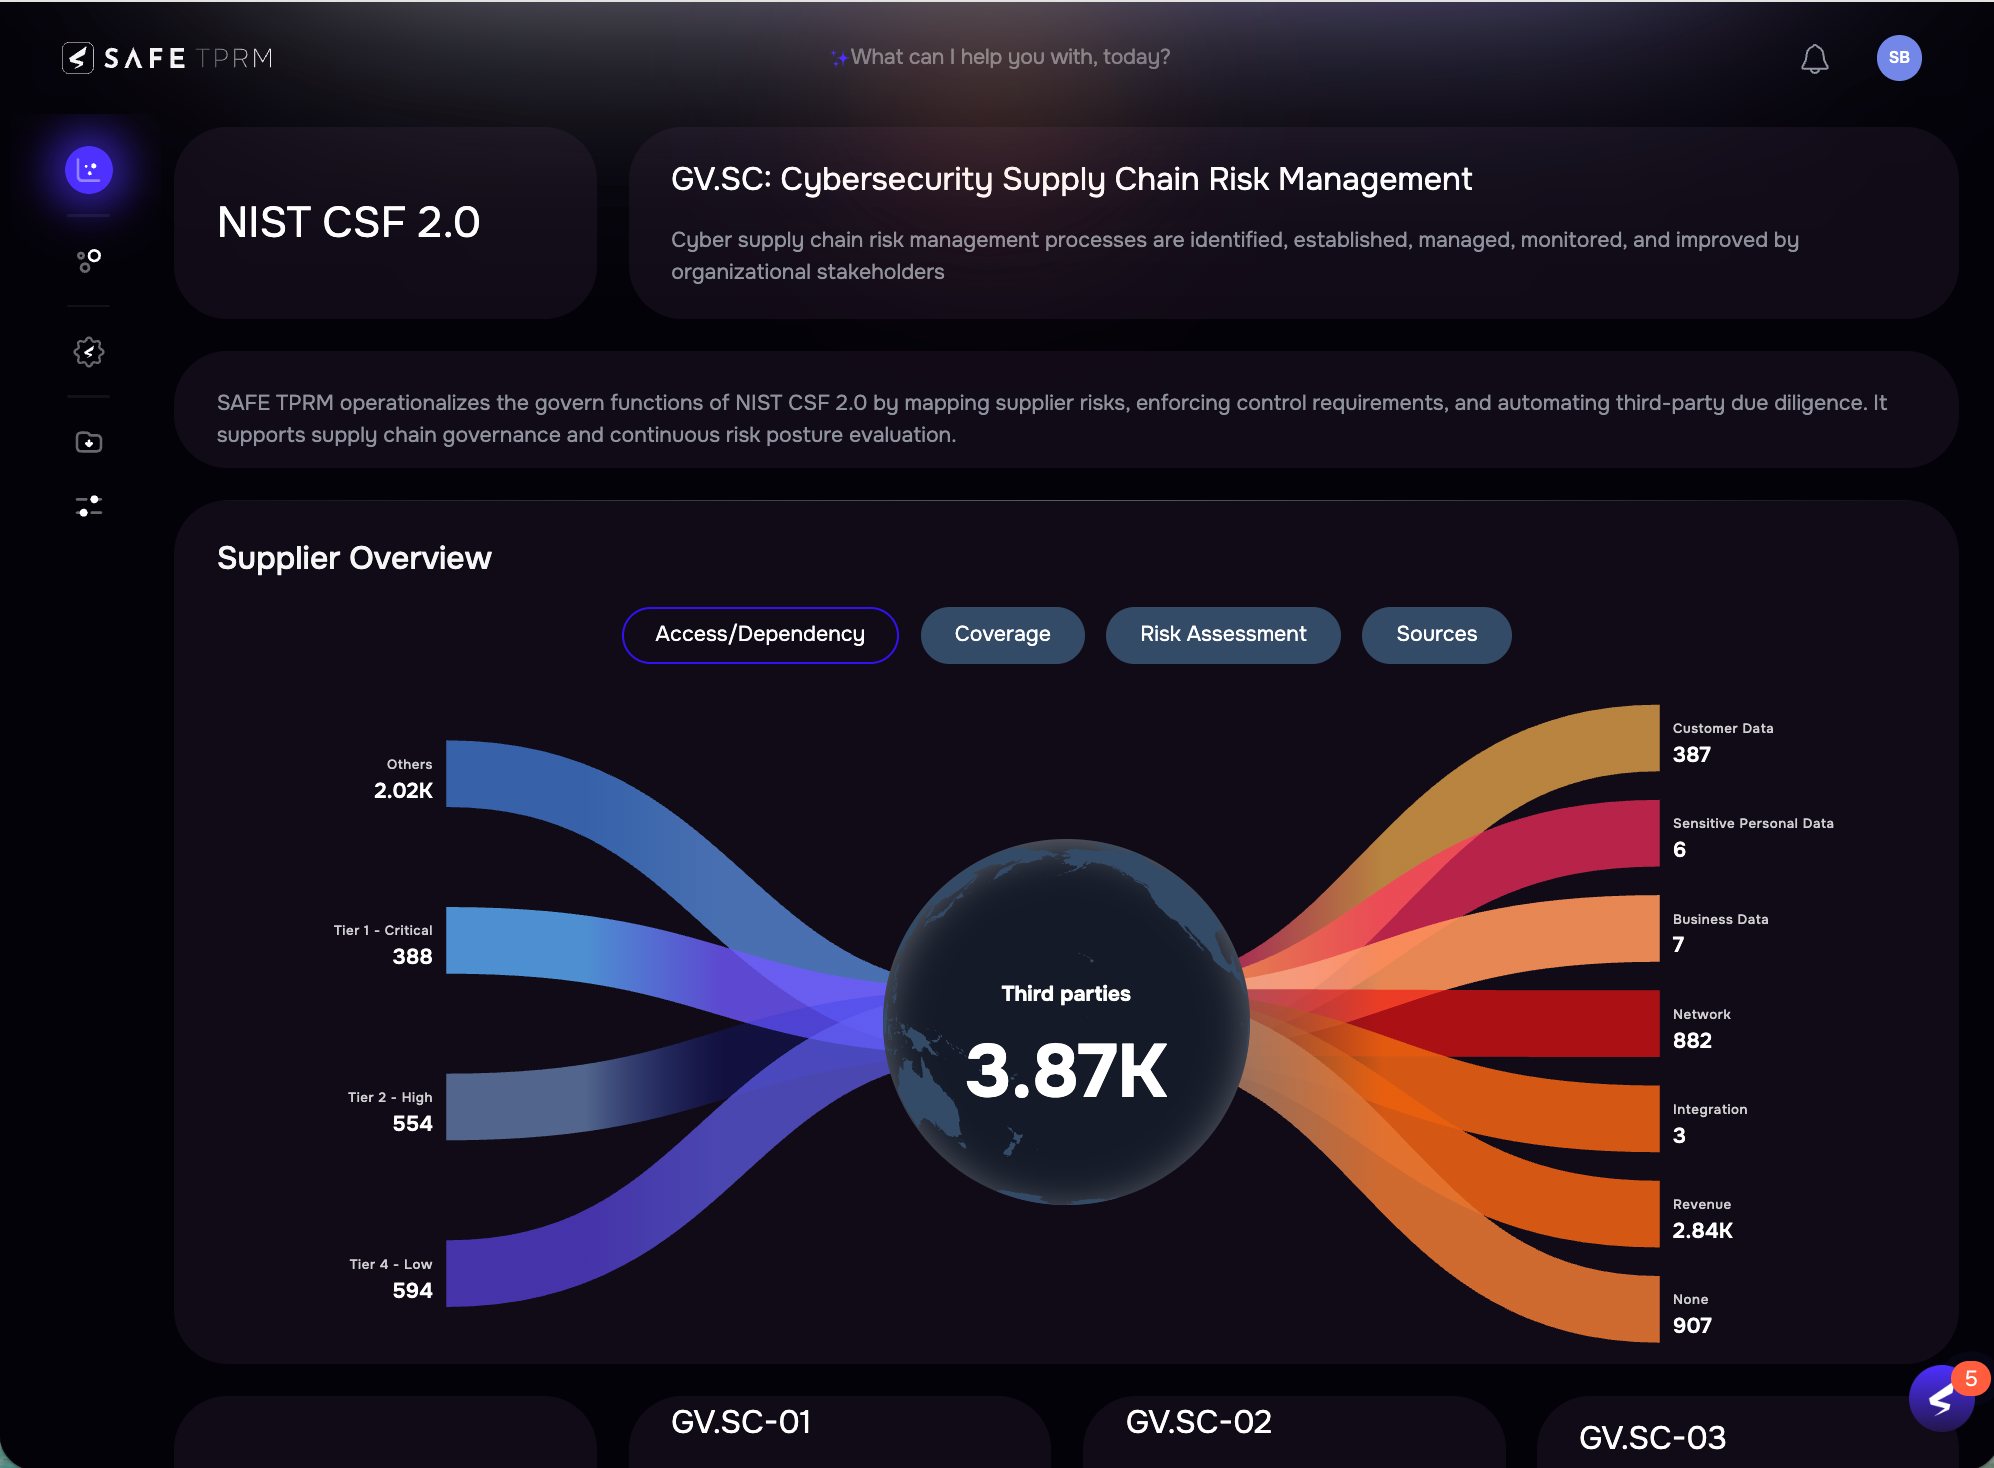
Get built-in, customizable compliance dashboards for NYDFS 500, PCI DSS, NIST, NIS2, DORA, and more

Leverage AI-powered, prompt-based reporting to generate regulatory, board, and audit-ready reports

Continuous monitoring of third-party security postures & operational resilience

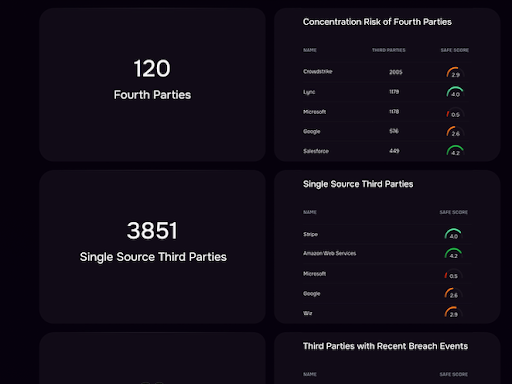
Minimize operational risk caused by vendor failures, concentration risk, and single-provider dependencies

Accelerate detection of third-party breaches to minimize disruption to critical financial services

Gain visibility into third- and fourth-party ecosystems — core banking providers, cloud platforms, and more

Accelerate & easily scale vendor onboarding & assessment

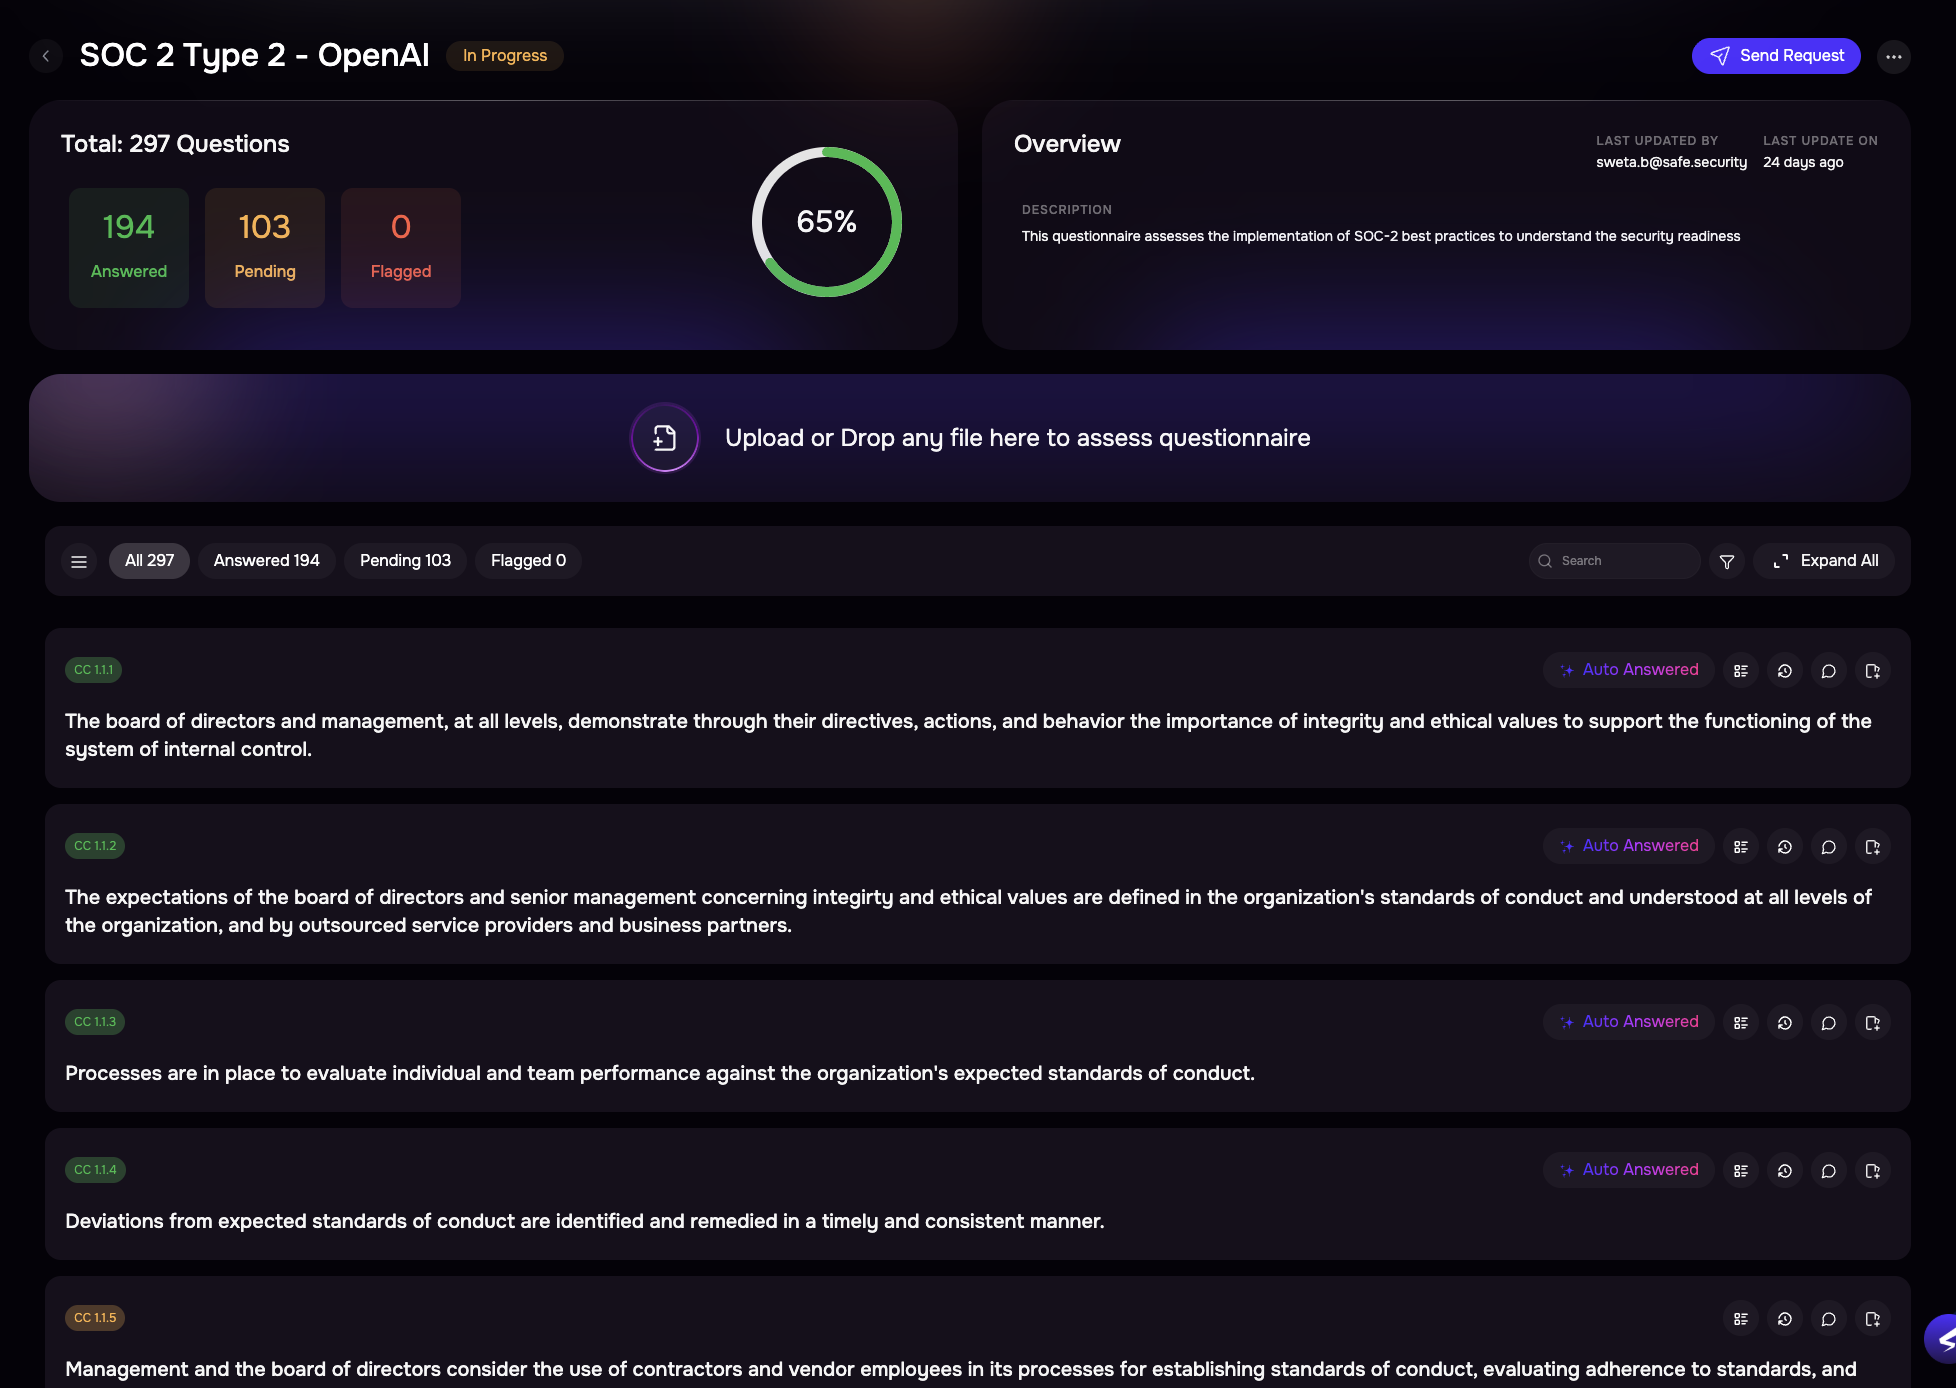
Experience autonomous TPRM, so teams focus on risks that disrupt services or create compliance exposures

Accelerate innovation by getting critical partners and service providers live in days instead of weeks

Auto-answer questionnaires and assessments, save hours of time in reconciliation to fast track risk assessments

Assess Risk Exposure to Emerging Risks including AI

Evaluate AI risk posture using the NIST AI-RMF framework to meet industry standards

Generate emerging and AI risk scenarios including risks posed by specific hacker groups

Quantify new and emerging risks via breach likelihood and loss for AI-related risk scenarios

Strategically prioritize your cybersecurity investments

Build business-unit–specific risk reduction strategies for Retail, Commercial, Payments, Capital Markets, and more

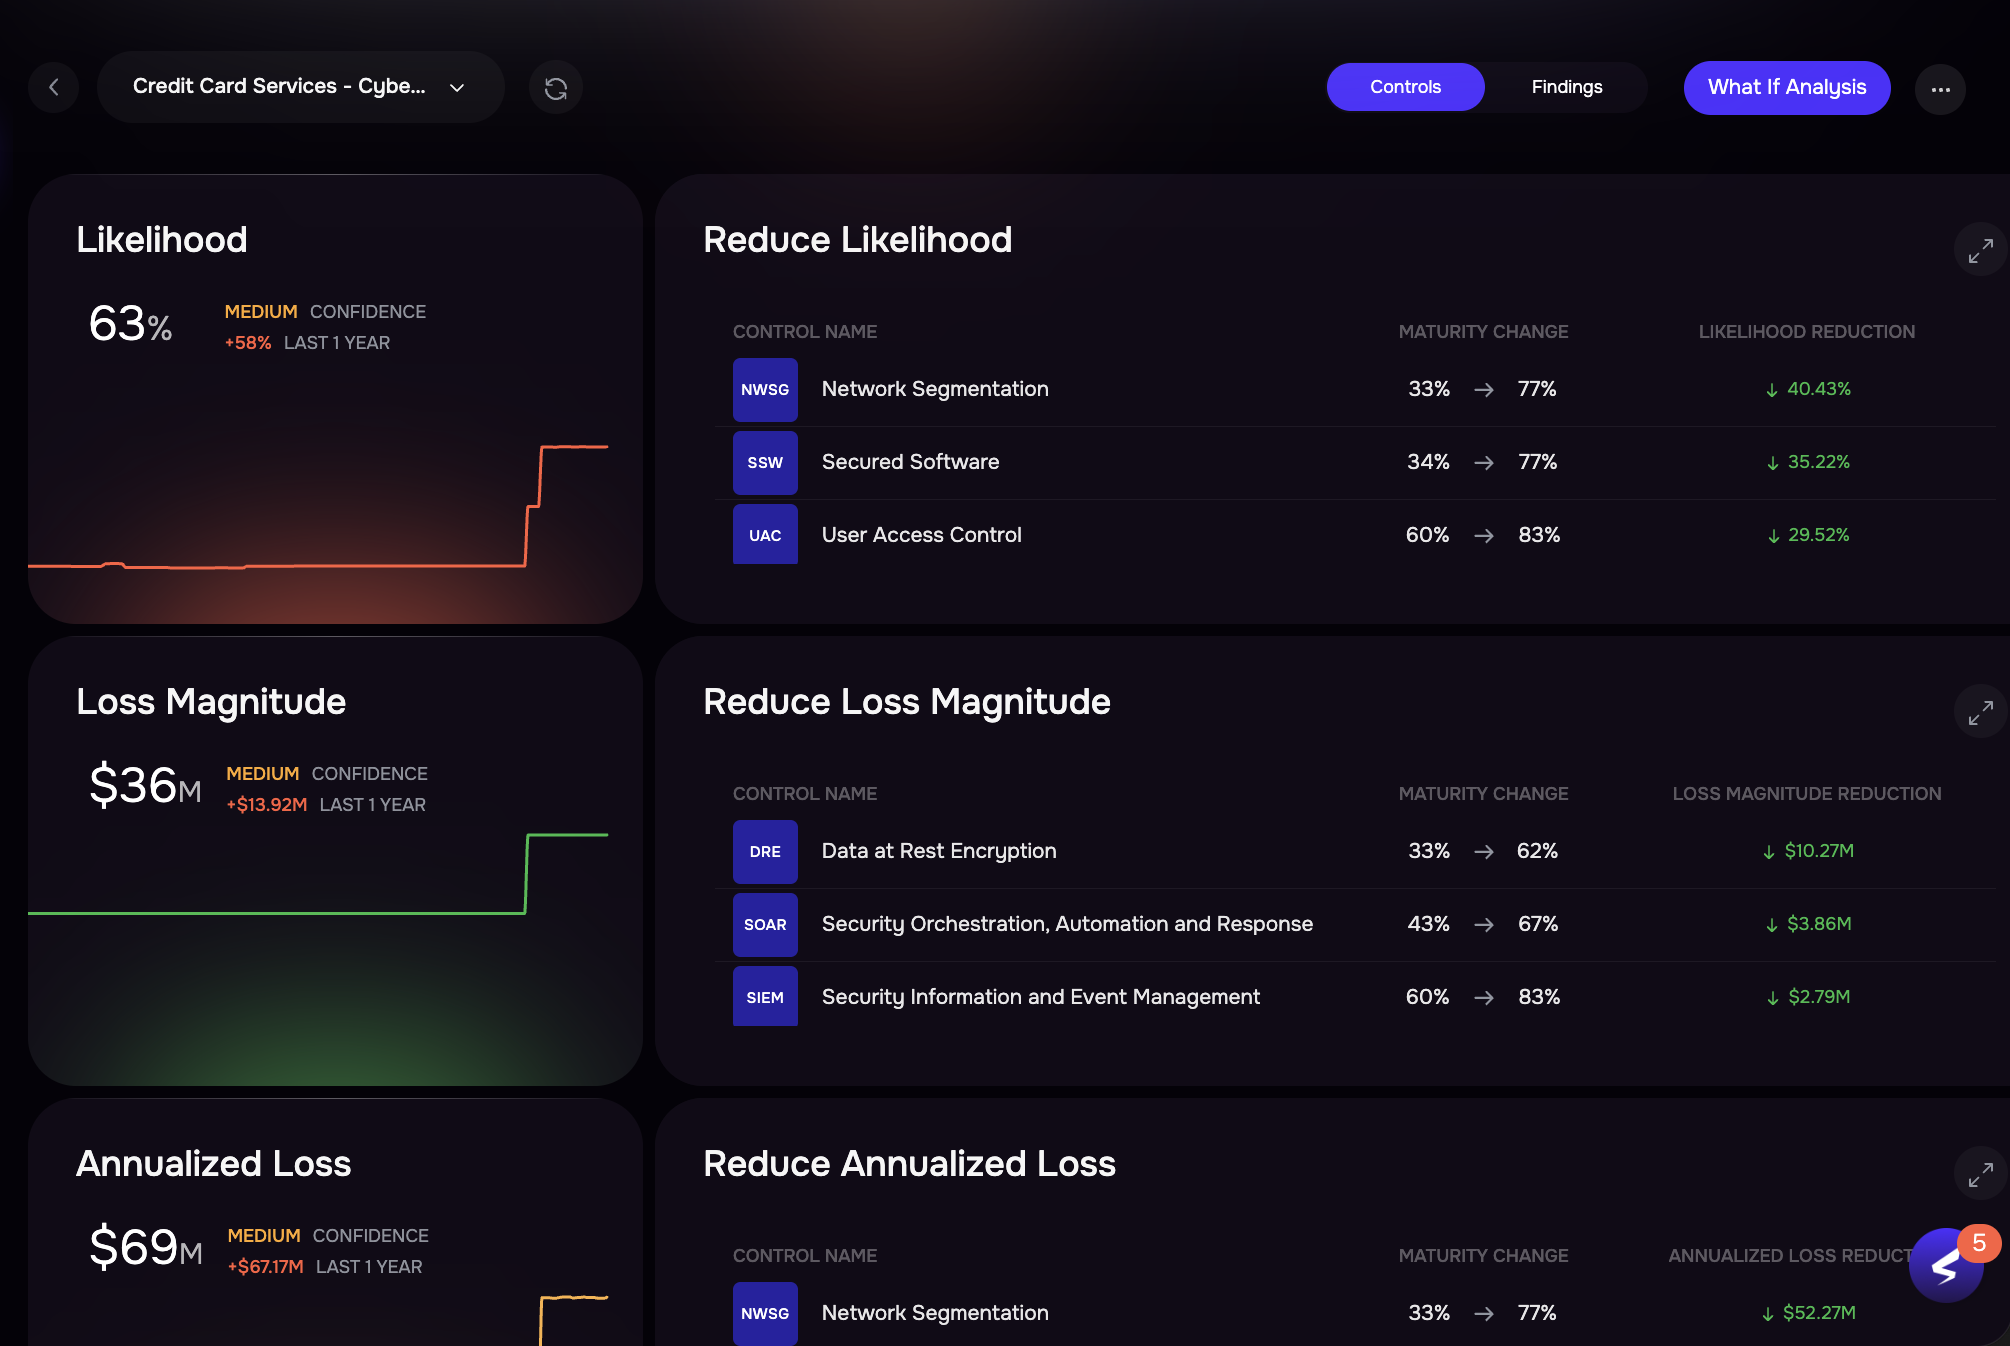
Run what-if analyses to see how changes to controls and third-party risk reduces business operations

Demonstrate the ROI of security investments that drive the greatest risk reduction to get stakeholder buy-in

The Proof

Machine-Speed Defense.
Measurable Results.

Instacart operationalizes enterprise-scale TPRM while reducing assessment effort.

Retail USA

Read the Full Story

The Challenge

Instacart’s TPRM team managed hundreds of vendors through manual processes that slowed assessments and limited visibility. They needed a more automated, risk-based approach to scale the program.

The Results

30+
hours
of analyst work eliminated per assessment
3
weeks
to operationalize TPRM with 600+ vendors
100%
vendors
assessed and monitored with zero added headcount

Trusted By 10% of Fortune 500

  • T-Mobile
  • Fannie Mae
  • Verizon
  • Delta
  • Honeywell
  • S&P Global
  • HP
  • AAA
  • ADP
  • Chipotle
  • Snap Inc.
Book a demo

Ready to Meet your
AI Co-Workers?

Get a Demo